mirror of
https://github.com/go-gost/gost.git
synced 2026-10-08 12:05:46 +00:00
Compare commits
318
Commits
| Author | SHA1 | Date | |
|---|---|---|---|
 ginuerzh |
87af3da1b6 | ||
|
ginuerzh
|
dc6fe595e0 | ||
|
ginuerzh
|
db4a0a9259 | ||
 Meng Zhuo |
62a097c5e4 | ||
|
ginuerzh
|
b51cecbbfd | ||
|
ginuerzh
|
66a260abd1 | ||
 ginuerzh |
1d3603f9ed | ||
 ravitheg |
952c61c1a2 | ||
|
ravitheg
|
6d61ab82db | ||
|
ginuerzh
|
f61bb2fd72 | ||
|
ginuerzh
|
4c2835db04 | ||
|
ginuerzh
|
d662b1fd46 | ||
|
ginuerzh
|
015923fa5d | ||
|
ginuerzh
|
f66fce9d49 | ||
|
ginuerzh
|
982a93eee4 | ||
|
ginuerzh
|
758251d3f9 | ||
|
ginuerzh
|
a1e48e164b | ||
|
ginuerzh
|
581dd74bbb | ||
|
ginuerzh
|
3c7a984aa3 | ||
|
ginuerzh
|
2a9b7e7d9b | ||
|
ginuerzh
|
ab2b9714ee | ||
|
ginuerzh
|
6d38c24d88 | ||
|
ginuerzh
|
f376db2000 | ||
|
ginuerzh
|
161d96f582 | ||
|
ginuerzh
|
128c0c3117 | ||
|
ginuerzh
|
66ce980c36 | ||
|
ginuerzh
|
829148d3f8 | ||
|
ginuerzh
|
c45f148a88 | ||
|
ginuerzh
|
fdc88af4ac | ||
|
ginuerzh
|
c41c5bf79a | ||
|
ginuerzh
|
b3eeb338fb | ||
|
ginuerzh
|
72f185bbf6 | ||
|
ginuerzh
|
a7599990a8 | ||
|
ginuerzh
|
17ca5600d3 | ||
|
ginuerzh
|
32ccfe483c | ||
|
ginuerzh
|
1d0eb06938 | ||
|
ginuerzh
|
1fa5067d14 | ||
|
ginuerzh
|
7ddfef85a5 | ||
|
ginuerzh
|
fa98777ab1 | ||
|
ginuerzh
|
e53486efe0 | ||
|
ginuerzh
|
881ebfad5b | ||
|
ginuerzh
|
d5bb691b38 | ||
|
ginuerzh
|
24c13b861a | ||
|
ginuerzh
|
d6daa8bf56 | ||
|
ginuerzh
|
d18539ef66 | ||
|
ginuerzh
|
48b0a690c5 | ||
|
ginuerzh
|
a7037a27bf | ||
|
ginuerzh
|
ac9960de6d | ||
|
ginuerzh
|
404e099907 | ||
|
ginuerzh
|
94cd590142 | ||
|
ginuerzh
|
d3809ec634 | ||
|
ginuerzh
|
efb4da6fa6 | ||
|
ginuerzh
|
2ec8584e96 | ||
|
ginuerzh
|
f05f5cf862 | ||
|
ginuerzh
|
bf3018b5b1 | ||
|
ginuerzh
|
073af6163e | ||
|
ginuerzh
|
ef07551e01 | ||
|
ginuerzh
|
8077c039f3 | ||
|
ginuerzh
|
33c8f3595a | ||
|
ginuerzh
|
87bff8cac6 | ||
|
ginuerzh
|
d52fcccf06 | ||
|
ginuerzh
|
18610d4608 | ||
|
ginuerzh
|
c1de9e4e72 | ||
|
ginuerzh
|
1f7c080043 | ||
|
ginuerzh
|
b091f72900 | ||
|
ginuerzh
|
8e50e9c085 | ||
|
ginuerzh
|
7a35d25c5c | ||
|
ginuerzh
|
8e311e7891 | ||
|
ginuerzh
|
17fc806c2d | ||
|
ginuerzh
|
b21fd4a22b | ||
|
ginuerzh
|
3e8a025c45 | ||
|
ginuerzh
|
0d7a6f8091 | ||
|
ginuerzh
|
4a2a2a00de | ||
|
ginuerzh
|
c71e128fec | ||
|
ginuerzh
|
1400b5ff5d | ||
|
ginuerzh
|
cd4fad8c08 | ||
|
ginuerzh
|
56a68ae06f | ||
|
ginuerzh
|
5d7100f749 | ||
|
ginuerzh
|
12871a4ff3 | ||
|
ginuerzh
|
6130bbc075 | ||
|
ginuerzh
|
85d4fcaf7d | ||
|
ginuerzh
|
7904e571c1 | ||
|
ginuerzh
|
8253c41de6 | ||
|
ginuerzh
|
2148d10def | ||
 Christian Groschupp |
8846c69c05 | ||
|
ginuerzh
|
2161b97064 | ||
|
ginuerzh
|
e245526b33 | ||
|
ginuerzh
|
60389894c0 | ||
 dependabot[bot] |
9ab142ac99 | ||
|
ginuerzh
|
be1b0627d1 | ||
|
dependabot[bot]
|
f4115b867d | ||
 kLiHz |
a513417d7e | ||
|
kLiHz
|
58bd3d062b | ||
|
kLiHz
|
d2b79c13a6 | ||
|
kLiHz
|
fedd7a7b07 | ||
|
kLiHz
|
27f4b6abeb | ||
|
kLiHz
|
d4aadbbc14 | ||
|
kLiHz
|
4508747635 | ||
|
dependabot[bot]
|
50844821f8 | ||
 Jalal Saberi |
29ec7c94ad | ||
|
Jalal Saberi
|
53d6706b5d | ||
|
ginuerzh
|
594418db53 | ||
|
ginuerzh
|
72cd708dfe | ||
|
ginuerzh
|
b576bb5645 | ||
|
ginuerzh
|
8c529e3595 | ||
|
ginuerzh
|
b75e133719 | ||
|
dependabot[bot]
|
abfbf23842 | ||
|
ginuerzh
|
42d62550bf | ||
|
ginuerzh
|
69ba5864ad | ||
|
ginuerzh
|
fdd3eb61c3 | ||
|
ginuerzh
|
f68bfdb149 | ||
|
ginuerzh
|
9e4bca84f1 | ||
|
ginuerzh
|
925ff89b78 | ||
|
ginuerzh
|
ca077d418a | ||
|
ginuerzh
|
7264fca4f8 | ||
|
ginuerzh
|
bc37fac037 | ||
|
ginuerzh
|
dc48c4a3b2 | ||
|
ginuerzh
|
310614663a | ||
|
ginuerzh
|
8f094d86b0 | ||
|
ginuerzh
|
638c780acd | ||
|
ginuerzh
|
1f20f199c0 | ||
|
ginuerzh
|
8dc6146f79 | ||
|
ginuerzh
|
ed29b34c68 | ||
|
ginuerzh
|
b41aea03da | ||
|
ginuerzh
|
2c17e4417d | ||
|
ginuerzh
|
ea8ff5f77a | ||
|
ginuerzh
|
6762957c65 | ||
|
ginuerzh
|
4c934cd737 | ||
|
ginuerzh
|
0d494f5ef2 | ||
|
ginuerzh
|
bf1bab7d84 | ||
|
ginuerzh
|
b8383b1076 | ||
|
ginuerzh
|
345da28f01 | ||
|
ginuerzh
|
907420d18b | ||
|
ginuerzh
|
c1437794f8 | ||
|
ginuerzh
|
c2df5650fb | ||
|
ginuerzh
|
23506579e7 | ||
|
ginuerzh
|
969db8691b | ||
|
ginuerzh
|
3b0a2f1bae | ||
|
ginuerzh
|
b2ed4ae9fd | ||
|
ginuerzh
|
b2784011d0 | ||
|
ginuerzh
|
d4e00683c3 | ||
|
ginuerzh
|
471513896d | ||
|
ginuerzh
|
6967278600 | ||
|
ginuerzh
|
2898732c20 | ||
|
dependabot[bot]
|
bb0c0450e8 | ||
|
ginuerzh
|
6bb7dfea8f | ||
|
ginuerzh
|
e27d2bc593 | ||
|
ginuerzh
|
3144d61ecd | ||
|
ginuerzh
|
e4b68d385a | ||
|
ginuerzh
|
a91300d078 | ||
|
ginuerzh
|
b8785eb71e | ||
|
ginuerzh
|
67fcd929be | ||
|
ginuerzh
|
48c262bf71 | ||
|
ginuerzh
|
05c35005e9 | ||
|
ginuerzh
|
f6112773a1 | ||
|
ginuerzh
|
61002b7c9c | ||
|
ginuerzh
|
f8a19e0829 | ||
|
ginuerzh
|
b1ace73943 | ||
|
ginuerzh
|
3d0e993498 | ||
|
ginuerzh
|
9cbc875965 | ||
|
dependabot[bot]
|
139b934fc6 | ||
|
ginuerzh
|
c1d9228eee | ||
|
ginuerzh
|
2ea7dc250a | ||
|
ginuerzh
|
be33046c16 | ||
|
ginuerzh
|
d85b8d487b | ||
|
ginuerzh
|
ab8d77bb5e | ||
|
ginuerzh
|
8640596064 | ||
|
ginuerzh
|
8a699e1906 | ||
|
ginuerzh
|
0d41f5edc8 | ||
|
ginuerzh
|
87364d2494 | ||
|
ginuerzh
|
6982b8af63 | ||
|
ginuerzh
|
0b1540b23a | ||
|
ginuerzh
|
1bbeeb7e66 | ||
|
ginuerzh
|
5d4db6e377 | ||
|
ginuerzh
|
05d06a2718 | ||
|
ginuerzh
|
420b36b2f8 | ||
|
ginuerzh
|
3883a4493a | ||
|
ginuerzh
|
355aaa7690 | ||
|
ginuerzh
|
c73c98974c | ||
 Sam Sesh |
98c9cc2821 | ||
|
127.0.0.1:443
|
b48d2c0dbc | ||
|
127.0.0.1:443
|
b7266f4660 | ||
|
Sam Sesh
|
6883c32157 | ||
|
Sam Sesh
|
f1c5f7598c | ||
|
Sam Sesh
|
c31242efbb | ||
|
dependabot[bot]
|
6ee632cee2 | ||
|
ginuerzh
|
8e2060582e | ||
|
dependabot[bot]
|
410b4ddf53 | ||
|
ginuerzh
|
0b6474d836 | ||
|
ginuerzh
|
4b6d6e7e7c | ||
|
ginuerzh
|
b2434dd05b | ||
|
ginuerzh
|
3d15dedab2 | ||
|
ginuerzh
|
436864ca92 | ||
|
ginuerzh
|
4847f9ee9f | ||
|
ginuerzh
|
a88b44d01d | ||
|
ginuerzh
|
45f1cc2efc | ||
|
ginuerzh
|
bfa1530ef6 | ||
|
ginuerzh
|
f02c9810f2 | ||
|
ginuerzh
|
fda6214c12 | ||
|
dependabot[bot]
|
acb8c5bd53 | ||
|
ginuerzh
|
3f53858c83 | ||
|
ginuerzh
|
a379565412 | ||
|
dependabot[bot]
|
69089b790f | ||
|
ginuerzh
|
1c2d9b2a5b | ||
|
ginuerzh
|
8d852b62cf | ||
|
ginuerzh
|
a80dec0dc1 | ||
|
ginuerzh
|
62ca8ff2de | ||
|
ginuerzh
|
b8504f7f28 | ||
|
ginuerzh
|
95a2f0d649 | ||
|
ginuerzh
|
d810224e7b | ||
|
ginuerzh
|
db36804bfa | ||
|
ginuerzh
|
ad8af1942d | ||
|
ginuerzh
|
3d01f74f7c | ||
|
ginuerzh
|
6b05bcb0ab | ||
|
ginuerzh
|
799c95bfb4 | ||
|
ginuerzh
|
de0a584175 | ||
|
ginuerzh
|
381b1c9bf5 | ||
|
ginuerzh
|
ed7d72bfd8 | ||
|
ginuerzh
|
98aef6ba90 | ||
|
ginuerzh
|
dfde6efdeb | ||
|
ginuerzh
|
8858598cf0 | ||
|
ginuerzh
|
c765789076 | ||
|
ginuerzh
|
cf49a3ae46 | ||
|
ginuerzh
|
fa47726c3d | ||
|
ginuerzh
|
c351b849e6 | ||
|
ginuerzh
|
44fca4e04c | ||
|
ginuerzh
|
a795923980 | ||
|
ginuerzh
|
d3283d6278 | ||
|
ginuerzh
|
4b3e711adb | ||
|
ginuerzh
|
258d9f5b26 | ||
 Carlos Ibáñez |
5d9d33f368 | ||
|
Carlos Ibáñez
|
fec33e62ea | ||
|
ginuerzh
|
2f0da6993b | ||
|
ginuerzh
|
39cb9c65d9 | ||
 segfault-bilibili |
4ef4448249 | ||
|
segfault-bilibili
|
1151ecd2a4 | ||
|
ginuerzh
|
df3533b4ef | ||
|
ginuerzh
|
2400e29fe0 | ||
|
ginuerzh
|
41bb4cdbb0 | ||
|
ginuerzh
|
4a192bc1b3 | ||
|
ginuerzh
|
f17b2d2e96 | ||
|
ginuerzh
|
e771534920 | ||
|
ginuerzh
|
68c311a7d1 | ||
|
ginuerzh
|
1c9974340b | ||
|
ginuerzh
|
09c12b013c | ||
|
ginuerzh
|
b86d7ee06d | ||
 soffchen |
8274b62672 | ||
|
ginuerzh
|
7f924fdeb6 | ||
|
ginuerzh
|
5d797eac43 | ||
|
ginuerzh
|
2c29028a3b | ||
|
ginuerzh
|
e8071d9b65 | ||
|
ginuerzh
|
50cf4edd1f | ||
|
ginuerzh
|
3d5f0f93fd | ||
|
ginuerzh
|
aa754f8515 | ||
|
ginuerzh
|
a7f4d3e63e | ||
|
ginuerzh
|
180214a124 | ||
|
ginuerzh
|
baa6f0cea0 | ||
|
ginuerzh
|
ca0de58757 | ||
|
ginuerzh
|
5acccebe7b | ||
|
ginuerzh
|
850bb1379f | ||
|
ginuerzh
|
9e404471a6 | ||
|
ginuerzh
|
166317a7d0 | ||
|
ginuerzh
|
77d9e3798c | ||
|
ginuerzh
|
5cbba69ae2 | ||
|
ginuerzh
|
8a8cbdd9e1 | ||
|
ginuerzh
|
fb5f57fa80 | ||
|
ginuerzh
|
5603af2fcf | ||
|
ginuerzh
|
8ae4e43fc3 | ||
|
ginuerzh
|
96b3b7e962 | ||
|
ginuerzh
|
85de11ae46 | ||
|
ginuerzh
|
3a409fea42 | ||
|
ginuerzh
|
1c65aae3a9 | ||
|
ginuerzh
|
84255850b6 | ||
|
ginuerzh
|
54e0091c38 | ||
|
ginuerzh
|
605c43ca08 | ||
|
ginuerzh
|
3418dd0f00 | ||
|
ginuerzh
|
21463c0e9b | ||
|
ginuerzh
|
11077eaa75 | ||
|
ginuerzh
|
9cd94cb68b | ||
|
ginuerzh
|
37ef13655d | ||
|
ginuerzh
|
961646fb46 | ||
|
ginuerzh
|
666846d352 | ||
|
ginuerzh
|
c70521ddab | ||
|
ginuerzh
|
7c91dfb56f | ||
|
ginuerzh
|
4b88c240f8 | ||
|
ginuerzh
|
1b31c80d2c | ||
|
ginuerzh
|
810f9f4d8f | ||
|
ginuerzh
|
5fe56cb63f | ||
|
ginuerzh
|
733655625a | ||
|
ginuerzh
|
670a118c6d | ||
|
ginuerzh
|
cb0d81f938 | ||
|
ginuerzh
|
7b5913123f | ||
|
ginuerzh
|
bb7fb31e3d | ||
|
ginuerzh
|
7fd8720f38 | ||
|
ginuerzh
|
815341dbfa | ||
|
ginuerzh
|
2864480296 | ||
|
ginuerzh
|
0a41b70ef4 | ||
|
ginuerzh
|
20e7528b25 | ||
|
ginuerzh
|
2e40afe535 | ||
|
ginuerzh
|
42f72adde0 | ||
|
ginuerzh
|
a2d62d1753 | ||
|
ginuerzh
|
749d802a12 | ||
|
ginuerzh
|
695c720d26 | ||
|
ginuerzh
|
c282e69ffd | ||
|
ginuerzh
|
eae153d481 | ||
|
ginuerzh
|
a7fddd1d7c | ||
|
ginuerzh
|
5c5af49b0e | ||
|
ginuerzh
|
bfc1f8472c | ||
|
ginuerzh
|
4007e80811 | ||
|
ginuerzh
|
4364190e6d | ||
|
ginuerzh
|
be374b6488 | ||
|
ginuerzh
|
ee72cea036 | ||
|
ginuerzh
|
e587b4df7c | ||
|
ginuerzh
|
8d8785f534 | ||
|
ginuerzh
|
b96d37d4cc | ||
|
ginuerzh
|
ffdf11e89e | ||
|
ginuerzh
|
07132d8de7 | ||
|
ginuerzh
|
0aee4f0ebd |
@@ -1,89 +0,0 @@
|
||||
# ref: https://docs.docker.com/ci-cd/github-actions/
|
||||
# https://blog.oddbit.com/post/2020-09-25-building-multi-architecture-im/
|
||||
|
||||
name: Docker
|
||||
|
||||
on:
|
||||
push:
|
||||
branches:
|
||||
- master
|
||||
tags:
|
||||
- 'v*'
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- name: Prepare
|
||||
id: prepare
|
||||
run: |
|
||||
DOCKER_IMAGE=${{ secrets.DOCKER_IMAGE }}
|
||||
VERSION=latest
|
||||
|
||||
# If this is git tag, use the tag name as a docker tag
|
||||
if [[ $GITHUB_REF == refs/tags/* ]]; then
|
||||
VERSION=${GITHUB_REF#refs/tags/v}
|
||||
fi
|
||||
TAGS="${DOCKER_IMAGE}:${VERSION}"
|
||||
|
||||
# If the VERSION looks like a version number, assume that
|
||||
# this is the most recent version of the image and also
|
||||
# tag it 'latest'.
|
||||
if [[ $VERSION =~ ^[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}$ ]]; then
|
||||
TAGS="$TAGS,${DOCKER_IMAGE}:latest"
|
||||
fi
|
||||
|
||||
# Set output parameters.
|
||||
echo ::set-output name=tags::${TAGS}
|
||||
echo ::set-output name=docker_image::${DOCKER_IMAGE}
|
||||
echo ::set-output name=docker_platforms::linux/386,linux/amd64,linux/arm/v6,linux/arm/v7,linux/arm64/v8,linux/ppc64le,linux/s390x
|
||||
|
||||
# https://github.com/crazy-max/ghaction-docker-buildx
|
||||
- name: Set up Docker Buildx
|
||||
id: buildx
|
||||
uses: crazy-max/ghaction-docker-buildx@v1
|
||||
with:
|
||||
version: latest
|
||||
|
||||
- name: Environment
|
||||
run: |
|
||||
echo home=$HOME
|
||||
echo git_ref=$GITHUB_REF
|
||||
echo git_sha=$GITHUB_SHA
|
||||
echo version=${{ steps.prepare.outputs.version }}
|
||||
echo image=${{ steps.prepare.outputs.docker_image }}
|
||||
echo platforms=${{ steps.prepare.outputs.docker_platforms }}
|
||||
echo avail_platforms=${{ steps.buildx.outputs.platforms }}
|
||||
|
||||
# https://github.com/actions/checkout
|
||||
- name: Checkout
|
||||
uses: actions/checkout@v2
|
||||
|
||||
- name: Docker Buildx (no push)
|
||||
run: |
|
||||
docker buildx bake \
|
||||
--set ${{ github.event.repository.name }}.platform=${{ steps.prepare.outputs.docker_platforms }} \
|
||||
--set ${{ github.event.repository.name }}.output=type=image,push=false \
|
||||
--set ${{ github.event.repository.name }}.tags="${{ steps.prepare.outputs.tags }}" \
|
||||
--file docker-compose.yaml
|
||||
|
||||
- name: Docker Login
|
||||
if: success()
|
||||
env:
|
||||
DOCKER_PASSWORD: ${{ secrets.DOCKER_PASSWORD }}
|
||||
run: |
|
||||
echo "${DOCKER_PASSWORD}" | docker login --username "${{ secrets.DOCKER_USERNAME }}" --password-stdin
|
||||
|
||||
- name: Docker Buildx (push)
|
||||
if: success()
|
||||
run: |
|
||||
docker buildx bake \
|
||||
--set ${{ github.event.repository.name }}.platform=${{ steps.prepare.outputs.docker_platforms }} \
|
||||
--set ${{ github.event.repository.name }}.output=type=image,push=true \
|
||||
--set ${{ github.event.repository.name }}.tags="${{ steps.prepare.outputs.tags }}" \
|
||||
--file docker-compose.yaml
|
||||
|
||||
- name: Clear
|
||||
if: always()
|
||||
run: |
|
||||
rm -f ${HOME}/.docker/config.json
|
||||
@@ -0,0 +1,69 @@
|
||||
# ref: https://docs.docker.com/ci-cd/github-actions/
|
||||
# https://blog.oddbit.com/post/2020-09-25-building-multi-architecture-im/
|
||||
|
||||
name: docker
|
||||
|
||||
on:
|
||||
push:
|
||||
branches:
|
||||
- master
|
||||
tags:
|
||||
- 'v*'
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- name: Prepare
|
||||
id: prepare
|
||||
run: |
|
||||
DOCKER_IMAGE=${{ secrets.DOCKER_IMAGE }}
|
||||
VERSION=latest
|
||||
|
||||
# If this is git tag, use the tag name as a docker tag
|
||||
if [[ $GITHUB_REF == refs/tags/* ]]; then
|
||||
VERSION=${GITHUB_REF#refs/tags/v}
|
||||
fi
|
||||
TAGS="${DOCKER_IMAGE}:${VERSION}"
|
||||
|
||||
# If the VERSION looks like a version number, assume that
|
||||
# this is the most recent version of the image and also
|
||||
# tag it 'latest'.
|
||||
if [[ $VERSION =~ ^[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}$ ]]; then
|
||||
MAJOR_VERSION=`echo $VERSION | awk '{split($0,a,"."); print a[1]}'`
|
||||
MINOR_VERSION=`echo $VERSION | awk '{split($0,a,"."); print a[2]}'`
|
||||
TAGS="$TAGS,${DOCKER_IMAGE}:${MAJOR_VERSION},${DOCKER_IMAGE}:${MAJOR_VERSION}.${MINOR_VERSION},${DOCKER_IMAGE}:latest"
|
||||
fi
|
||||
|
||||
# Set output parameters.
|
||||
echo "tags=${TAGS}" >> $GITHUB_OUTPUT
|
||||
echo "docker_image=${DOCKER_IMAGE}" >> $GITHUB_OUTPUT
|
||||
echo "docker_platforms=linux/386,linux/amd64,linux/arm/v6,linux/arm/v7,linux/arm64/v8,linux/s390x,linux/riscv64" >> $GITHUB_OUTPUT
|
||||
|
||||
- name: Set up Docker Buildx
|
||||
id: buildx
|
||||
uses: docker/setup-buildx-action@v3
|
||||
|
||||
- name: Environment
|
||||
run: |
|
||||
echo home=$HOME
|
||||
echo git_ref=$GITHUB_REF
|
||||
echo git_sha=$GITHUB_SHA
|
||||
echo image=${{ steps.prepare.outputs.docker_image }}
|
||||
echo tags=${{ steps.prepare.outputs.tags }}
|
||||
echo platforms=${{ steps.prepare.outputs.docker_platforms }}
|
||||
echo avail_platforms=${{ steps.buildx.outputs.platforms }}
|
||||
|
||||
- name: Login to DockerHub
|
||||
if: github.event_name != 'pull_request'
|
||||
uses: docker/login-action@v3
|
||||
with:
|
||||
username: ${{ secrets.DOCKER_USERNAME }}
|
||||
password: ${{ secrets.DOCKER_PASSWORD }}
|
||||
|
||||
- name: Buildx and push
|
||||
uses: docker/build-push-action@v6
|
||||
with:
|
||||
platforms: ${{ steps.prepare.outputs.docker_platforms }}
|
||||
push: true
|
||||
tags: ${{ steps.prepare.outputs.tags }}
|
||||
@@ -0,0 +1,38 @@
|
||||
name: goreleaser
|
||||
|
||||
on:
|
||||
push:
|
||||
# run only against tags
|
||||
tags:
|
||||
- 'v*'
|
||||
|
||||
permissions:
|
||||
contents: write
|
||||
# packages: write
|
||||
# issues: write
|
||||
|
||||
jobs:
|
||||
goreleaser:
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- uses: actions/checkout@v4
|
||||
with:
|
||||
fetch-depth: 0
|
||||
- run: git fetch --force --tags
|
||||
- uses: actions/setup-go@v5
|
||||
with:
|
||||
go-version: '1.24'
|
||||
cache: true
|
||||
# More assembly might be required: Docker logins, GPG, etc. It all depends
|
||||
# on your needs.
|
||||
- uses: goreleaser/goreleaser-action@v6
|
||||
with:
|
||||
# either 'goreleaser' (default) or 'goreleaser-pro':
|
||||
distribution: goreleaser
|
||||
version: '~> v2'
|
||||
args: release --clean
|
||||
env:
|
||||
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
|
||||
# Your GoReleaser Pro key, if you are using the 'goreleaser-pro'
|
||||
# distribution:
|
||||
# GORELEASER_KEY: ${{ secrets.GORELEASER_KEY }}
|
||||
@@ -0,0 +1,60 @@
|
||||
name: Trigger nightly build
|
||||
|
||||
on:
|
||||
schedule:
|
||||
# * is a special character in YAML, so you have to quote this string
|
||||
- cron: '30 15 * * *'
|
||||
workflow_dispatch:
|
||||
|
||||
jobs:
|
||||
check_date:
|
||||
runs-on: ubuntu-latest
|
||||
name: Check latest commit
|
||||
outputs:
|
||||
should_run: ${{ steps.should_run.outputs.should_run }}
|
||||
steps:
|
||||
- uses: actions/checkout@v4
|
||||
- name: print latest_commit
|
||||
run: echo ${{ github.sha }}
|
||||
- id: should_run
|
||||
continue-on-error: true
|
||||
name: check latest commit is less than a day
|
||||
if: ${{ github.event_name == 'schedule' }}
|
||||
run: test -z $(git rev-list --after="24 hours" ${{ github.sha }}) && echo "should_run=false" >> $GITHUB_OUTPUT
|
||||
|
||||
trigger-nightly:
|
||||
needs: check_date
|
||||
if: ${{ needs.check_date.outputs.should_run != 'false' }}
|
||||
name: Push tag for nightly build
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
-
|
||||
name: 'Checkout'
|
||||
uses: actions/checkout@v4
|
||||
with:
|
||||
token: ${{ secrets.NIGHTLY_BUILD_GH_TOKEN }}
|
||||
fetch-depth: 0
|
||||
-
|
||||
name: 'Push new tag'
|
||||
run: |
|
||||
git config user.name "${GITHUB_ACTOR}"
|
||||
git config user.email "${GITHUB_ACTOR}@users.noreply.github.com"
|
||||
|
||||
# A previous release was created using a lightweight tag
|
||||
# git describe by default includes only annotated tags
|
||||
# git describe --tags includes lightweight tags as well
|
||||
DESCRIBE=`git tag -l --sort=-v:refname | grep -v nightly | head -n 1`
|
||||
MAJOR_VERSION=`echo $DESCRIBE | awk '{split($0,a,"."); print a[1]}'`
|
||||
MINOR_VERSION=`echo $DESCRIBE | awk '{split($0,a,"."); print a[2]}'`
|
||||
# MINOR_VERSION="$((${MINOR_VERSION} + 1))"
|
||||
TAG="${MAJOR_VERSION}.${MINOR_VERSION}.0-nightly.$(date +'%Y%m%d')"
|
||||
git tag -a $TAG -m "$TAG: nightly build"
|
||||
git push origin $TAG
|
||||
- name: 'Clean up nightly releases'
|
||||
uses: dev-drprasad/delete-older-releases@v0.3.3
|
||||
with:
|
||||
keep_latest: 2
|
||||
delete_tags: true
|
||||
delete_tag_pattern: nightly
|
||||
env:
|
||||
GITHUB_TOKEN: ${{ secrets.NIGHTLY_BUILD_GH_TOKEN }}
|
||||
+4
-1
@@ -34,4 +34,7 @@ _testmain.go
|
||||
cmd/gost/gost
|
||||
snap
|
||||
|
||||
*.pem
|
||||
*.pem
|
||||
*.yaml
|
||||
*.txt
|
||||
dist/
|
||||
|
||||
@@ -0,0 +1,65 @@
|
||||
# This is an example .goreleaser.yml file with some sensible defaults.
|
||||
# Make sure to check the documentation at https://goreleaser.com
|
||||
before:
|
||||
hooks:
|
||||
# You may remove this if you don't use go modules.
|
||||
- go mod tidy
|
||||
# you may remove this if you don't need go generate
|
||||
# - go generate ./...
|
||||
builds:
|
||||
- env:
|
||||
- CGO_ENABLED=0
|
||||
main: ./cmd/gost
|
||||
targets:
|
||||
- darwin_amd64
|
||||
- darwin_arm64
|
||||
- linux_386
|
||||
- linux_amd64
|
||||
- linux_amd64_v3
|
||||
- linux_arm_5
|
||||
- linux_arm_6
|
||||
- linux_arm_7
|
||||
- linux_arm64
|
||||
- linux_mips_softfloat
|
||||
- linux_mips_hardfloat
|
||||
- linux_mipsle_softfloat
|
||||
- linux_mipsle_hardfloat
|
||||
- linux_mips64
|
||||
- linux_mips64le
|
||||
- linux_s390x
|
||||
- linux_riscv64
|
||||
- linux_loong64
|
||||
- freebsd_386
|
||||
- freebsd_amd64
|
||||
- windows_386
|
||||
- windows_amd64
|
||||
- windows_amd64_v3
|
||||
- windows_arm64
|
||||
ldflags:
|
||||
- "-s -w -X 'main.version={{ .Tag }}'"
|
||||
|
||||
archives:
|
||||
- format: tar.gz
|
||||
# use zip for windows archives
|
||||
format_overrides:
|
||||
- goos: windows
|
||||
format: zip
|
||||
checksum:
|
||||
name_template: 'checksums.txt'
|
||||
snapshot:
|
||||
name_template: "{{ incpatch .Version }}-next"
|
||||
changelog:
|
||||
sort: asc
|
||||
filters:
|
||||
exclude:
|
||||
- '^docs:'
|
||||
- '^test:'
|
||||
|
||||
release:
|
||||
prerelease: auto
|
||||
mode: keep-existing
|
||||
|
||||
# The lines beneath this are called `modelines`. See `:help modeline`
|
||||
# Feel free to remove those if you don't want/use them.
|
||||
# yaml-language-server: $schema=https://goreleaser.com/static/schema.json
|
||||
# vim: set ts=2 sw=2 tw=0 fo=cnqoj
|
||||
+18
-12
@@ -1,26 +1,32 @@
|
||||
FROM --platform=$BUILDPLATFORM golang:1.17.7-alpine as builder
|
||||
# FROM --platform=$BUILDPLATFORM golang:1.18-rc-alpine as builder
|
||||
FROM --platform=$BUILDPLATFORM tonistiigi/xx:1.6.1 AS xx
|
||||
|
||||
# Convert TARGETPLATFORM to GOARCH format
|
||||
# https://github.com/tonistiigi/xx
|
||||
COPY --from=tonistiigi/xx:golang / /
|
||||
FROM --platform=$BUILDPLATFORM golang:1.24-alpine3.22 AS builder
|
||||
|
||||
COPY --from=xx / /
|
||||
|
||||
ARG TARGETPLATFORM
|
||||
|
||||
RUN apk add --no-cache musl-dev git gcc
|
||||
RUN xx-info env
|
||||
|
||||
ADD . /src
|
||||
ENV CGO_ENABLED=0
|
||||
|
||||
WORKDIR /src
|
||||
ENV XX_VERIFY_STATIC=1
|
||||
|
||||
ENV GO111MODULE=on
|
||||
WORKDIR /app
|
||||
|
||||
RUN cd cmd/gost && go env && go build
|
||||
COPY . .
|
||||
|
||||
FROM alpine:latest
|
||||
RUN cd cmd/gost && \
|
||||
xx-go build && \
|
||||
xx-verify gost
|
||||
|
||||
FROM alpine:3.22
|
||||
|
||||
# add iptables for tun/tap
|
||||
RUN apk add --no-cache iptables
|
||||
|
||||
WORKDIR /bin/
|
||||
|
||||
COPY --from=builder /src/cmd/gost/gost .
|
||||
COPY --from=builder /app/cmd/gost/gost .
|
||||
|
||||
ENTRYPOINT ["/bin/gost"]
|
||||
@@ -9,6 +9,7 @@ PLATFORM_LIST = \
|
||||
darwin-arm64 \
|
||||
linux-386 \
|
||||
linux-amd64 \
|
||||
linux-amd64v3 \
|
||||
linux-armv5 \
|
||||
linux-armv6 \
|
||||
linux-armv7 \
|
||||
@@ -20,12 +21,15 @@ PLATFORM_LIST = \
|
||||
linux-mips64 \
|
||||
linux-mips64le \
|
||||
linux-s390x \
|
||||
linux-riscv64 \
|
||||
freebsd-386 \
|
||||
freebsd-amd64
|
||||
|
||||
WINDOWS_ARCH_LIST = \
|
||||
windows-386 \
|
||||
windows-amd64
|
||||
windows-amd64 \
|
||||
windows-amd64v3 \
|
||||
windows-arm64
|
||||
|
||||
all: linux-amd64 darwin-amd64 darwin-arm64 windows-amd64 # Most used
|
||||
|
||||
@@ -41,6 +45,9 @@ linux-386:
|
||||
linux-amd64:
|
||||
GOARCH=amd64 GOOS=linux $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
linux-amd64v3:
|
||||
GOARCH=amd64 GOOS=linux GOAMD64=v3 $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
linux-armv5:
|
||||
GOARCH=arm GOOS=linux GOARM=5 $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
@@ -74,6 +81,9 @@ linux-mips64le:
|
||||
linux-s390x:
|
||||
GOARCH=s390x GOOS=linux $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
linux-riscv64:
|
||||
GOARCH=riscv64 GOOS=linux $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
freebsd-386:
|
||||
GOARCH=386 GOOS=freebsd $(GOBUILD) -o $(BINDIR)/$(NAME)-$@ $(GOFILES)
|
||||
|
||||
@@ -86,6 +96,12 @@ windows-386:
|
||||
windows-amd64:
|
||||
GOARCH=amd64 GOOS=windows $(GOBUILD) -o $(BINDIR)/$(NAME)-$@.exe $(GOFILES)
|
||||
|
||||
windows-amd64v3:
|
||||
GOARCH=amd64 GOOS=windows GOAMD64=v3 $(GOBUILD) -o $(BINDIR)/$(NAME)-$@.exe $(GOFILES)
|
||||
|
||||
windows-arm64:
|
||||
GOARCH=arm64 GOOS=windows $(GOBUILD) -o $(BINDIR)/$(NAME)-$@.exe $(GOFILES)
|
||||
|
||||
gz_releases=$(addsuffix .gz, $(PLATFORM_LIST))
|
||||
zip_releases=$(addsuffix .zip, $(WINDOWS_ARCH_LIST))
|
||||
|
||||
|
||||
@@ -1,4 +1,106 @@
|
||||
gost 3.0
|
||||
======
|
||||
# GO Simple Tunnel
|
||||
|
||||
WORK IN PROGRESS...
|
||||
### GO语言实现的安全隧道
|
||||
|
||||
[](README.md) [](README_en.md)
|
||||
|
||||
## 功能特性
|
||||
|
||||
- [x] [多端口监听](https://gost.run/getting-started/quick-start/)
|
||||
- [x] [多级转发链](https://gost.run/concepts/chain/)
|
||||
- [x] [多协议支持](https://gost.run/tutorials/protocols/overview/)
|
||||
- [x] [TCP/UDP端口转发](https://gost.run/tutorials/port-forwarding/)
|
||||
- [x] [反向代理](https://gost.run/tutorials/reverse-proxy/)和[隧道](https://gost.run/tutorials/reverse-proxy-tunnel/)
|
||||
- [x] [TCP/UDP透明代理](https://gost.run/tutorials/redirect/)
|
||||
- [x] DNS[解析](https://gost.run/concepts/resolver/)和[代理](https://gost.run/tutorials/dns/)
|
||||
- [x] [TUN/TAP设备](https://gost.run/tutorials/tuntap/)
|
||||
- [x] [负载均衡](https://gost.run/concepts/selector/)
|
||||
- [x] [路由控制](https://gost.run/concepts/bypass/)
|
||||
- [x] [准入控制](https://gost.run/concepts/admission/)
|
||||
- [x] [限速限流](https://gost.run/concepts/limiter/)
|
||||
- [x] [插件系统](https://gost.run/concepts/plugin/)
|
||||
- [x] [Prometheus监控指标](https://gost.run/tutorials/metrics/)
|
||||
- [x] [动态配置](https://gost.run/tutorials/api/config/)
|
||||
- [x] [Web API](https://gost.run/tutorials/api/overview/)
|
||||
- [x] [GUI](https://github.com/go-gost/gostctl)/[WebUI](https://github.com/go-gost/gost-ui)
|
||||
|
||||
## 概览
|
||||
|
||||
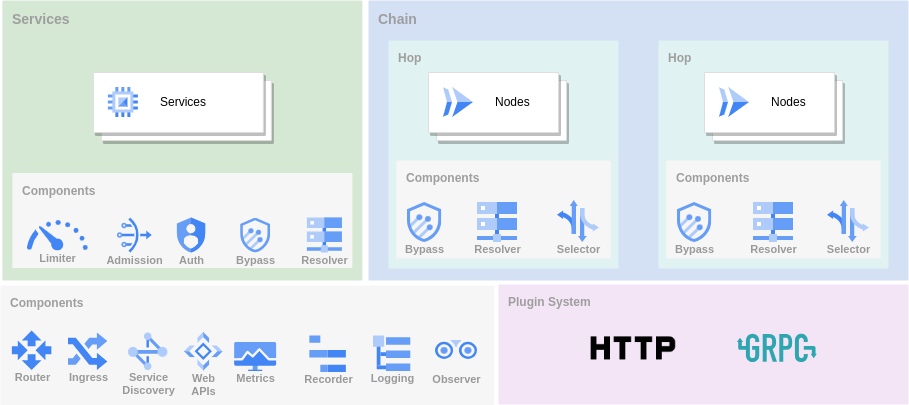
|
||||
|
||||
GOST作为隧道有三种主要使用方式。
|
||||
|
||||
### 正向代理
|
||||
|
||||
作为代理服务访问网络,可以组合使用多种协议组成转发链进行转发。
|
||||
|
||||
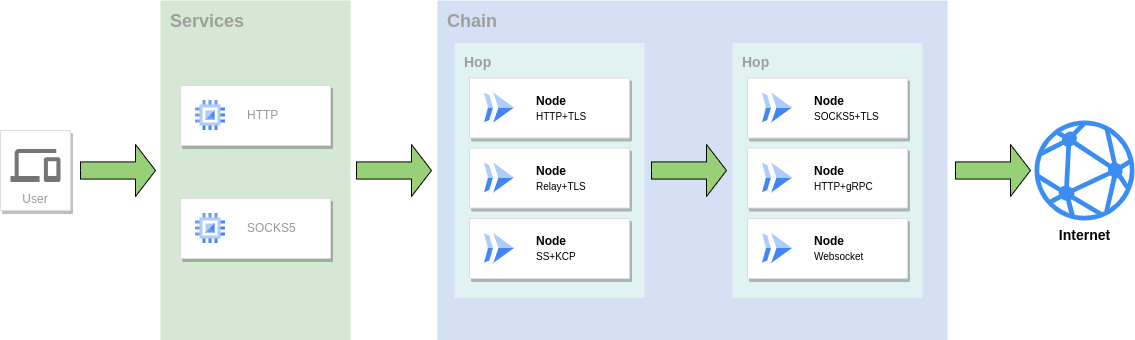
|
||||
|
||||
### 端口转发
|
||||
|
||||
将一个服务的端口映射到另外一个服务的端口,同样可以组合使用多种协议组成转发链进行转发。
|
||||
|
||||
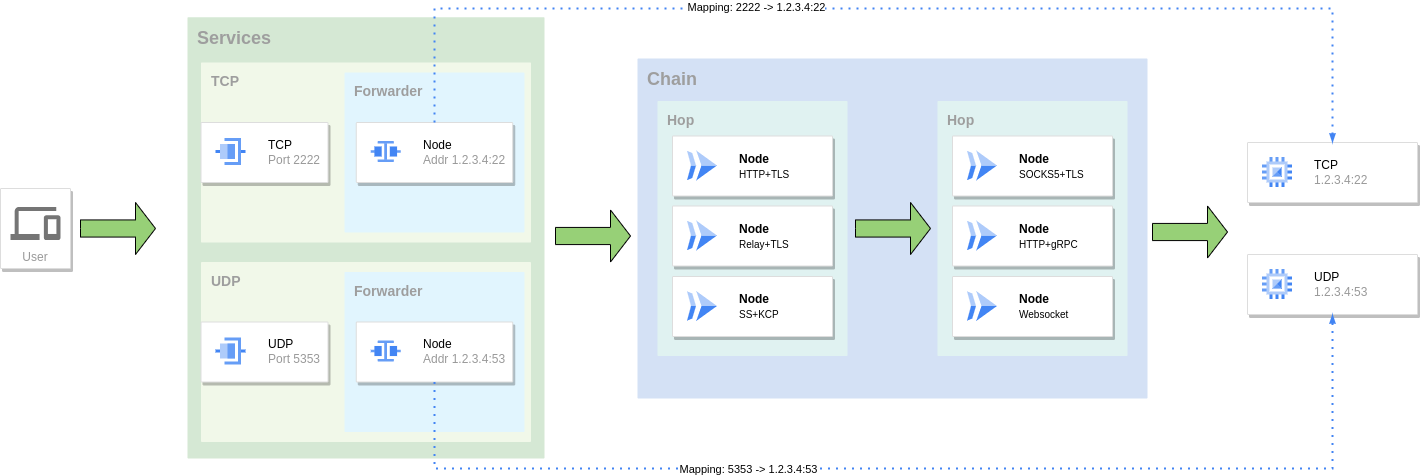
|
||||
|
||||
### 反向代理
|
||||
|
||||
利用隧道和内网穿透将内网服务暴露到公网访问。
|
||||
|
||||
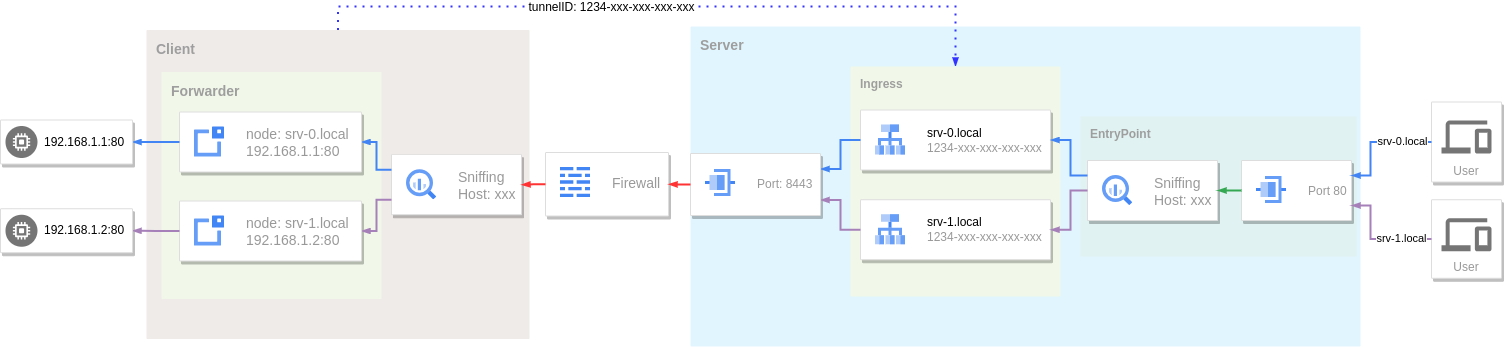
|
||||
|
||||
## 下载安装
|
||||
|
||||
### 二进制文件
|
||||
|
||||
[https://github.com/go-gost/gost/releases](https://github.com/go-gost/gost/releases)
|
||||
|
||||
### 安装脚本
|
||||
|
||||
```bash
|
||||
# 安装最新版本 [https://github.com/go-gost/gost/releases](https://github.com/go-gost/gost/releases)
|
||||
bash <(curl -fsSL https://github.com/go-gost/gost/raw/master/install.sh) --install
|
||||
```
|
||||
```bash
|
||||
# 选择要安装的版本
|
||||
bash <(curl -fsSL https://github.com/go-gost/gost/raw/master/install.sh)
|
||||
```
|
||||
|
||||
### 源码编译
|
||||
|
||||
```
|
||||
git clone https://github.com/go-gost/gost.git
|
||||
cd gost/cmd/gost
|
||||
go build
|
||||
```
|
||||
|
||||
### Docker
|
||||
|
||||
```
|
||||
docker run --rm gogost/gost -V
|
||||
```
|
||||
|
||||
## 工具
|
||||
|
||||
### GUI
|
||||
|
||||
[go-gost/gostctl](https://github.com/go-gost/gostctl)
|
||||
|
||||
### WebUI
|
||||
|
||||
[go-gost/gost-ui](https://github.com/go-gost/gost-ui)
|
||||
|
||||
### Shadowsocks Android插件
|
||||
|
||||
[xausky/ShadowsocksGostPlugin](https://github.com/xausky/ShadowsocksGostPlugin)
|
||||
|
||||
## 帮助与支持
|
||||
|
||||
Wiki站点:[https://gost.run](https://gost.run)
|
||||
|
||||
YouTube: [https://www.youtube.com/@gost-tunnel](https://www.youtube.com/@gost-tunnel)
|
||||
|
||||
Telegram:[https://t.me/gogost](https://t.me/gogost)
|
||||
|
||||
Google讨论组:[https://groups.google.com/d/forum/go-gost](https://groups.google.com/d/forum/go-gost)
|
||||
|
||||
旧版入口:[v2.gost.run](https://v2.gost.run)
|
||||
|
||||
+106
@@ -0,0 +1,106 @@
|
||||
# GO Simple Tunnel
|
||||
|
||||
### A simple security tunnel written in golang
|
||||
|
||||
[](README_en.md) [](README.md)
|
||||
|
||||
## Features
|
||||
|
||||
- [x] [Listening on multiple ports](https://gost.run/en/getting-started/quick-start/)
|
||||
- [x] [Multi-level forwarding chain](https://gost.run/en/concepts/chain/)
|
||||
- [x] Rich protocol
|
||||
- [x] [TCP/UDP port forwarding](https://gost.run/en/tutorials/port-forwarding/)
|
||||
- [x] [Reverse Proxy](https://gost.run/en/tutorials/reverse-proxy/) and [Tunnel](https://gost.run/en/tutorials/reverse-proxy-tunnel/)
|
||||
- [x] [TCP/UDP transparent proxy](https://gost.run/en/tutorials/redirect/)
|
||||
- [x] DNS [resolver](https://gost.run/en/concepts/resolver/) and [proxy](https://gost.run/en/tutorials/dns/)
|
||||
- [x] [TUN/TAP device](https://gost.run/en/tutorials/tuntap/)
|
||||
- [x] [Load balancing](https://gost.run/en/concepts/selector/)
|
||||
- [x] [Routing control](https://gost.run/en/concepts/bypass/)
|
||||
- [x] [Admission control](https://gost.run/en/concepts/limiter/)
|
||||
- [x] [Bandwidth/Rate Limiter](https://gost.run/en/concepts/limiter/)
|
||||
- [x] [Plugin System](https://gost.run/en/concepts/plugin/)
|
||||
- [x] [Prometheus metrics](https://gost.run/en/tutorials/metrics/)
|
||||
- [x] [Dynamic configuration](https://gost.run/en/tutorials/api/config/)
|
||||
- [x] [Web API](https://gost.run/en/tutorials/api/overview/)
|
||||
- [x] [GUI](https://github.com/go-gost/gostctl)/[WebUI](https://github.com/go-gost/gost-ui)
|
||||
|
||||
## Overview
|
||||
|
||||

|
||||
|
||||
There are three main ways to use GOST as a tunnel.
|
||||
|
||||
### Proxy
|
||||
|
||||
As a proxy service to access the network, multiple protocols can be used in combination to form a forwarding chain for traffic forwarding.
|
||||
|
||||

|
||||
|
||||
### Port Forwarding
|
||||
|
||||
Mapping the port of one service to the port of another service, you can also use a combination of multiple protocols to form a forwarding chain for traffic forwarding.
|
||||
|
||||

|
||||
|
||||
### Reverse Proxy
|
||||
|
||||
Use tunnel and intranet penetration to expose local services behind NAT or firewall to public network for access.
|
||||
|
||||

|
||||
|
||||
## Installation
|
||||
|
||||
### Binary files
|
||||
|
||||
[https://github.com/go-gost/gost/releases](https://github.com/go-gost/gost/releases)
|
||||
|
||||
### install script
|
||||
|
||||
```bash
|
||||
# install latest from [https://github.com/go-gost/gost/releases](https://github.com/go-gost/gost/releases)
|
||||
bash <(curl -fsSL https://github.com/go-gost/gost/raw/master/install.sh) --install
|
||||
```
|
||||
```bash
|
||||
# select version for install
|
||||
bash <(curl -fsSL https://github.com/go-gost/gost/raw/master/install.sh)
|
||||
```
|
||||
|
||||
### From source
|
||||
|
||||
```
|
||||
git clone https://github.com/go-gost/gost.git
|
||||
cd gost/cmd/gost
|
||||
go build
|
||||
```
|
||||
|
||||
### Docker
|
||||
|
||||
```
|
||||
docker run --rm gogost/gost -V
|
||||
```
|
||||
|
||||
## Tools
|
||||
|
||||
### GUI
|
||||
|
||||
[go-gost/gostctl](https://github.com/go-gost/gostctl)
|
||||
|
||||
### WebUI
|
||||
|
||||
[go-gost/gost-ui](https://github.com/go-gost/gost-ui)
|
||||
|
||||
### Shadowsocks Android
|
||||
|
||||
[xausky/ShadowsocksGostPlugin](https://github.com/xausky/ShadowsocksGostPlugin)
|
||||
|
||||
## Support
|
||||
|
||||
Wiki: [https://gost.run](https://gost.run/en/)
|
||||
|
||||
YouTube: [https://www.youtube.com/@gost-tunnel](https://www.youtube.com/@gost-tunnel)
|
||||
|
||||
Telegram: [https://t.me/gogost](https://t.me/gogost)
|
||||
|
||||
Google group: [https://groups.google.com/d/forum/go-gost](https://groups.google.com/d/forum/go-gost)
|
||||
|
||||
Legacy version: [v2.gost.run](https://v2.gost.run/en/)
|
||||
-522
@@ -1,522 +0,0 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"encoding/base64"
|
||||
"errors"
|
||||
"fmt"
|
||||
"net/url"
|
||||
"os"
|
||||
"strings"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
var (
|
||||
ErrInvalidCmd = errors.New("invalid cmd")
|
||||
ErrInvalidNode = errors.New("invalid node")
|
||||
)
|
||||
|
||||
type stringList []string
|
||||
|
||||
func (l *stringList) String() string {
|
||||
return fmt.Sprintf("%s", *l)
|
||||
}
|
||||
func (l *stringList) Set(value string) error {
|
||||
*l = append(*l, value)
|
||||
return nil
|
||||
}
|
||||
|
||||
func buildConfigFromCmd(services, nodes stringList) (*config.Config, error) {
|
||||
cfg := &config.Config{}
|
||||
|
||||
if v := os.Getenv("GOST_PROFILING"); v != "" {
|
||||
cfg.Profiling = &config.ProfilingConfig{
|
||||
Addr: v,
|
||||
Enable: true,
|
||||
}
|
||||
}
|
||||
if v := os.Getenv("GOST_METRICS"); v != "" {
|
||||
cfg.Metrics = &config.MetricsConfig{
|
||||
Addr: v,
|
||||
Path: "/metrics",
|
||||
Enable: true,
|
||||
}
|
||||
}
|
||||
|
||||
var chain *config.ChainConfig
|
||||
if len(nodes) > 0 {
|
||||
chain = &config.ChainConfig{
|
||||
Name: "chain-0",
|
||||
}
|
||||
cfg.Chains = append(cfg.Chains, chain)
|
||||
}
|
||||
|
||||
for i, node := range nodes {
|
||||
url, err := normCmd(node)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
nodeConfig, err := buildNodeConfig(url)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
nodeConfig.Name = "node-0"
|
||||
|
||||
var nodes []*config.NodeConfig
|
||||
for _, host := range strings.Split(nodeConfig.Addr, ",") {
|
||||
if host == "" {
|
||||
continue
|
||||
}
|
||||
nodeCfg := &config.NodeConfig{}
|
||||
*nodeCfg = *nodeConfig
|
||||
nodeCfg.Name = fmt.Sprintf("node-%d", len(nodes))
|
||||
nodeCfg.Addr = host
|
||||
nodes = append(nodes, nodeCfg)
|
||||
}
|
||||
|
||||
md := metadata.MapMetadata(nodeConfig.Connector.Metadata)
|
||||
|
||||
hopConfig := &config.HopConfig{
|
||||
Name: fmt.Sprintf("hop-%d", i),
|
||||
Selector: parseSelector(md),
|
||||
Nodes: nodes,
|
||||
}
|
||||
|
||||
if v := metadata.GetString(md, "bypass"); v != "" {
|
||||
bypassCfg := &config.BypassConfig{
|
||||
Name: fmt.Sprintf("bypass-%d", len(cfg.Bypasses)),
|
||||
}
|
||||
if v[0] == '~' {
|
||||
bypassCfg.Reverse = true
|
||||
v = v[1:]
|
||||
}
|
||||
for _, s := range strings.Split(v, ",") {
|
||||
if s == "" {
|
||||
continue
|
||||
}
|
||||
bypassCfg.Matchers = append(bypassCfg.Matchers, s)
|
||||
}
|
||||
hopConfig.Bypass = bypassCfg.Name
|
||||
cfg.Bypasses = append(cfg.Bypasses, bypassCfg)
|
||||
md.Del("bypass")
|
||||
}
|
||||
if v := metadata.GetString(md, "resolver"); v != "" {
|
||||
resolverCfg := &config.ResolverConfig{
|
||||
Name: fmt.Sprintf("resolver-%d", len(cfg.Resolvers)),
|
||||
}
|
||||
for _, rs := range strings.Split(v, ",") {
|
||||
if rs == "" {
|
||||
continue
|
||||
}
|
||||
resolverCfg.Nameservers = append(
|
||||
resolverCfg.Nameservers,
|
||||
&config.NameserverConfig{
|
||||
Addr: rs,
|
||||
},
|
||||
)
|
||||
}
|
||||
hopConfig.Resolver = resolverCfg.Name
|
||||
cfg.Resolvers = append(cfg.Resolvers, resolverCfg)
|
||||
md.Del("resolver")
|
||||
}
|
||||
if v := metadata.GetString(md, "hosts"); v != "" {
|
||||
hostsCfg := &config.HostsConfig{
|
||||
Name: fmt.Sprintf("hosts-%d", len(cfg.Hosts)),
|
||||
}
|
||||
for _, s := range strings.Split(v, ",") {
|
||||
ss := strings.SplitN(s, ":", 2)
|
||||
if len(ss) != 2 {
|
||||
continue
|
||||
}
|
||||
hostsCfg.Mappings = append(
|
||||
hostsCfg.Mappings,
|
||||
&config.HostMappingConfig{
|
||||
Hostname: ss[0],
|
||||
IP: ss[1],
|
||||
},
|
||||
)
|
||||
}
|
||||
hopConfig.Hosts = hostsCfg.Name
|
||||
cfg.Hosts = append(cfg.Hosts, hostsCfg)
|
||||
md.Del("hosts")
|
||||
}
|
||||
|
||||
chain.Hops = append(chain.Hops, hopConfig)
|
||||
}
|
||||
|
||||
for i, svc := range services {
|
||||
url, err := normCmd(svc)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
service, err := buildServiceConfig(url)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
service.Name = fmt.Sprintf("service-%d", i)
|
||||
if chain != nil {
|
||||
if service.Listener.Type == "rtcp" || service.Listener.Type == "rudp" {
|
||||
service.Listener.Chain = chain.Name
|
||||
} else {
|
||||
service.Handler.Chain = chain.Name
|
||||
}
|
||||
}
|
||||
cfg.Services = append(cfg.Services, service)
|
||||
|
||||
md := metadata.MapMetadata(service.Handler.Metadata)
|
||||
if v := metadata.GetInt(md, "retries"); v > 0 {
|
||||
service.Handler.Retries = v
|
||||
md.Del("retries")
|
||||
}
|
||||
if v := metadata.GetString(md, "admission"); v != "" {
|
||||
admCfg := &config.AdmissionConfig{
|
||||
Name: fmt.Sprintf("admission-%d", len(cfg.Admissions)),
|
||||
}
|
||||
if v[0] == '~' {
|
||||
admCfg.Reverse = true
|
||||
v = v[1:]
|
||||
}
|
||||
for _, s := range strings.Split(v, ",") {
|
||||
if s == "" {
|
||||
continue
|
||||
}
|
||||
admCfg.Matchers = append(admCfg.Matchers, s)
|
||||
}
|
||||
service.Admission = admCfg.Name
|
||||
cfg.Admissions = append(cfg.Admissions, admCfg)
|
||||
md.Del("admission")
|
||||
}
|
||||
if v := metadata.GetString(md, "bypass"); v != "" {
|
||||
bypassCfg := &config.BypassConfig{
|
||||
Name: fmt.Sprintf("bypass-%d", len(cfg.Bypasses)),
|
||||
}
|
||||
if v[0] == '~' {
|
||||
bypassCfg.Reverse = true
|
||||
v = v[1:]
|
||||
}
|
||||
for _, s := range strings.Split(v, ",") {
|
||||
if s == "" {
|
||||
continue
|
||||
}
|
||||
bypassCfg.Matchers = append(bypassCfg.Matchers, s)
|
||||
}
|
||||
service.Bypass = bypassCfg.Name
|
||||
cfg.Bypasses = append(cfg.Bypasses, bypassCfg)
|
||||
md.Del("bypass")
|
||||
}
|
||||
if v := metadata.GetString(md, "resolver"); v != "" {
|
||||
resolverCfg := &config.ResolverConfig{
|
||||
Name: fmt.Sprintf("resolver-%d", len(cfg.Resolvers)),
|
||||
}
|
||||
for _, rs := range strings.Split(v, ",") {
|
||||
if rs == "" {
|
||||
continue
|
||||
}
|
||||
resolverCfg.Nameservers = append(
|
||||
resolverCfg.Nameservers,
|
||||
&config.NameserverConfig{
|
||||
Addr: rs,
|
||||
},
|
||||
)
|
||||
}
|
||||
service.Resolver = resolverCfg.Name
|
||||
cfg.Resolvers = append(cfg.Resolvers, resolverCfg)
|
||||
md.Del("resolver")
|
||||
}
|
||||
if v := metadata.GetString(md, "hosts"); v != "" {
|
||||
hostsCfg := &config.HostsConfig{
|
||||
Name: fmt.Sprintf("hosts-%d", len(cfg.Hosts)),
|
||||
}
|
||||
for _, s := range strings.Split(v, ",") {
|
||||
ss := strings.SplitN(s, ":", 2)
|
||||
if len(ss) != 2 {
|
||||
continue
|
||||
}
|
||||
hostsCfg.Mappings = append(
|
||||
hostsCfg.Mappings,
|
||||
&config.HostMappingConfig{
|
||||
Hostname: ss[0],
|
||||
IP: ss[1],
|
||||
},
|
||||
)
|
||||
}
|
||||
service.Hosts = hostsCfg.Name
|
||||
cfg.Hosts = append(cfg.Hosts, hostsCfg)
|
||||
md.Del("hosts")
|
||||
}
|
||||
}
|
||||
|
||||
return cfg, nil
|
||||
}
|
||||
|
||||
func buildServiceConfig(url *url.URL) (*config.ServiceConfig, error) {
|
||||
var handler, listener string
|
||||
schemes := strings.Split(url.Scheme, "+")
|
||||
if len(schemes) == 1 {
|
||||
handler = schemes[0]
|
||||
listener = schemes[0]
|
||||
}
|
||||
if len(schemes) == 2 {
|
||||
handler = schemes[0]
|
||||
listener = schemes[1]
|
||||
}
|
||||
|
||||
svc := &config.ServiceConfig{
|
||||
Addr: url.Host,
|
||||
}
|
||||
|
||||
if h := registry.GetHandler(handler); h == nil {
|
||||
handler = "auto"
|
||||
}
|
||||
if ln := registry.GetListener(listener); ln == nil {
|
||||
listener = "tcp"
|
||||
if handler == "ssu" {
|
||||
listener = "udp"
|
||||
}
|
||||
}
|
||||
|
||||
// forward mode
|
||||
if remotes := strings.Trim(url.EscapedPath(), "/"); remotes != "" {
|
||||
svc.Forwarder = &config.ForwarderConfig{
|
||||
Targets: strings.Split(remotes, ","),
|
||||
}
|
||||
if handler != "relay" {
|
||||
if listener == "tcp" || listener == "udp" ||
|
||||
listener == "rtcp" || listener == "rudp" ||
|
||||
listener == "tun" || listener == "tap" {
|
||||
handler = listener
|
||||
} else {
|
||||
handler = "forward"
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
var auth *config.AuthConfig
|
||||
if url.User != nil {
|
||||
auth = &config.AuthConfig{
|
||||
Username: url.User.Username(),
|
||||
}
|
||||
auth.Password, _ = url.User.Password()
|
||||
}
|
||||
|
||||
md := metadata.MapMetadata{}
|
||||
for k, v := range url.Query() {
|
||||
if len(v) > 0 {
|
||||
md[k] = v[0]
|
||||
}
|
||||
}
|
||||
|
||||
if sa := metadata.GetString(md, "auth"); sa != "" {
|
||||
au, err := parseAuthFromCmd(sa)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
auth = au
|
||||
}
|
||||
md.Del("auth")
|
||||
|
||||
tlsConfig := &config.TLSConfig{
|
||||
CertFile: metadata.GetString(md, "certFile"),
|
||||
KeyFile: metadata.GetString(md, "keyFile"),
|
||||
CAFile: metadata.GetString(md, "caFile"),
|
||||
}
|
||||
md.Del("certFile")
|
||||
md.Del("keyFile")
|
||||
md.Del("caFile")
|
||||
|
||||
if tlsConfig.CertFile == "" {
|
||||
tlsConfig = nil
|
||||
}
|
||||
|
||||
if v := metadata.GetString(md, "dns"); v != "" {
|
||||
md.Set("dns", strings.Split(v, ","))
|
||||
}
|
||||
|
||||
if svc.Forwarder != nil {
|
||||
svc.Forwarder.Selector = parseSelector(md)
|
||||
}
|
||||
|
||||
svc.Handler = &config.HandlerConfig{
|
||||
Type: handler,
|
||||
Auth: auth,
|
||||
Metadata: md,
|
||||
}
|
||||
svc.Listener = &config.ListenerConfig{
|
||||
Type: listener,
|
||||
TLS: tlsConfig,
|
||||
Metadata: md,
|
||||
}
|
||||
|
||||
if svc.Handler.Type == "sshd" {
|
||||
svc.Handler.Auth = nil
|
||||
}
|
||||
if svc.Listener.Type == "sshd" {
|
||||
svc.Listener.Auth = auth
|
||||
}
|
||||
|
||||
return svc, nil
|
||||
}
|
||||
|
||||
func buildNodeConfig(url *url.URL) (*config.NodeConfig, error) {
|
||||
var connector, dialer string
|
||||
schemes := strings.Split(url.Scheme, "+")
|
||||
if len(schemes) == 1 {
|
||||
connector = schemes[0]
|
||||
dialer = schemes[0]
|
||||
}
|
||||
if len(schemes) == 2 {
|
||||
connector = schemes[0]
|
||||
dialer = schemes[1]
|
||||
}
|
||||
|
||||
node := &config.NodeConfig{
|
||||
Addr: url.Host,
|
||||
}
|
||||
|
||||
if c := registry.GetConnector(connector); c == nil {
|
||||
connector = "http"
|
||||
}
|
||||
if d := registry.GetDialer(dialer); d == nil {
|
||||
dialer = "tcp"
|
||||
if connector == "ssu" {
|
||||
dialer = "udp"
|
||||
}
|
||||
}
|
||||
|
||||
var auth *config.AuthConfig
|
||||
if url.User != nil {
|
||||
auth = &config.AuthConfig{
|
||||
Username: url.User.Username(),
|
||||
}
|
||||
auth.Password, _ = url.User.Password()
|
||||
}
|
||||
|
||||
md := metadata.MapMetadata{}
|
||||
for k, v := range url.Query() {
|
||||
if len(v) > 0 {
|
||||
md[k] = v[0]
|
||||
}
|
||||
}
|
||||
|
||||
if sauth := metadata.GetString(md, "auth"); sauth != "" && auth == nil {
|
||||
au, err := parseAuthFromCmd(sauth)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
auth = au
|
||||
}
|
||||
md.Del("auth")
|
||||
|
||||
tlsConfig := &config.TLSConfig{
|
||||
CertFile: metadata.GetString(md, "certFile"),
|
||||
KeyFile: metadata.GetString(md, "keyFile"),
|
||||
CAFile: metadata.GetString(md, "caFile"),
|
||||
Secure: metadata.GetBool(md, "secure"),
|
||||
ServerName: metadata.GetString(md, "serverName"),
|
||||
}
|
||||
if tlsConfig.ServerName == "" {
|
||||
tlsConfig.ServerName = url.Hostname()
|
||||
}
|
||||
md.Del("certFile")
|
||||
md.Del("keyFile")
|
||||
md.Del("caFile")
|
||||
md.Del("secure")
|
||||
md.Del("serverName")
|
||||
|
||||
if !tlsConfig.Secure && tlsConfig.CertFile == "" && tlsConfig.CAFile == "" {
|
||||
tlsConfig = nil
|
||||
}
|
||||
|
||||
node.Connector = &config.ConnectorConfig{
|
||||
Type: connector,
|
||||
Auth: auth,
|
||||
Metadata: md,
|
||||
}
|
||||
node.Dialer = &config.DialerConfig{
|
||||
Type: dialer,
|
||||
TLS: tlsConfig,
|
||||
Metadata: md,
|
||||
}
|
||||
|
||||
if node.Connector.Type == "sshd" {
|
||||
node.Connector.Auth = nil
|
||||
}
|
||||
if node.Dialer.Type == "sshd" {
|
||||
node.Dialer.Auth = auth
|
||||
}
|
||||
|
||||
return node, nil
|
||||
}
|
||||
|
||||
func normCmd(s string) (*url.URL, error) {
|
||||
s = strings.TrimSpace(s)
|
||||
if s == "" {
|
||||
return nil, ErrInvalidCmd
|
||||
}
|
||||
|
||||
if s[0] == ':' || !strings.Contains(s, "://") {
|
||||
s = "auto://" + s
|
||||
}
|
||||
|
||||
url, err := url.Parse(s)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
if url.Scheme == "https" {
|
||||
url.Scheme = "http+tls"
|
||||
}
|
||||
|
||||
return url, nil
|
||||
}
|
||||
|
||||
func parseAuthFromCmd(sa string) (*config.AuthConfig, error) {
|
||||
v, err := base64.StdEncoding.DecodeString(sa)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
cs := string(v)
|
||||
n := strings.IndexByte(cs, ':')
|
||||
if n < 0 {
|
||||
return &config.AuthConfig{
|
||||
Username: cs,
|
||||
}, nil
|
||||
}
|
||||
|
||||
return &config.AuthConfig{
|
||||
Username: cs[:n],
|
||||
Password: cs[n+1:],
|
||||
}, nil
|
||||
}
|
||||
|
||||
func parseSelector(md metadata.MapMetadata) *config.SelectorConfig {
|
||||
strategy := metadata.GetString(md, "strategy")
|
||||
maxFails := metadata.GetInt(md, "maxFails")
|
||||
failTimeout := metadata.GetDuration(md, "failTimeout")
|
||||
if strategy == "" && maxFails <= 0 && failTimeout <= 0 {
|
||||
return nil
|
||||
}
|
||||
if strategy == "" {
|
||||
strategy = "round"
|
||||
}
|
||||
if maxFails <= 0 {
|
||||
maxFails = 1
|
||||
}
|
||||
if failTimeout <= 0 {
|
||||
failTimeout = time.Second
|
||||
}
|
||||
|
||||
md.Del("strategy")
|
||||
md.Del("maxFails")
|
||||
md.Del("failTimeout")
|
||||
|
||||
return &config.SelectorConfig{
|
||||
Strategy: strategy,
|
||||
MaxFails: maxFails,
|
||||
FailTimeout: failTimeout,
|
||||
}
|
||||
}
|
||||
@@ -1,133 +0,0 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"io"
|
||||
"os"
|
||||
|
||||
"github.com/go-gost/gost/pkg/api"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/go-gost/gost/pkg/service"
|
||||
)
|
||||
|
||||
func buildService(cfg *config.Config) (services []service.Service) {
|
||||
if cfg == nil {
|
||||
return
|
||||
}
|
||||
|
||||
for _, autherCfg := range cfg.Authers {
|
||||
if auther := parsing.ParseAuther(autherCfg); auther != nil {
|
||||
if err := registry.Auther().Register(autherCfg.Name, auther); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, admissionCfg := range cfg.Admissions {
|
||||
if adm := parsing.ParseAdmission(admissionCfg); adm != nil {
|
||||
if err := registry.Admission().Register(admissionCfg.Name, adm); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, bypassCfg := range cfg.Bypasses {
|
||||
if bp := parsing.ParseBypass(bypassCfg); bp != nil {
|
||||
if err := registry.Bypass().Register(bypassCfg.Name, bp); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, resolverCfg := range cfg.Resolvers {
|
||||
r, err := parsing.ParseResolver(resolverCfg)
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
if r != nil {
|
||||
if err := registry.Resolver().Register(resolverCfg.Name, r); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, hostsCfg := range cfg.Hosts {
|
||||
if h := parsing.ParseHosts(hostsCfg); h != nil {
|
||||
if err := registry.Hosts().Register(hostsCfg.Name, h); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, chainCfg := range cfg.Chains {
|
||||
c, err := parsing.ParseChain(chainCfg)
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
if c != nil {
|
||||
if err := registry.Chain().Register(chainCfg.Name, c); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
for _, svcCfg := range cfg.Services {
|
||||
svc, err := parsing.ParseService(svcCfg)
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
if svc != nil {
|
||||
if err := registry.Service().Register(svcCfg.Name, svc); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
}
|
||||
services = append(services, svc)
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func logFromConfig(cfg *config.LogConfig) logger.Logger {
|
||||
if cfg == nil {
|
||||
cfg = &config.LogConfig{}
|
||||
}
|
||||
opts := []logger.LoggerOption{
|
||||
logger.FormatLoggerOption(logger.LogFormat(cfg.Format)),
|
||||
logger.LevelLoggerOption(logger.LogLevel(cfg.Level)),
|
||||
}
|
||||
|
||||
var out io.Writer = os.Stderr
|
||||
switch cfg.Output {
|
||||
case "none", "null":
|
||||
return logger.Nop()
|
||||
case "stdout":
|
||||
out = os.Stdout
|
||||
case "stderr", "":
|
||||
out = os.Stderr
|
||||
default:
|
||||
f, err := os.OpenFile(cfg.Output, os.O_CREATE|os.O_WRONLY|os.O_APPEND, 0666)
|
||||
if err != nil {
|
||||
log.Warnf("log", err)
|
||||
} else {
|
||||
out = f
|
||||
}
|
||||
}
|
||||
opts = append(opts, logger.OutputLoggerOption(out))
|
||||
|
||||
return logger.NewLogger(opts...)
|
||||
}
|
||||
|
||||
func buildAPIServer(cfg *config.APIConfig) (*api.Server, error) {
|
||||
auther := parsing.ParseAutherFromAuth(cfg.Auth)
|
||||
if cfg.Auther != "" {
|
||||
auther = registry.Auther().Get(cfg.Auther)
|
||||
}
|
||||
return api.NewServer(
|
||||
cfg.Addr,
|
||||
api.PathPrefixOption(cfg.PathPrefix),
|
||||
api.AccessLogOption(cfg.AccessLog),
|
||||
api.AutherOption(auther),
|
||||
)
|
||||
}
|
||||
+73
-75
@@ -1,38 +1,99 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"context"
|
||||
"flag"
|
||||
"fmt"
|
||||
"net/http"
|
||||
"log"
|
||||
_ "net/http/pprof"
|
||||
"os"
|
||||
"os/exec"
|
||||
"runtime"
|
||||
"strings"
|
||||
"sync"
|
||||
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/core/logger"
|
||||
xlogger "github.com/go-gost/x/logger"
|
||||
"github.com/judwhite/go-svc"
|
||||
)
|
||||
|
||||
var (
|
||||
log = logger.Default()
|
||||
type stringList []string
|
||||
|
||||
func (l *stringList) String() string {
|
||||
return fmt.Sprintf("%s", *l)
|
||||
}
|
||||
func (l *stringList) Set(value string) error {
|
||||
*l = append(*l, value)
|
||||
return nil
|
||||
}
|
||||
|
||||
var (
|
||||
cfgFile string
|
||||
outputFormat string
|
||||
services stringList
|
||||
nodes stringList
|
||||
debug bool
|
||||
trace bool
|
||||
apiAddr string
|
||||
metricsAddr string
|
||||
)
|
||||
|
||||
func init() {
|
||||
log.SetFlags(log.LstdFlags | log.Lshortfile | log.Lmicroseconds)
|
||||
|
||||
args := strings.Join(os.Args[1:], " ")
|
||||
|
||||
if strings.Contains(args, " -- ") {
|
||||
var (
|
||||
wg sync.WaitGroup
|
||||
ret int
|
||||
)
|
||||
|
||||
ctx, cancel := context.WithCancel(context.Background())
|
||||
defer cancel()
|
||||
|
||||
for wid, wargs := range strings.Split(" "+args+" ", " -- ") {
|
||||
wg.Add(1)
|
||||
go func(wid int, wargs string) {
|
||||
defer wg.Done()
|
||||
defer cancel()
|
||||
worker(wid, strings.Split(wargs, " "), &ctx, &ret)
|
||||
}(wid, strings.TrimSpace(wargs))
|
||||
}
|
||||
|
||||
wg.Wait()
|
||||
|
||||
os.Exit(ret)
|
||||
}
|
||||
}
|
||||
|
||||
func worker(id int, args []string, ctx *context.Context, ret *int) {
|
||||
cmd := exec.CommandContext(*ctx, os.Args[0], args...)
|
||||
|
||||
cmd.Stdout = os.Stdout
|
||||
cmd.Stderr = os.Stderr
|
||||
cmd.Env = append(os.Environ(), fmt.Sprintf("_GOST_ID=%d", id))
|
||||
|
||||
if err := cmd.Run(); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
if cmd.ProcessState.Exited() {
|
||||
*ret = cmd.ProcessState.ExitCode()
|
||||
}
|
||||
}
|
||||
|
||||
func init() {
|
||||
var printVersion bool
|
||||
|
||||
flag.Var(&services, "L", "service list")
|
||||
flag.Var(&nodes, "F", "chain node list")
|
||||
flag.StringVar(&cfgFile, "C", "", "configure file")
|
||||
flag.StringVar(&cfgFile, "C", "", "configuration file")
|
||||
flag.BoolVar(&printVersion, "V", false, "print version")
|
||||
flag.StringVar(&outputFormat, "O", "", "output format, one of yaml|json format")
|
||||
flag.BoolVar(&debug, "D", false, "debug mode")
|
||||
flag.StringVar(&apiAddr, "api", "", "api server addr")
|
||||
flag.BoolVar(&trace, "DD", false, "trace mode")
|
||||
flag.StringVar(&apiAddr, "api", "", "api service address")
|
||||
flag.StringVar(&metricsAddr, "metrics", "", "metrics service address")
|
||||
flag.Parse()
|
||||
|
||||
if printVersion {
|
||||
@@ -43,75 +104,12 @@ func init() {
|
||||
}
|
||||
|
||||
func main() {
|
||||
cfg := &config.Config{}
|
||||
var err error
|
||||
if len(services) > 0 || apiAddr != "" {
|
||||
cfg, err = buildConfigFromCmd(services, nodes)
|
||||
if debug && cfg != nil {
|
||||
if cfg.Log == nil {
|
||||
cfg.Log = &config.LogConfig{}
|
||||
}
|
||||
cfg.Log.Level = string(logger.DebugLevel)
|
||||
}
|
||||
if apiAddr != "" {
|
||||
cfg.API = &config.APIConfig{
|
||||
Addr: apiAddr,
|
||||
}
|
||||
}
|
||||
} else {
|
||||
if cfgFile != "" {
|
||||
err = cfg.ReadFile(cfgFile)
|
||||
} else {
|
||||
err = cfg.Load()
|
||||
}
|
||||
}
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
|
||||
log = logFromConfig(cfg.Log)
|
||||
|
||||
log := xlogger.NewLogger()
|
||||
logger.SetDefault(log)
|
||||
|
||||
if outputFormat != "" {
|
||||
if err := cfg.Write(os.Stdout, outputFormat); err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
os.Exit(0)
|
||||
p := &program{}
|
||||
|
||||
if err := svc.Run(p); err != nil {
|
||||
logger.Default().Fatal(err)
|
||||
}
|
||||
|
||||
if cfg.Profiling != nil && cfg.Profiling.Enable {
|
||||
go func() {
|
||||
addr := cfg.Profiling.Addr
|
||||
if addr == "" {
|
||||
addr = ":6060"
|
||||
}
|
||||
log.Info("profiling server on ", addr)
|
||||
log.Fatal(http.ListenAndServe(addr, nil))
|
||||
}()
|
||||
}
|
||||
|
||||
if cfg.API != nil {
|
||||
s, err := buildAPIServer(cfg.API)
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
defer s.Close()
|
||||
|
||||
go func() {
|
||||
log.Info("api server on ", s.Addr())
|
||||
log.Fatal(s.Serve())
|
||||
}()
|
||||
}
|
||||
|
||||
buildDefaultTLSConfig(cfg.TLS)
|
||||
|
||||
services := buildService(cfg)
|
||||
for _, svc := range services {
|
||||
go svc.Serve()
|
||||
}
|
||||
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
select {}
|
||||
}
|
||||
|
||||
@@ -0,0 +1,274 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"context"
|
||||
"errors"
|
||||
"net/http"
|
||||
"os"
|
||||
"os/signal"
|
||||
"strings"
|
||||
"syscall"
|
||||
|
||||
"github.com/go-gost/core/auth"
|
||||
"github.com/go-gost/core/logger"
|
||||
"github.com/go-gost/core/service"
|
||||
api_service "github.com/go-gost/x/api/service"
|
||||
xauth "github.com/go-gost/x/auth"
|
||||
"github.com/go-gost/x/config"
|
||||
"github.com/go-gost/x/config/loader"
|
||||
auth_parser "github.com/go-gost/x/config/parsing/auth"
|
||||
"github.com/go-gost/x/config/parsing/parser"
|
||||
xmetrics "github.com/go-gost/x/metrics"
|
||||
metrics "github.com/go-gost/x/metrics/service"
|
||||
"github.com/go-gost/x/registry"
|
||||
"github.com/judwhite/go-svc"
|
||||
)
|
||||
|
||||
type program struct {
|
||||
srvApi service.Service
|
||||
srvMetrics service.Service
|
||||
srvProfiling *http.Server
|
||||
|
||||
cancel context.CancelFunc
|
||||
}
|
||||
|
||||
func (p *program) Init(env svc.Environment) error {
|
||||
parser.Init(parser.Args{
|
||||
CfgFile: cfgFile,
|
||||
Services: services,
|
||||
Nodes: nodes,
|
||||
Debug: debug,
|
||||
Trace: trace,
|
||||
ApiAddr: apiAddr,
|
||||
MetricsAddr: metricsAddr,
|
||||
})
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func (p *program) Start() error {
|
||||
cfg, err := parser.Parse()
|
||||
if err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
if outputFormat != "" {
|
||||
if err := cfg.Write(os.Stdout, outputFormat); err != nil {
|
||||
return err
|
||||
}
|
||||
os.Exit(0)
|
||||
}
|
||||
|
||||
config.Set(cfg)
|
||||
|
||||
if err := loader.Load(cfg); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
if err := p.run(cfg); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
ctx, cancel := context.WithCancel(context.Background())
|
||||
p.cancel = cancel
|
||||
go p.reload(ctx)
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func (p *program) run(cfg *config.Config) error {
|
||||
for _, svc := range registry.ServiceRegistry().GetAll() {
|
||||
svc := svc
|
||||
go func() {
|
||||
svc.Serve()
|
||||
}()
|
||||
}
|
||||
|
||||
if p.srvApi != nil {
|
||||
p.srvApi.Close()
|
||||
p.srvApi = nil
|
||||
}
|
||||
if cfg.API != nil {
|
||||
s, err := buildApiService(cfg.API)
|
||||
if err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
p.srvApi = s
|
||||
|
||||
go func() {
|
||||
defer s.Close()
|
||||
|
||||
log := logger.Default().WithFields(map[string]any{"kind": "service", "service": "@api"})
|
||||
|
||||
log.Info("listening on ", s.Addr())
|
||||
if err := s.Serve(); !errors.Is(err, http.ErrServerClosed) {
|
||||
log.Error(err)
|
||||
}
|
||||
}()
|
||||
}
|
||||
|
||||
if p.srvMetrics != nil {
|
||||
p.srvMetrics.Close()
|
||||
p.srvMetrics = nil
|
||||
}
|
||||
if cfg.Metrics != nil && cfg.Metrics.Addr != "" {
|
||||
s, err := buildMetricsService(cfg.Metrics)
|
||||
if err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
p.srvMetrics = s
|
||||
|
||||
xmetrics.Enable(true)
|
||||
|
||||
go func() {
|
||||
defer s.Close()
|
||||
|
||||
log := logger.Default().WithFields(map[string]any{"kind": "service", "service": "@metrics"})
|
||||
|
||||
log.Info("listening on ", s.Addr())
|
||||
if err := s.Serve(); !errors.Is(err, http.ErrServerClosed) {
|
||||
log.Error(err)
|
||||
}
|
||||
}()
|
||||
}
|
||||
|
||||
if p.srvProfiling != nil {
|
||||
p.srvProfiling.Close()
|
||||
p.srvProfiling = nil
|
||||
}
|
||||
if cfg.Profiling != nil {
|
||||
addr := cfg.Profiling.Addr
|
||||
if addr == "" {
|
||||
addr = ":6060"
|
||||
}
|
||||
s := &http.Server{
|
||||
Addr: addr,
|
||||
}
|
||||
p.srvProfiling = s
|
||||
|
||||
go func() {
|
||||
defer s.Close()
|
||||
|
||||
log := logger.Default().WithFields(map[string]any{"kind": "service", "service": "@profiling"})
|
||||
|
||||
log.Info("listening on ", addr)
|
||||
if err := s.ListenAndServe(); !errors.Is(err, http.ErrServerClosed) {
|
||||
log.Error(err)
|
||||
}
|
||||
}()
|
||||
}
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func (p *program) Stop() error {
|
||||
if p.cancel != nil {
|
||||
p.cancel()
|
||||
}
|
||||
|
||||
for name, srv := range registry.ServiceRegistry().GetAll() {
|
||||
srv.Close()
|
||||
logger.Default().Debugf("service %s shutdown", name)
|
||||
}
|
||||
|
||||
if p.srvApi != nil {
|
||||
p.srvApi.Close()
|
||||
logger.Default().Debug("service @api shutdown")
|
||||
}
|
||||
if p.srvMetrics != nil {
|
||||
p.srvMetrics.Close()
|
||||
logger.Default().Debug("service @metrics shutdown")
|
||||
}
|
||||
if p.srvProfiling != nil {
|
||||
p.srvProfiling.Close()
|
||||
logger.Default().Debug("service @profiling shutdown")
|
||||
}
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func (p *program) reload(ctx context.Context) {
|
||||
c := make(chan os.Signal, 1)
|
||||
signal.Notify(c, syscall.SIGHUP)
|
||||
|
||||
for {
|
||||
select {
|
||||
case <-c:
|
||||
if err := p.reloadConfig(); err != nil {
|
||||
logger.Default().Error(err)
|
||||
} else {
|
||||
logger.Default().Info("config reloaded")
|
||||
}
|
||||
|
||||
case <-ctx.Done():
|
||||
return
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
func (p *program) reloadConfig() error {
|
||||
cfg, err := parser.Parse()
|
||||
if err != nil {
|
||||
return err
|
||||
}
|
||||
config.Set(cfg)
|
||||
|
||||
if err := loader.Load(cfg); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
if err := p.run(cfg); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func buildApiService(cfg *config.APIConfig) (service.Service, error) {
|
||||
var authers []auth.Authenticator
|
||||
if auther := auth_parser.ParseAutherFromAuth(cfg.Auth); auther != nil {
|
||||
authers = append(authers, auther)
|
||||
}
|
||||
if cfg.Auther != "" {
|
||||
authers = append(authers, registry.AutherRegistry().Get(cfg.Auther))
|
||||
}
|
||||
|
||||
var auther auth.Authenticator
|
||||
if len(authers) > 0 {
|
||||
auther = xauth.AuthenticatorGroup(authers...)
|
||||
}
|
||||
|
||||
network := "tcp"
|
||||
addr := cfg.Addr
|
||||
if strings.HasPrefix(addr, "unix://") {
|
||||
network = "unix"
|
||||
addr = strings.TrimPrefix(addr, "unix://")
|
||||
}
|
||||
return api_service.NewService(
|
||||
network, addr,
|
||||
api_service.PathPrefixOption(cfg.PathPrefix),
|
||||
api_service.AccessLogOption(cfg.AccessLog),
|
||||
api_service.AutherOption(auther),
|
||||
)
|
||||
}
|
||||
|
||||
func buildMetricsService(cfg *config.MetricsConfig) (service.Service, error) {
|
||||
auther := auth_parser.ParseAutherFromAuth(cfg.Auth)
|
||||
if cfg.Auther != "" {
|
||||
auther = registry.AutherRegistry().Get(cfg.Auther)
|
||||
}
|
||||
|
||||
network := "tcp"
|
||||
addr := cfg.Addr
|
||||
if strings.HasPrefix(addr, "unix://") {
|
||||
network = "unix"
|
||||
addr = strings.TrimPrefix(addr, "unix://")
|
||||
}
|
||||
return metrics.NewService(
|
||||
network, addr,
|
||||
metrics.PathOption(cfg.Path),
|
||||
metrics.AutherOption(auther),
|
||||
)
|
||||
}
|
||||
+98
-68
@@ -2,78 +2,108 @@ package main
|
||||
|
||||
import (
|
||||
// Register connectors
|
||||
_ "github.com/go-gost/gost/pkg/connector/forward"
|
||||
_ "github.com/go-gost/gost/pkg/connector/http"
|
||||
_ "github.com/go-gost/gost/pkg/connector/http2"
|
||||
_ "github.com/go-gost/gost/pkg/connector/relay"
|
||||
_ "github.com/go-gost/gost/pkg/connector/sni"
|
||||
_ "github.com/go-gost/gost/pkg/connector/socks/v4"
|
||||
_ "github.com/go-gost/gost/pkg/connector/socks/v5"
|
||||
_ "github.com/go-gost/gost/pkg/connector/ss"
|
||||
_ "github.com/go-gost/gost/pkg/connector/ss/udp"
|
||||
_ "github.com/go-gost/gost/pkg/connector/sshd"
|
||||
_ "github.com/go-gost/x/connector/direct"
|
||||
_ "github.com/go-gost/x/connector/forward"
|
||||
_ "github.com/go-gost/x/connector/http"
|
||||
_ "github.com/go-gost/x/connector/http2"
|
||||
_ "github.com/go-gost/x/connector/relay"
|
||||
_ "github.com/go-gost/x/connector/router"
|
||||
_ "github.com/go-gost/x/connector/serial"
|
||||
_ "github.com/go-gost/x/connector/sni"
|
||||
_ "github.com/go-gost/x/connector/socks/v4"
|
||||
_ "github.com/go-gost/x/connector/socks/v5"
|
||||
_ "github.com/go-gost/x/connector/ss"
|
||||
_ "github.com/go-gost/x/connector/ss/udp"
|
||||
_ "github.com/go-gost/x/connector/sshd"
|
||||
_ "github.com/go-gost/x/connector/tcp"
|
||||
_ "github.com/go-gost/x/connector/tunnel"
|
||||
_ "github.com/go-gost/x/connector/unix"
|
||||
|
||||
// Register dialers
|
||||
_ "github.com/go-gost/gost/pkg/dialer/ftcp"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/grpc"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/http2"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/http2/h2"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/http3"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/kcp"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/obfs/http"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/obfs/tls"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/pht"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/quic"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/ssh"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/sshd"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/tcp"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/tls"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/tls/mux"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/udp"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/ws"
|
||||
_ "github.com/go-gost/gost/pkg/dialer/ws/mux"
|
||||
_ "github.com/go-gost/x/dialer/direct"
|
||||
_ "github.com/go-gost/x/dialer/dtls"
|
||||
_ "github.com/go-gost/x/dialer/ftcp"
|
||||
_ "github.com/go-gost/x/dialer/grpc"
|
||||
_ "github.com/go-gost/x/dialer/http2"
|
||||
_ "github.com/go-gost/x/dialer/http2/h2"
|
||||
_ "github.com/go-gost/x/dialer/http3"
|
||||
_ "github.com/go-gost/x/dialer/http3/wt"
|
||||
_ "github.com/go-gost/x/dialer/icmp"
|
||||
_ "github.com/go-gost/x/dialer/kcp"
|
||||
_ "github.com/go-gost/x/dialer/mtcp"
|
||||
_ "github.com/go-gost/x/dialer/mtls"
|
||||
_ "github.com/go-gost/x/dialer/mws"
|
||||
_ "github.com/go-gost/x/dialer/obfs/http"
|
||||
_ "github.com/go-gost/x/dialer/obfs/tls"
|
||||
_ "github.com/go-gost/x/dialer/pht"
|
||||
_ "github.com/go-gost/x/dialer/quic"
|
||||
_ "github.com/go-gost/x/dialer/serial"
|
||||
_ "github.com/go-gost/x/dialer/ssh"
|
||||
_ "github.com/go-gost/x/dialer/sshd"
|
||||
_ "github.com/go-gost/x/dialer/tcp"
|
||||
_ "github.com/go-gost/x/dialer/tls"
|
||||
_ "github.com/go-gost/x/dialer/udp"
|
||||
_ "github.com/go-gost/x/dialer/unix"
|
||||
_ "github.com/go-gost/x/dialer/ws"
|
||||
|
||||
// Register handlers
|
||||
_ "github.com/go-gost/gost/pkg/handler/auto"
|
||||
_ "github.com/go-gost/gost/pkg/handler/dns"
|
||||
_ "github.com/go-gost/gost/pkg/handler/forward/local"
|
||||
_ "github.com/go-gost/gost/pkg/handler/forward/remote"
|
||||
_ "github.com/go-gost/gost/pkg/handler/http"
|
||||
_ "github.com/go-gost/gost/pkg/handler/http2"
|
||||
_ "github.com/go-gost/gost/pkg/handler/redirect"
|
||||
_ "github.com/go-gost/gost/pkg/handler/relay"
|
||||
_ "github.com/go-gost/gost/pkg/handler/sni"
|
||||
_ "github.com/go-gost/gost/pkg/handler/socks/v4"
|
||||
_ "github.com/go-gost/gost/pkg/handler/socks/v5"
|
||||
_ "github.com/go-gost/gost/pkg/handler/ss"
|
||||
_ "github.com/go-gost/gost/pkg/handler/ss/udp"
|
||||
_ "github.com/go-gost/gost/pkg/handler/sshd"
|
||||
_ "github.com/go-gost/gost/pkg/handler/tap"
|
||||
_ "github.com/go-gost/gost/pkg/handler/tun"
|
||||
_ "github.com/go-gost/x/handler/api"
|
||||
_ "github.com/go-gost/x/handler/auto"
|
||||
_ "github.com/go-gost/x/handler/dns"
|
||||
_ "github.com/go-gost/x/handler/file"
|
||||
_ "github.com/go-gost/x/handler/forward/local"
|
||||
_ "github.com/go-gost/x/handler/forward/remote"
|
||||
_ "github.com/go-gost/x/handler/http"
|
||||
_ "github.com/go-gost/x/handler/http2"
|
||||
_ "github.com/go-gost/x/handler/http3"
|
||||
_ "github.com/go-gost/x/handler/metrics"
|
||||
_ "github.com/go-gost/x/handler/redirect/tcp"
|
||||
_ "github.com/go-gost/x/handler/redirect/udp"
|
||||
_ "github.com/go-gost/x/handler/relay"
|
||||
_ "github.com/go-gost/x/handler/router"
|
||||
_ "github.com/go-gost/x/handler/serial"
|
||||
_ "github.com/go-gost/x/handler/sni"
|
||||
_ "github.com/go-gost/x/handler/socks/v4"
|
||||
_ "github.com/go-gost/x/handler/socks/v5"
|
||||
_ "github.com/go-gost/x/handler/ss"
|
||||
_ "github.com/go-gost/x/handler/ss/udp"
|
||||
_ "github.com/go-gost/x/handler/sshd"
|
||||
_ "github.com/go-gost/x/handler/tap"
|
||||
_ "github.com/go-gost/x/handler/tun"
|
||||
_ "github.com/go-gost/x/handler/tunnel"
|
||||
_ "github.com/go-gost/x/handler/unix"
|
||||
|
||||
// Register listeners
|
||||
_ "github.com/go-gost/gost/pkg/listener/dns"
|
||||
_ "github.com/go-gost/gost/pkg/listener/ftcp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/grpc"
|
||||
_ "github.com/go-gost/gost/pkg/listener/http2"
|
||||
_ "github.com/go-gost/gost/pkg/listener/http2/h2"
|
||||
_ "github.com/go-gost/gost/pkg/listener/http3"
|
||||
_ "github.com/go-gost/gost/pkg/listener/kcp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/obfs/http"
|
||||
_ "github.com/go-gost/gost/pkg/listener/obfs/tls"
|
||||
_ "github.com/go-gost/gost/pkg/listener/pht"
|
||||
_ "github.com/go-gost/gost/pkg/listener/quic"
|
||||
_ "github.com/go-gost/gost/pkg/listener/redirect/udp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/rtcp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/rudp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/ssh"
|
||||
_ "github.com/go-gost/gost/pkg/listener/sshd"
|
||||
_ "github.com/go-gost/gost/pkg/listener/tap"
|
||||
_ "github.com/go-gost/gost/pkg/listener/tcp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/tls"
|
||||
_ "github.com/go-gost/gost/pkg/listener/tls/mux"
|
||||
_ "github.com/go-gost/gost/pkg/listener/tun"
|
||||
_ "github.com/go-gost/gost/pkg/listener/udp"
|
||||
_ "github.com/go-gost/gost/pkg/listener/ws"
|
||||
_ "github.com/go-gost/gost/pkg/listener/ws/mux"
|
||||
_ "github.com/go-gost/x/listener/dns"
|
||||
_ "github.com/go-gost/x/listener/dtls"
|
||||
_ "github.com/go-gost/x/listener/ftcp"
|
||||
_ "github.com/go-gost/x/listener/grpc"
|
||||
_ "github.com/go-gost/x/listener/http2"
|
||||
_ "github.com/go-gost/x/listener/http2/h2"
|
||||
_ "github.com/go-gost/x/listener/http3"
|
||||
_ "github.com/go-gost/x/listener/http3/h3"
|
||||
_ "github.com/go-gost/x/listener/http3/wt"
|
||||
_ "github.com/go-gost/x/listener/icmp"
|
||||
_ "github.com/go-gost/x/listener/kcp"
|
||||
_ "github.com/go-gost/x/listener/mtcp"
|
||||
_ "github.com/go-gost/x/listener/mtls"
|
||||
_ "github.com/go-gost/x/listener/mws"
|
||||
_ "github.com/go-gost/x/listener/obfs/http"
|
||||
_ "github.com/go-gost/x/listener/obfs/tls"
|
||||
_ "github.com/go-gost/x/listener/pht"
|
||||
_ "github.com/go-gost/x/listener/quic"
|
||||
_ "github.com/go-gost/x/listener/redirect/tcp"
|
||||
_ "github.com/go-gost/x/listener/redirect/udp"
|
||||
_ "github.com/go-gost/x/listener/rtcp"
|
||||
_ "github.com/go-gost/x/listener/rudp"
|
||||
_ "github.com/go-gost/x/listener/serial"
|
||||
_ "github.com/go-gost/x/listener/ssh"
|
||||
_ "github.com/go-gost/x/listener/sshd"
|
||||
_ "github.com/go-gost/x/listener/tap"
|
||||
_ "github.com/go-gost/x/listener/tcp"
|
||||
_ "github.com/go-gost/x/listener/tls"
|
||||
_ "github.com/go-gost/x/listener/tun"
|
||||
_ "github.com/go-gost/x/listener/udp"
|
||||
_ "github.com/go-gost/x/listener/unix"
|
||||
_ "github.com/go-gost/x/listener/ws"
|
||||
)
|
||||
|
||||
-107
@@ -1,107 +0,0 @@
|
||||
package main
|
||||
|
||||
import (
|
||||
"crypto/rand"
|
||||
"crypto/rsa"
|
||||
"crypto/tls"
|
||||
"crypto/x509"
|
||||
"crypto/x509/pkix"
|
||||
"encoding/pem"
|
||||
"math/big"
|
||||
"time"
|
||||
|
||||
tls_util "github.com/go-gost/gost/pkg/common/util/tls"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
)
|
||||
|
||||
func buildDefaultTLSConfig(cfg *config.TLSConfig) {
|
||||
if cfg == nil {
|
||||
cfg = &config.TLSConfig{
|
||||
CertFile: "cert.pem",
|
||||
KeyFile: "key.pem",
|
||||
}
|
||||
}
|
||||
|
||||
tlsConfig, err := loadConfig(cfg.CertFile, cfg.KeyFile)
|
||||
if err != nil {
|
||||
// generate random self-signed certificate.
|
||||
cert, err := genCertificate()
|
||||
if err != nil {
|
||||
log.Fatal(err)
|
||||
}
|
||||
tlsConfig = &tls.Config{
|
||||
Certificates: []tls.Certificate{cert},
|
||||
}
|
||||
log.Warn("load TLS certificate files failed, use random generated certificate")
|
||||
} else {
|
||||
log.Info("load TLS certificate files OK")
|
||||
}
|
||||
tls_util.DefaultConfig = tlsConfig
|
||||
}
|
||||
|
||||
func loadConfig(certFile, keyFile string) (*tls.Config, error) {
|
||||
cert, err := tls.LoadX509KeyPair(certFile, keyFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cfg := &tls.Config{
|
||||
Certificates: []tls.Certificate{cert},
|
||||
}
|
||||
|
||||
return cfg, nil
|
||||
}
|
||||
|
||||
func genCertificate() (cert tls.Certificate, err error) {
|
||||
rawCert, rawKey, err := generateKeyPair()
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
return tls.X509KeyPair(rawCert, rawKey)
|
||||
}
|
||||
|
||||
func generateKeyPair() (rawCert, rawKey []byte, err error) {
|
||||
// Create private key and self-signed certificate
|
||||
// Adapted from https://golang.org/src/crypto/tls/generate_cert.go
|
||||
|
||||
priv, err := rsa.GenerateKey(rand.Reader, 2048)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
validFor := time.Hour * 24 * 365 * 10 // ten years
|
||||
notBefore := time.Now()
|
||||
notAfter := notBefore.Add(validFor)
|
||||
serialNumberLimit := new(big.Int).Lsh(big.NewInt(1), 128)
|
||||
serialNumber, err := rand.Int(rand.Reader, serialNumberLimit)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
template := x509.Certificate{
|
||||
SerialNumber: serialNumber,
|
||||
Subject: pkix.Name{
|
||||
Organization: []string{"gost"},
|
||||
},
|
||||
NotBefore: notBefore,
|
||||
NotAfter: notAfter,
|
||||
|
||||
KeyUsage: x509.KeyUsageKeyEncipherment | x509.KeyUsageDigitalSignature,
|
||||
ExtKeyUsage: []x509.ExtKeyUsage{x509.ExtKeyUsageServerAuth},
|
||||
BasicConstraintsValid: true,
|
||||
}
|
||||
|
||||
template.DNSNames = append(template.DNSNames, "gost.run")
|
||||
derBytes, err := x509.CreateCertificate(rand.Reader, &template, &template, &priv.PublicKey, priv)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
rawCert = pem.EncodeToMemory(&pem.Block{Type: "CERTIFICATE", Bytes: derBytes})
|
||||
privBytes, err := x509.MarshalPKCS8PrivateKey(priv)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
rawKey = pem.EncodeToMemory(&pem.Block{Type: "PRIVATE KEY", Bytes: privBytes})
|
||||
|
||||
return
|
||||
}
|
||||
+2
-2
@@ -1,5 +1,5 @@
|
||||
package main
|
||||
|
||||
const (
|
||||
version = "3.0.0-alpha.2"
|
||||
var (
|
||||
version = "3.1.0"
|
||||
)
|
||||
|
||||
@@ -1,4 +0,0 @@
|
||||
version: "3.4"
|
||||
services:
|
||||
gost:
|
||||
build: .
|
||||
@@ -1,85 +1,123 @@
|
||||
module github.com/go-gost/gost
|
||||
|
||||
go 1.17
|
||||
go 1.23.0
|
||||
|
||||
toolchain go1.23.4
|
||||
|
||||
require (
|
||||
github.com/LiamHaworth/go-tproxy v0.0.0-20190726054950-ef7efd7f24ed
|
||||
github.com/aead/chacha20 v0.0.0-20180709150244-8b13a72661da // indirect
|
||||
github.com/asaskevich/govalidator v0.0.0-20210307081110-f21760c49a8d
|
||||
github.com/cheekybits/genny v1.0.0 // indirect
|
||||
github.com/go-gost/core v0.3.2
|
||||
github.com/go-gost/x v0.5.7
|
||||
github.com/judwhite/go-svc v1.2.1
|
||||
)
|
||||
|
||||
require (
|
||||
github.com/alecthomas/units v0.0.0-20211218093645-b94a6e3cc137 // indirect
|
||||
github.com/alessio/shellescape v1.4.1 // indirect
|
||||
github.com/asaskevich/govalidator v0.0.0-20210307081110-f21760c49a8d // indirect
|
||||
github.com/beorn7/perks v1.0.1 // indirect
|
||||
github.com/bytedance/sonic v1.11.6 // indirect
|
||||
github.com/bytedance/sonic/loader v0.1.1 // indirect
|
||||
github.com/cespare/xxhash/v2 v2.3.0 // indirect
|
||||
github.com/cloudwego/base64x v0.1.4 // indirect
|
||||
github.com/cloudwego/iasm v0.2.0 // indirect
|
||||
github.com/coreos/go-iptables v0.5.0 // indirect
|
||||
github.com/docker/libcontainer v2.2.1+incompatible
|
||||
github.com/fsnotify/fsnotify v1.5.1 // indirect
|
||||
github.com/gin-contrib/cors v1.3.1
|
||||
github.com/gin-gonic/gin v1.7.7
|
||||
github.com/go-gost/gosocks4 v0.0.1
|
||||
github.com/go-gost/gosocks5 v0.3.1-0.20211109033403-d894d75b7f09
|
||||
github.com/go-gost/relay v0.1.1-0.20211123134818-8ef7fd81ffd7
|
||||
github.com/go-gost/tls-dissector v0.0.2-0.20211125135007-2b5d5bd9c07e
|
||||
github.com/go-task/slim-sprig v0.0.0-20210107165309-348f09dbbbc0 // indirect
|
||||
github.com/gobwas/glob v0.2.3
|
||||
github.com/golang/snappy v0.0.3
|
||||
github.com/google/gopacket v1.1.19 // indirect
|
||||
github.com/gorilla/websocket v1.4.2
|
||||
github.com/hashicorp/hcl v1.0.0 // indirect
|
||||
github.com/klauspost/cpuid v1.3.1 // indirect
|
||||
github.com/klauspost/reedsolomon v1.9.9 // indirect
|
||||
github.com/lucas-clemente/quic-go v0.24.0
|
||||
github.com/magiconair/properties v1.8.5 // indirect
|
||||
github.com/marten-seemann/qtls-go1-16 v0.1.4 // indirect
|
||||
github.com/marten-seemann/qtls-go1-17 v0.1.0 // indirect
|
||||
github.com/miekg/dns v1.1.45
|
||||
github.com/milosgajdos/tenus v0.0.3
|
||||
github.com/mitchellh/mapstructure v1.4.2 // indirect
|
||||
github.com/mmcloughlin/avo v0.0.0-20200803215136-443f81d77104 // indirect
|
||||
github.com/nxadm/tail v1.4.8 // indirect
|
||||
github.com/onsi/ginkgo v1.16.4 // indirect
|
||||
github.com/pelletier/go-toml v1.9.4 // indirect
|
||||
github.com/pkg/errors v0.9.1 // indirect
|
||||
github.com/riobard/go-bloom v0.0.0-20200614022211-cdc8013cb5b3 // indirect
|
||||
github.com/rs/xid v1.3.0
|
||||
github.com/shadowsocks/go-shadowsocks2 v0.1.4
|
||||
github.com/shadowsocks/shadowsocks-go v0.0.0-20200409064450-3e585ff90601
|
||||
github.com/sirupsen/logrus v1.8.1
|
||||
github.com/songgao/water v0.0.0-20200317203138-2b4b6d7c09d8
|
||||
github.com/spf13/afero v1.6.0 // indirect
|
||||
github.com/spf13/cast v1.4.1 // indirect
|
||||
github.com/spf13/jwalterweatherman v1.1.0 // indirect
|
||||
github.com/spf13/pflag v1.0.5 // indirect
|
||||
github.com/spf13/viper v1.9.0
|
||||
github.com/subosito/gotenv v1.2.0 // indirect
|
||||
github.com/templexxx/cpu v0.0.7 // indirect
|
||||
github.com/templexxx/xorsimd v0.4.1 // indirect
|
||||
github.com/tjfoc/gmsm v1.3.2 // indirect
|
||||
github.com/xtaci/kcp-go/v5 v5.6.1
|
||||
github.com/xtaci/smux v1.5.16
|
||||
github.com/xtaci/tcpraw v1.2.25
|
||||
golang.org/x/crypto v0.0.0-20211215153901-e495a2d5b3d3
|
||||
golang.org/x/mod v0.4.2 // indirect
|
||||
golang.org/x/net v0.0.0-20220127200216-cd36cc0744dd
|
||||
golang.org/x/sys v0.0.0-20220114195835-da31bd327af9 // indirect
|
||||
golang.org/x/text v0.3.7 // indirect
|
||||
golang.org/x/tools v0.1.6-0.20210726203631-07bc1bf47fb2 // indirect
|
||||
golang.org/x/xerrors v0.0.0-20200804184101-5ec99f83aff1 // indirect
|
||||
google.golang.org/grpc v1.44.0
|
||||
google.golang.org/protobuf v1.27.1
|
||||
gopkg.in/ini.v1 v1.63.2 // indirect
|
||||
gopkg.in/tomb.v1 v1.0.0-20141024135613-dd632973f1e7 // indirect
|
||||
gopkg.in/yaml.v2 v2.4.0
|
||||
)
|
||||
|
||||
require (
|
||||
github.com/danieljoos/wincred v1.2.0 // indirect
|
||||
github.com/dgryski/go-rendezvous v0.0.0-20200823014737-9f7001d12a5f // indirect
|
||||
github.com/fsnotify/fsnotify v1.7.0 // indirect
|
||||
github.com/gabriel-vasile/mimetype v1.4.3 // indirect
|
||||
github.com/gin-contrib/cors v1.7.2 // indirect
|
||||
github.com/gin-contrib/sse v0.1.0 // indirect
|
||||
github.com/go-playground/locales v0.13.0 // indirect
|
||||
github.com/go-playground/universal-translator v0.17.0 // indirect
|
||||
github.com/go-playground/validator/v10 v10.4.1 // indirect
|
||||
github.com/golang/protobuf v1.5.2 // indirect
|
||||
github.com/json-iterator/go v1.1.11 // indirect
|
||||
github.com/leodido/go-urn v1.2.0 // indirect
|
||||
github.com/marten-seemann/qpack v0.2.1 // indirect
|
||||
github.com/mattn/go-isatty v0.0.12 // indirect
|
||||
github.com/gin-gonic/gin v1.10.0 // indirect
|
||||
github.com/go-gost/gosocks4 v0.0.1 // indirect
|
||||
github.com/go-gost/gosocks5 v0.4.2 // indirect
|
||||
github.com/go-gost/plugin v0.2.0 // indirect
|
||||
github.com/go-gost/relay v0.5.0 // indirect
|
||||
github.com/go-gost/tls-dissector v0.1.1 // indirect
|
||||
github.com/go-playground/locales v0.14.1 // indirect
|
||||
github.com/go-playground/universal-translator v0.18.1 // indirect
|
||||
github.com/go-playground/validator/v10 v10.20.0 // indirect
|
||||
github.com/go-redis/redis/v8 v8.11.5 // indirect
|
||||
github.com/gobwas/glob v0.2.3 // indirect
|
||||
github.com/goccy/go-json v0.10.2 // indirect
|
||||
github.com/godbus/dbus/v5 v5.1.0 // indirect
|
||||
github.com/golang/snappy v0.0.4 // indirect
|
||||
github.com/google/gopacket v1.1.19 // indirect
|
||||
github.com/google/uuid v1.6.0 // indirect
|
||||
github.com/gorilla/websocket v1.5.3 // indirect
|
||||
github.com/gravitational/trace v1.1.16-0.20220114165159-14a9a7dd6aaf // indirect
|
||||
github.com/hashicorp/hcl v1.0.0 // indirect
|
||||
github.com/jonboulle/clockwork v0.2.2 // indirect
|
||||
github.com/json-iterator/go v1.1.12 // indirect
|
||||
github.com/klauspost/cpuid/v2 v2.2.7 // indirect
|
||||
github.com/klauspost/reedsolomon v1.11.8 // indirect
|
||||
github.com/leodido/go-urn v1.4.0 // indirect
|
||||
github.com/magiconair/properties v1.8.7 // indirect
|
||||
github.com/mattn/go-isatty v0.0.20 // indirect
|
||||
github.com/miekg/dns v1.1.61 // indirect
|
||||
github.com/mitchellh/go-homedir v1.1.0 // indirect
|
||||
github.com/mitchellh/mapstructure v1.5.0 // indirect
|
||||
github.com/modern-go/concurrent v0.0.0-20180306012644-bacd9c7ef1dd // indirect
|
||||
github.com/modern-go/reflect2 v1.0.1 // indirect
|
||||
github.com/ugorji/go/codec v1.1.7 // indirect
|
||||
google.golang.org/genproto v0.0.0-20220126215142-9970aeb2e350 // indirect
|
||||
github.com/modern-go/reflect2 v1.0.2 // indirect
|
||||
github.com/patrickmn/go-cache v2.1.0+incompatible // indirect
|
||||
github.com/pelletier/go-toml/v2 v2.2.2 // indirect
|
||||
github.com/pion/dtls/v2 v2.2.6 // indirect
|
||||
github.com/pion/logging v0.2.2 // indirect
|
||||
github.com/pion/transport/v2 v2.0.2 // indirect
|
||||
github.com/pion/udp/v2 v2.0.1 // indirect
|
||||
github.com/pires/go-proxyproto v0.7.0 // indirect
|
||||
github.com/pkg/errors v0.9.1 // indirect
|
||||
github.com/prometheus/client_golang v1.19.1 // indirect
|
||||
github.com/prometheus/client_model v0.6.0 // indirect
|
||||
github.com/prometheus/common v0.48.0 // indirect
|
||||
github.com/prometheus/procfs v0.12.0 // indirect
|
||||
github.com/quic-go/qpack v0.5.1 // indirect
|
||||
github.com/quic-go/quic-go v0.53.0 // indirect
|
||||
github.com/quic-go/webtransport-go v0.9.0 // indirect
|
||||
github.com/riobard/go-bloom v0.0.0-20200614022211-cdc8013cb5b3 // indirect
|
||||
github.com/rs/xid v1.3.0 // indirect
|
||||
github.com/sagikazarmark/locafero v0.4.0 // indirect
|
||||
github.com/sagikazarmark/slog-shim v0.1.0 // indirect
|
||||
github.com/shadowsocks/go-shadowsocks2 v0.1.6-0.20241020092332-e1fe9ea73740 // indirect
|
||||
github.com/sirupsen/logrus v1.8.1 // indirect
|
||||
github.com/songgao/water v0.0.0-20200317203138-2b4b6d7c09d8 // indirect
|
||||
github.com/sourcegraph/conc v0.3.0 // indirect
|
||||
github.com/spf13/afero v1.11.0 // indirect
|
||||
github.com/spf13/cast v1.6.0 // indirect
|
||||
github.com/spf13/pflag v1.0.5 // indirect
|
||||
github.com/spf13/viper v1.19.0 // indirect
|
||||
github.com/subosito/gotenv v1.6.0 // indirect
|
||||
github.com/templexxx/cpu v0.1.1 // indirect
|
||||
github.com/templexxx/xorsimd v0.4.3 // indirect
|
||||
github.com/tjfoc/gmsm v1.4.1 // indirect
|
||||
github.com/twitchyliquid64/golang-asm v0.15.1 // indirect
|
||||
github.com/ugorji/go/codec v1.2.12 // indirect
|
||||
github.com/vishvananda/netlink v1.1.0 // indirect
|
||||
github.com/vishvananda/netns v0.0.4 // indirect
|
||||
github.com/vulcand/predicate v1.2.0 // indirect
|
||||
github.com/xtaci/kcp-go/v5 v5.6.5 // indirect
|
||||
github.com/xtaci/smux v1.5.31 // indirect
|
||||
github.com/xtaci/tcpraw v1.2.25 // indirect
|
||||
github.com/yl2chen/cidranger v1.0.2 // indirect
|
||||
github.com/zalando/go-keyring v0.2.4 // indirect
|
||||
go.uber.org/mock v0.5.0 // indirect
|
||||
go.uber.org/multierr v1.11.0 // indirect
|
||||
golang.org/x/arch v0.8.0 // indirect
|
||||
golang.org/x/crypto v0.39.0 // indirect
|
||||
golang.org/x/exp v0.0.0-20241210194714-1829a127f884 // indirect
|
||||
golang.org/x/mod v0.25.0 // indirect
|
||||
golang.org/x/net v0.40.0 // indirect
|
||||
golang.org/x/sync v0.15.0 // indirect
|
||||
golang.org/x/sys v0.33.0 // indirect
|
||||
golang.org/x/term v0.32.0 // indirect
|
||||
golang.org/x/text v0.26.0 // indirect
|
||||
golang.org/x/time v0.5.0 // indirect
|
||||
golang.org/x/tools v0.33.0 // indirect
|
||||
golang.zx2c4.com/wintun v0.0.0-20230126152724-0fa3db229ce2 // indirect
|
||||
golang.zx2c4.com/wireguard v0.0.0-20231211153847-12269c276173 // indirect
|
||||
google.golang.org/genproto/googleapis/rpc v0.0.0-20240903143218-8af14fe29dc1 // indirect
|
||||
google.golang.org/grpc v1.67.1 // indirect
|
||||
google.golang.org/protobuf v1.35.1 // indirect
|
||||
gopkg.in/ini.v1 v1.67.0 // indirect
|
||||
gopkg.in/natefinch/lumberjack.v2 v2.2.1 // indirect
|
||||
gopkg.in/yaml.v3 v3.0.1 // indirect
|
||||
)
|
||||
|
||||
@@ -1,283 +1,145 @@
|
||||
log:
|
||||
output: stderr # none, stderr, stdout, /path/to/file
|
||||
level: debug # debug, info, warn, error, fatal
|
||||
format: json # text, json
|
||||
|
||||
services:
|
||||
- name: http+tcp
|
||||
addr: ":28000"
|
||||
# bypass: bypass01
|
||||
- name: service-0
|
||||
addr: ":8080"
|
||||
interface: eth0
|
||||
admission: admission-0
|
||||
bypass: bypass-0
|
||||
resolver: resolver-0
|
||||
hosts: hosts-0
|
||||
handler:
|
||||
type: http
|
||||
chain: chain01
|
||||
metadata:
|
||||
proxyAgent: "gost/3.0"
|
||||
auths:
|
||||
- user1:pass1
|
||||
- user2:pass2
|
||||
# probeResist: code:404 # code, web, host, file
|
||||
# knock: example.com
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
auther: auther-0
|
||||
chain: chain-0
|
||||
retries: 1
|
||||
metadata:
|
||||
foo: bar
|
||||
bar: baz
|
||||
listener:
|
||||
type: tcp
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
auther: auther-0
|
||||
chain: chain-0
|
||||
tls:
|
||||
certFile: cert.pem
|
||||
keyFile: key.pem
|
||||
caFile: ca.pem
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
- name: ss
|
||||
addr: ":28338"
|
||||
# bypass: bypass01
|
||||
handler:
|
||||
type: ss
|
||||
# chain: chain01
|
||||
metadata:
|
||||
method: chacha20-ietf
|
||||
password: gost
|
||||
readTimeout: 5s
|
||||
udp: true
|
||||
bufferSize: 4096
|
||||
listener:
|
||||
type: tcp
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
- name: socks5
|
||||
addr: ":21080"
|
||||
# bypass: bypass01
|
||||
handler:
|
||||
type: socks5
|
||||
# chain: chain-ss
|
||||
metadata:
|
||||
auths:
|
||||
- gost:gost
|
||||
readTimeout: 5s
|
||||
notls: true
|
||||
bind: true
|
||||
udp: true
|
||||
# udpBufferSize: 4096 # range [512, 66560]
|
||||
listener:
|
||||
type: tcp
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
- name: socks5+tcp
|
||||
addr: ":21081"
|
||||
handler:
|
||||
type: socks5
|
||||
metadata:
|
||||
auths:
|
||||
- gost:gost
|
||||
readTimeout: 5s
|
||||
notls: true
|
||||
# udpBufferSize: 1024
|
||||
listener:
|
||||
type: tcp
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
- name: forward
|
||||
addr: ":10053"
|
||||
abc: xyz
|
||||
def: 456
|
||||
forwarder:
|
||||
targets:
|
||||
- 192.168.8.8:53
|
||||
- 192.168.8.1:53
|
||||
- 1.1.1.1:53
|
||||
nodes:
|
||||
- name: target-0
|
||||
addr: 192.168.1.1:1234
|
||||
- name: target-1
|
||||
addr: 192.168.1.2:2345
|
||||
selector:
|
||||
strategy: fifo
|
||||
strategy: rand
|
||||
maxFails: 1
|
||||
failTimeout: 30s
|
||||
handler:
|
||||
type: forward
|
||||
chain: chain-ss
|
||||
metadata:
|
||||
readTimeout: 5s
|
||||
listener:
|
||||
type: udp
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
|
||||
- name: kcp-forward-tunnel
|
||||
addr: ":8388"
|
||||
forwarder:
|
||||
targets:
|
||||
- 127.0.0.1:28338
|
||||
handler:
|
||||
type: forward
|
||||
metadata:
|
||||
readTimeout: 5s
|
||||
listener:
|
||||
type: kcp
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
|
||||
- name: rtcp
|
||||
addr: ":28100"
|
||||
forwarder:
|
||||
targets:
|
||||
- 192.168.8.8:80
|
||||
handler:
|
||||
type: forward
|
||||
metadata:
|
||||
readTimeout: 5s
|
||||
listener:
|
||||
type: rtcp
|
||||
# chain: chain-socks5
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
mux: true
|
||||
- name: rudp
|
||||
addr: ":1053"
|
||||
forwarder:
|
||||
targets:
|
||||
- 192.168.8.8:53
|
||||
- 192.168.8.1:53
|
||||
selector:
|
||||
strategy: round
|
||||
maxFails: 1
|
||||
failTimeout: 30s
|
||||
handler:
|
||||
type: forward
|
||||
metadata:
|
||||
readTimeout: 5s
|
||||
listener:
|
||||
type: rudp
|
||||
chain: chain-socks5
|
||||
metadata:
|
||||
keepAlive: 15s
|
||||
|
||||
chains:
|
||||
- name: chain01
|
||||
# chain level selector
|
||||
- name: chain-0
|
||||
selector:
|
||||
strategy: round
|
||||
maxFails: 1
|
||||
failTimeout: 30s
|
||||
hops:
|
||||
- name: hop01
|
||||
# hop level selector
|
||||
- name: hop-0
|
||||
- name: hop-1
|
||||
interface: 192.168.1.2
|
||||
selector:
|
||||
strategy: round
|
||||
maxFails: 1
|
||||
failTimeout: 30s
|
||||
strategy: rand
|
||||
maxFails: 3
|
||||
failTimeout: 60s
|
||||
bypass: bypass-0
|
||||
nodes:
|
||||
- name: node01
|
||||
addr: ":8081"
|
||||
# bypass: bypass01
|
||||
connector:
|
||||
type: http
|
||||
metadata:
|
||||
userAgent: "gost/3.0"
|
||||
auth: user1:pass1
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
- name: node02
|
||||
addr: ":8082"
|
||||
# bypass: bypass01
|
||||
connector:
|
||||
type: http
|
||||
metadata:
|
||||
userAgent: "gost/3.0"
|
||||
auth: user2:pass2
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
- name: hop02
|
||||
# hop level selector
|
||||
selector:
|
||||
strategy: round
|
||||
maxFails: 1
|
||||
failTimeout: 30s
|
||||
nodes:
|
||||
- name: node03
|
||||
addr: ":8083"
|
||||
# bypass: bypass01
|
||||
connector:
|
||||
type: http
|
||||
metadata:
|
||||
userAgent: "gost/3.0"
|
||||
auth: user3:pass3
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
- name: chain-socks4
|
||||
hops:
|
||||
- name: hop01
|
||||
nodes:
|
||||
- name: node01
|
||||
addr: ":8081"
|
||||
url: "http://gost:gost@:8081"
|
||||
# bypass: bypass01
|
||||
connector:
|
||||
type: socks4
|
||||
metadata: {}
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
- name: chain-socks5
|
||||
hops:
|
||||
- name: hop01
|
||||
nodes:
|
||||
- name: node01
|
||||
addr: ":21080"
|
||||
# bypass: bypass01
|
||||
- name: node-0
|
||||
addr: ":1080"
|
||||
interface: eth1
|
||||
bypass: bypass-0
|
||||
connector:
|
||||
type: socks5
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
metadata:
|
||||
notls: true
|
||||
auth: gost:gost
|
||||
foo: bar
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
- name: chain-ss
|
||||
hops:
|
||||
- name: hop01
|
||||
nodes:
|
||||
- name: node01
|
||||
addr: ":28338"
|
||||
url: "http://gost:gost@:8081"
|
||||
# bypass: bypass01
|
||||
connector:
|
||||
type: ss
|
||||
metadata:
|
||||
method: chacha20-ietf
|
||||
password: gost
|
||||
readTimeout: 5s
|
||||
nodelay: true
|
||||
udp: true
|
||||
bufferSize: 4096
|
||||
dialer:
|
||||
type: tcp
|
||||
metadata: {}
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
tls:
|
||||
caFile: "ca.pem"
|
||||
secure: true
|
||||
serverName: "example.com"
|
||||
metadata:
|
||||
bar: baz
|
||||
|
||||
hops:
|
||||
- name: hop-0
|
||||
interface: 192.168.1.2
|
||||
selector:
|
||||
strategy: rand
|
||||
maxFails: 3
|
||||
failTimeout: 60s
|
||||
bypass: bypass-0
|
||||
nodes:
|
||||
- name: node-0
|
||||
addr: ":1080"
|
||||
interface: eth1
|
||||
bypass: bypass-0
|
||||
connector:
|
||||
type: socks5
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
metadata:
|
||||
foo: bar
|
||||
dialer:
|
||||
type: tcp
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
tls:
|
||||
caFile: "ca.pem"
|
||||
secure: true
|
||||
serverName: "example.com"
|
||||
metadata:
|
||||
bar: baz
|
||||
|
||||
tls:
|
||||
certFile: "cert.pem"
|
||||
keyFile: "key.pem"
|
||||
caFile: "ca.pem"
|
||||
|
||||
authers:
|
||||
- name: auther-0
|
||||
auths:
|
||||
- username: user1
|
||||
password: pass1
|
||||
- username: user2
|
||||
password: pass2
|
||||
|
||||
admissions:
|
||||
- name: admission-0
|
||||
whitelist: false
|
||||
matchers:
|
||||
- 127.0.0.1
|
||||
- 192.168.0.0/16
|
||||
|
||||
bypasses:
|
||||
- name: bypass-0
|
||||
reverse: false
|
||||
whitelist: false
|
||||
matchers:
|
||||
- .baidu.com
|
||||
- "*.example.com" # domain wildcard
|
||||
- .example.org # will match example.org and *.example.org
|
||||
|
||||
# From IANA IPv4 Special-Purpose Address Registry
|
||||
# http://www.iana.org/assignments/iana-ipv4-special-registry/iana-ipv4-special-registry.xhtml
|
||||
- 0.0.0.0/8 # RFC1122: "This host on this network"
|
||||
- 10.0.0.0/8 # RFC1918: Private-Use
|
||||
- 100.64.0.0/10 # RFC6598: Shared Address Space
|
||||
- 127.0.0.0/8 # RFC1122: Loopback
|
||||
- 169.254.0.0/16 # RFC3927: Link Local
|
||||
- 172.16.0.0/12 # RFC1918: Private-Use
|
||||
- 192.0.0.0/24 # RFC6890: IETF Protocol Assignments
|
||||
- 192.0.2.0/24 # RFC5737: Documentation (TEST-NET-1)
|
||||
- 192.88.99.0/24 # RFC3068: 6to4 Relay Anycast
|
||||
- 192.168.0.0/16 # RFC1918: Private-Use
|
||||
- 198.18.0.0/15 # RFC2544: Benchmarking
|
||||
- 198.51.100.0/24 # RFC5737: Documentation (TEST-NET-2)
|
||||
- 203.0.113.0/24 # RFC5737: Documentation (TEST-NET-3)
|
||||
- 240.0.0.0/4 # RFC1112: Reserved
|
||||
- 255.255.255.255/32 # RFC0919: Limited Broadcast
|
||||
|
||||
# From IANA Multicast Address Space Registry
|
||||
# http://www.iana.org/assignments/multicast-addresses/multicast-addresses.xhtml
|
||||
- 224.0.0.0/4 # RFC5771: Multicast/Reserved
|
||||
|
||||
tls:
|
||||
cert: "cert.pem"
|
||||
key: "key.pem"
|
||||
# ca: "root.ca"
|
||||
- "*.example.com"
|
||||
- .example.org
|
||||
- 0.0.0.0/8
|
||||
|
||||
resolvers:
|
||||
- name: resolver-0
|
||||
@@ -308,6 +170,23 @@ hosts:
|
||||
- bar
|
||||
- baz
|
||||
|
||||
log:
|
||||
output: stderr
|
||||
level: debug
|
||||
format: json
|
||||
|
||||
profiling:
|
||||
addr: ":6060"
|
||||
enabled: true
|
||||
|
||||
api:
|
||||
addr: ":18080"
|
||||
pathPrefix: /api
|
||||
accesslog: true
|
||||
auth:
|
||||
username: user
|
||||
password: pass
|
||||
auther: auther-0
|
||||
|
||||
metrics:
|
||||
addr: :9000
|
||||
path: /metrics
|
||||
|
||||
Executable
+103
@@ -0,0 +1,103 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Check Root User
|
||||
|
||||
# If you want to run as another user, please modify $EUID to be owned by this user
|
||||
if [[ "$EUID" -ne '0' ]]; then
|
||||
echo "$(tput setaf 1)Error: You must run this script as root!$(tput sgr0)"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Set the desired GitHub repository
|
||||
repo="go-gost/gost"
|
||||
base_url="https://api.github.com/repos/$repo/releases"
|
||||
|
||||
# Function to download and install gost
|
||||
install_gost() {
|
||||
version=$1
|
||||
# Detect the operating system
|
||||
if [[ "$(uname)" == "Linux" ]]; then
|
||||
os="linux"
|
||||
elif [[ "$(uname)" == "Darwin" ]]; then
|
||||
os="darwin"
|
||||
elif [[ "$(uname)" == "MINGW"* ]]; then
|
||||
os="windows"
|
||||
else
|
||||
echo "Unsupported operating system."
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Detect the CPU architecture
|
||||
arch=$(uname -m)
|
||||
case $arch in
|
||||
x86_64)
|
||||
cpu_arch="amd64"
|
||||
;;
|
||||
armv5*)
|
||||
cpu_arch="armv5"
|
||||
;;
|
||||
armv6*)
|
||||
cpu_arch="armv6"
|
||||
;;
|
||||
armv7*)
|
||||
cpu_arch="armv7"
|
||||
;;
|
||||
aarch64)
|
||||
cpu_arch="arm64"
|
||||
;;
|
||||
i686)
|
||||
cpu_arch="386"
|
||||
;;
|
||||
mips64*)
|
||||
cpu_arch="mips64"
|
||||
;;
|
||||
mips*)
|
||||
cpu_arch="mips"
|
||||
;;
|
||||
mipsel*)
|
||||
cpu_arch="mipsle"
|
||||
;;
|
||||
riscv64)
|
||||
cpu_arch="riscv64"
|
||||
;;
|
||||
*)
|
||||
echo "Unsupported CPU architecture."
|
||||
exit 1
|
||||
;;
|
||||
esac
|
||||
get_download_url="$base_url/tags/$version"
|
||||
download_url=$(curl -s "$get_download_url" | grep -Eo "\"browser_download_url\": \".*${os}.*${cpu_arch}.*\"" | awk -F'["]' '{print $4}')
|
||||
|
||||
# Download the binary
|
||||
echo "Downloading gost version $version..."
|
||||
curl -fsSL -o gost.tar.gz $download_url
|
||||
|
||||
# Extract and install the binary
|
||||
echo "Installing gost..."
|
||||
tar -xzf gost.tar.gz
|
||||
chmod +x gost
|
||||
mv gost /usr/local/bin/gost
|
||||
|
||||
echo "gost installation completed!"
|
||||
}
|
||||
|
||||
# Retrieve available versions from GitHub API
|
||||
versions=$(curl -s "$base_url" | grep -oP 'tag_name": "\K[^"]+')
|
||||
|
||||
# Check if --install option provided
|
||||
if [[ "$1" == "--install" ]]; then
|
||||
# Install the latest version automatically
|
||||
latest_version=$(echo "$versions" | head -n 1)
|
||||
install_gost $latest_version
|
||||
else
|
||||
# Display available versions to the user
|
||||
echo "Available gost versions:"
|
||||
select version in $versions; do
|
||||
if [[ -n $version ]]; then
|
||||
install_gost $version
|
||||
break
|
||||
else
|
||||
echo "Invalid choice! Please select a valid option."
|
||||
fi
|
||||
done
|
||||
fi
|
||||
@@ -1,85 +0,0 @@
|
||||
package admission
|
||||
|
||||
import (
|
||||
"net"
|
||||
"strconv"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/matcher"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type Admission interface {
|
||||
Admit(addr string) bool
|
||||
}
|
||||
|
||||
type options struct {
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
type Option func(opts *options)
|
||||
|
||||
func LoggerOption(logger logger.Logger) Option {
|
||||
return func(opts *options) {
|
||||
opts.logger = logger
|
||||
}
|
||||
}
|
||||
|
||||
type admission struct {
|
||||
matchers []matcher.Matcher
|
||||
reversed bool
|
||||
options options
|
||||
}
|
||||
|
||||
// NewAdmission creates and initializes a new Admission using matchers as its match rules.
|
||||
// The rules will be reversed if the reversed is true.
|
||||
func NewAdmission(reversed bool, matchers []matcher.Matcher, opts ...Option) Admission {
|
||||
options := options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
return &admission{
|
||||
matchers: matchers,
|
||||
reversed: reversed,
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
// NewAdmissionPatterns creates and initializes a new Admission using matcher patterns as its match rules.
|
||||
// The rules will be reversed if the reverse is true.
|
||||
func NewAdmissionPatterns(reversed bool, patterns []string, opts ...Option) Admission {
|
||||
var matchers []matcher.Matcher
|
||||
for _, pattern := range patterns {
|
||||
if m := matcher.NewMatcher(pattern); m != nil {
|
||||
matchers = append(matchers, m)
|
||||
}
|
||||
}
|
||||
return NewAdmission(reversed, matchers, opts...)
|
||||
}
|
||||
|
||||
func (p *admission) Admit(addr string) bool {
|
||||
if addr == "" || p == nil || len(p.matchers) == 0 {
|
||||
return false
|
||||
}
|
||||
|
||||
// try to strip the port
|
||||
if host, port, _ := net.SplitHostPort(addr); host != "" && port != "" {
|
||||
if p, _ := strconv.Atoi(port); p > 0 { // port is valid
|
||||
addr = host
|
||||
}
|
||||
}
|
||||
|
||||
var matched bool
|
||||
for _, matcher := range p.matchers {
|
||||
if matcher == nil {
|
||||
continue
|
||||
}
|
||||
if matcher.Match(addr) {
|
||||
matched = true
|
||||
break
|
||||
}
|
||||
}
|
||||
|
||||
b := !p.reversed && matched ||
|
||||
p.reversed && !matched
|
||||
return b
|
||||
}
|
||||
@@ -1,15 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"embed"
|
||||
)
|
||||
|
||||
var (
|
||||
//go:embed swagger.yaml
|
||||
swaggerDoc embed.FS
|
||||
)
|
||||
|
||||
type Response struct {
|
||||
Code int `json:"code,omitempty"`
|
||||
Msg string `json:"msg,omitempty"`
|
||||
}
|
||||
@@ -1,118 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"fmt"
|
||||
"net/http"
|
||||
"os"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
)
|
||||
|
||||
// swagger:parameters getConfigRequest
|
||||
type getConfigRequest struct {
|
||||
// output format, one of yaml|json, default is json.
|
||||
// in: query
|
||||
Format string `form:"format" json:"format"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response getConfigResponse
|
||||
type getConfigResponse struct {
|
||||
Config *config.Config
|
||||
}
|
||||
|
||||
func getConfig(ctx *gin.Context) {
|
||||
// swagger:route GET /config ConfigManagement getConfigRequest
|
||||
//
|
||||
// Get current config.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: getConfigResponse
|
||||
|
||||
var req getConfigRequest
|
||||
ctx.ShouldBindQuery(&req)
|
||||
|
||||
var resp getConfigResponse
|
||||
resp.Config = config.Global()
|
||||
|
||||
buf := &bytes.Buffer{}
|
||||
switch req.Format {
|
||||
case "yaml":
|
||||
default:
|
||||
req.Format = "json"
|
||||
}
|
||||
|
||||
resp.Config.Write(buf, req.Format)
|
||||
|
||||
contentType := "application/json"
|
||||
if req.Format == "yaml" {
|
||||
contentType = "text/x-yaml"
|
||||
}
|
||||
|
||||
ctx.Data(http.StatusOK, contentType, buf.Bytes())
|
||||
}
|
||||
|
||||
// swagger:parameters saveConfigRequest
|
||||
type saveConfigRequest struct {
|
||||
// output format, one of yaml|json, default is yaml.
|
||||
// in: query
|
||||
Format string `form:"format" json:"format"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response saveConfigResponse
|
||||
type saveConfigResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func saveConfig(ctx *gin.Context) {
|
||||
// swagger:route POST /config ConfigManagement saveConfigRequest
|
||||
//
|
||||
// Save current config to file (gost.yaml or gost.json).
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: saveConfigResponse
|
||||
|
||||
var req saveConfigRequest
|
||||
ctx.ShouldBindQuery(&req)
|
||||
|
||||
file := "gost.yaml"
|
||||
switch req.Format {
|
||||
case "json":
|
||||
file = "gost.json"
|
||||
default:
|
||||
req.Format = "yaml"
|
||||
}
|
||||
|
||||
f, err := os.Create(file)
|
||||
if err != nil {
|
||||
writeError(ctx, &Error{
|
||||
statusCode: http.StatusInternalServerError,
|
||||
Code: 40005,
|
||||
Msg: fmt.Sprintf("create file: %s", err.Error()),
|
||||
})
|
||||
return
|
||||
}
|
||||
defer f.Close()
|
||||
|
||||
if err := config.Global().Write(f, req.Format); err != nil {
|
||||
writeError(ctx, &Error{
|
||||
statusCode: http.StatusInternalServerError,
|
||||
Code: 40006,
|
||||
Msg: fmt.Sprintf("write: %s", err.Error()),
|
||||
})
|
||||
return
|
||||
}
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,166 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createAdmissionRequest
|
||||
type createAdmissionRequest struct {
|
||||
// in: body
|
||||
Data config.AdmissionConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createAdmissionResponse
|
||||
type createAdmissionResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createAdmission(ctx *gin.Context) {
|
||||
// swagger:route POST /config/admissions ConfigManagement createAdmissionRequest
|
||||
//
|
||||
// Create a new admission, the name of admission must be unique in admission list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createAdmissionResponse
|
||||
|
||||
var req createAdmissionRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v := parsing.ParseAdmission(&req.Data)
|
||||
|
||||
if err := registry.Admission().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Admissions = append(cfg.Admissions, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateAdmissionRequest
|
||||
type updateAdmissionRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Admission string `uri:"admission" json:"admission"`
|
||||
// in: body
|
||||
Data config.AdmissionConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateAdmissionResponse
|
||||
type updateAdmissionResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateAdmission(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/admissions/{admission} ConfigManagement updateAdmissionRequest
|
||||
//
|
||||
// Update admission by name, the admission must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateAdmissionResponse
|
||||
|
||||
var req updateAdmissionRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Admission().IsRegistered(req.Admission) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Admission
|
||||
|
||||
v := parsing.ParseAdmission(&req.Data)
|
||||
|
||||
registry.Admission().Unregister(req.Admission)
|
||||
|
||||
if err := registry.Admission().Register(req.Admission, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Admissions {
|
||||
if cfg.Admissions[i].Name == req.Admission {
|
||||
cfg.Admissions[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteAdmissionRequest
|
||||
type deleteAdmissionRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Admission string `uri:"admission" json:"admission"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteAdmissionResponse
|
||||
type deleteAdmissionResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteAdmission(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/admissions/{admission} ConfigManagement deleteAdmissionRequest
|
||||
//
|
||||
// Delete admission by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteAdmissionResponse
|
||||
|
||||
var req deleteAdmissionRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Admission().IsRegistered(req.Admission) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Admission().Unregister(req.Admission)
|
||||
|
||||
cfg := config.Global()
|
||||
admissiones := cfg.Admissions
|
||||
cfg.Admissions = nil
|
||||
for _, s := range admissiones {
|
||||
if s.Name == req.Admission {
|
||||
continue
|
||||
}
|
||||
cfg.Admissions = append(cfg.Admissions, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,164 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createAutherRequest
|
||||
type createAutherRequest struct {
|
||||
// in: body
|
||||
Data config.AutherConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createAutherResponse
|
||||
type createAutherResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createAuther(ctx *gin.Context) {
|
||||
// swagger:route POST /config/authers ConfigManagement createAutherRequest
|
||||
//
|
||||
// Create a new auther, the name of the auther must be unique in auther list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createAutherResponse
|
||||
|
||||
var req createAutherRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v := parsing.ParseAuther(&req.Data)
|
||||
if err := registry.Auther().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Authers = append(cfg.Authers, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateAutherRequest
|
||||
type updateAutherRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Auther string `uri:"auther" json:"auther"`
|
||||
// in: body
|
||||
Data config.AutherConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateAutherResponse
|
||||
type updateAutherResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateAuther(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/authers/{auther} ConfigManagement updateAutherRequest
|
||||
//
|
||||
// Update auther by name, the auther must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateAutherResponse
|
||||
|
||||
var req updateAutherRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Auther().IsRegistered(req.Auther) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Auther
|
||||
|
||||
v := parsing.ParseAuther(&req.Data)
|
||||
registry.Auther().Unregister(req.Auther)
|
||||
|
||||
if err := registry.Auther().Register(req.Auther, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Authers {
|
||||
if cfg.Authers[i].Name == req.Auther {
|
||||
cfg.Authers[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteAutherRequest
|
||||
type deleteAutherRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Auther string `uri:"auther" json:"auther"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteAutherResponse
|
||||
type deleteAutherResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteAuther(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/authers/{auther} ConfigManagement deleteAutherRequest
|
||||
//
|
||||
// Delete auther by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteAutherResponse
|
||||
|
||||
var req deleteAutherRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Auther().IsRegistered(req.Auther) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Auther().Unregister(req.Auther)
|
||||
|
||||
cfg := config.Global()
|
||||
authers := cfg.Authers
|
||||
cfg.Authers = nil
|
||||
for _, s := range authers {
|
||||
if s.Name == req.Auther {
|
||||
continue
|
||||
}
|
||||
cfg.Authers = append(cfg.Authers, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,166 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createBypassRequest
|
||||
type createBypassRequest struct {
|
||||
// in: body
|
||||
Data config.BypassConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createBypassResponse
|
||||
type createBypassResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createBypass(ctx *gin.Context) {
|
||||
// swagger:route POST /config/bypasses ConfigManagement createBypassRequest
|
||||
//
|
||||
// Create a new bypass, the name of bypass must be unique in bypass list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createBypassResponse
|
||||
|
||||
var req createBypassRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v := parsing.ParseBypass(&req.Data)
|
||||
|
||||
if err := registry.Bypass().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Bypasses = append(cfg.Bypasses, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateBypassRequest
|
||||
type updateBypassRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Bypass string `uri:"bypass" json:"bypass"`
|
||||
// in: body
|
||||
Data config.BypassConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateBypassResponse
|
||||
type updateBypassResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateBypass(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/bypasses/{bypass} ConfigManagement updateBypassRequest
|
||||
//
|
||||
// Update bypass by name, the bypass must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateBypassResponse
|
||||
|
||||
var req updateBypassRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Bypass().IsRegistered(req.Bypass) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Bypass
|
||||
|
||||
v := parsing.ParseBypass(&req.Data)
|
||||
|
||||
registry.Bypass().Unregister(req.Bypass)
|
||||
|
||||
if err := registry.Bypass().Register(req.Bypass, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Bypasses {
|
||||
if cfg.Bypasses[i].Name == req.Bypass {
|
||||
cfg.Bypasses[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteBypassRequest
|
||||
type deleteBypassRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Bypass string `uri:"bypass" json:"bypass"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteBypassResponse
|
||||
type deleteBypassResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteBypass(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/bypasses/{bypass} ConfigManagement deleteBypassRequest
|
||||
//
|
||||
// Delete bypass by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteBypassResponse
|
||||
|
||||
var req deleteBypassRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Bypass().IsRegistered(req.Bypass) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Bypass().Unregister(req.Bypass)
|
||||
|
||||
cfg := config.Global()
|
||||
bypasses := cfg.Bypasses
|
||||
cfg.Bypasses = nil
|
||||
for _, s := range bypasses {
|
||||
if s.Name == req.Bypass {
|
||||
continue
|
||||
}
|
||||
cfg.Bypasses = append(cfg.Bypasses, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,175 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createChainRequest
|
||||
type createChainRequest struct {
|
||||
// in: body
|
||||
Data config.ChainConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createChainResponse
|
||||
type createChainResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createChain(ctx *gin.Context) {
|
||||
// swagger:route POST /config/chains ConfigManagement createChainRequest
|
||||
//
|
||||
// Create a new chain, the name of chain must be unique in chain list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createChainResponse
|
||||
|
||||
var req createChainRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v, err := parsing.ParseChain(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
if err := registry.Chain().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Chains = append(cfg.Chains, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateChainRequest
|
||||
type updateChainRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
// chain name
|
||||
Chain string `uri:"chain" json:"chain"`
|
||||
// in: body
|
||||
Data config.ChainConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateChainResponse
|
||||
type updateChainResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateChain(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/chains/{chain} ConfigManagement updateChainRequest
|
||||
//
|
||||
// Update chain by name, the chain must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateChainResponse
|
||||
|
||||
var req updateChainRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Chain().IsRegistered(req.Chain) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Chain
|
||||
|
||||
v, err := parsing.ParseChain(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
registry.Chain().Unregister(req.Chain)
|
||||
|
||||
if err := registry.Chain().Register(req.Chain, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Chains {
|
||||
if cfg.Chains[i].Name == req.Chain {
|
||||
cfg.Chains[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteChainRequest
|
||||
type deleteChainRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Chain string `uri:"chain" json:"chain"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteChainResponse
|
||||
type deleteChainResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteChain(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/chains/{chain} ConfigManagement deleteChainRequest
|
||||
//
|
||||
// Delete chain by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteChainResponse
|
||||
|
||||
var req deleteChainRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Chain().IsRegistered(req.Chain) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Chain().Unregister(req.Chain)
|
||||
|
||||
cfg := config.Global()
|
||||
chains := cfg.Chains
|
||||
cfg.Chains = nil
|
||||
for _, s := range chains {
|
||||
if s.Name == req.Chain {
|
||||
continue
|
||||
}
|
||||
cfg.Chains = append(cfg.Chains, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,166 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createHostsRequest
|
||||
type createHostsRequest struct {
|
||||
// in: body
|
||||
Data config.HostsConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createHostsResponse
|
||||
type createHostsesponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createHosts(ctx *gin.Context) {
|
||||
// swagger:route POST /config/hosts ConfigManagement createHostsRequest
|
||||
//
|
||||
// Create a new hosts, the name of the hosts must be unique in hosts list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createHostsResponse
|
||||
|
||||
var req createHostsRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v := parsing.ParseHosts(&req.Data)
|
||||
|
||||
if err := registry.Hosts().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Hosts = append(cfg.Hosts, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateHostsRequest
|
||||
type updateHostsRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Hosts string `uri:"hosts" json:"hosts"`
|
||||
// in: body
|
||||
Data config.HostsConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateHostsResponse
|
||||
type updateHostsResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateHosts(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/hosts/{hosts} ConfigManagement updateHostsRequest
|
||||
//
|
||||
// Update hosts by name, the hosts must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateHostsResponse
|
||||
|
||||
var req updateHostsRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Hosts().IsRegistered(req.Hosts) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Hosts
|
||||
|
||||
v := parsing.ParseHosts(&req.Data)
|
||||
|
||||
registry.Hosts().Unregister(req.Hosts)
|
||||
|
||||
if err := registry.Hosts().Register(req.Hosts, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Hosts {
|
||||
if cfg.Hosts[i].Name == req.Hosts {
|
||||
cfg.Hosts[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteHostsRequest
|
||||
type deleteHostsRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Hosts string `uri:"hosts" json:"hosts"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteHostsResponse
|
||||
type deleteHostsResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteHosts(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/hosts/{hosts} ConfigManagement deleteHostsRequest
|
||||
//
|
||||
// Delete hosts by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteHostsResponse
|
||||
|
||||
var req deleteHostsRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Hosts().IsRegistered(req.Hosts) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Hosts().Unregister(req.Hosts)
|
||||
|
||||
cfg := config.Global()
|
||||
hosts := cfg.Hosts
|
||||
cfg.Hosts = nil
|
||||
for _, s := range hosts {
|
||||
if s.Name == req.Hosts {
|
||||
continue
|
||||
}
|
||||
cfg.Hosts = append(cfg.Hosts, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,174 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createResolverRequest
|
||||
type createResolverRequest struct {
|
||||
// in: body
|
||||
Data config.ResolverConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createResolverResponse
|
||||
type createResolverResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createResolver(ctx *gin.Context) {
|
||||
// swagger:route POST /config/resolvers ConfigManagement createResolverRequest
|
||||
//
|
||||
// Create a new resolver, the name of the resolver must be unique in resolver list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createResolverResponse
|
||||
|
||||
var req createResolverRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
v, err := parsing.ParseResolver(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
if err := registry.Resolver().Register(req.Data.Name, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Resolvers = append(cfg.Resolvers, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateResolverRequest
|
||||
type updateResolverRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Resolver string `uri:"resolver" json:"resolver"`
|
||||
// in: body
|
||||
Data config.ResolverConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateResolverResponse
|
||||
type updateResolverResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateResolver(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/resolvers/{resolver} ConfigManagement updateResolverRequest
|
||||
//
|
||||
// Update resolver by name, the resolver must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateResolverResponse
|
||||
|
||||
var req updateResolverRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if !registry.Resolver().IsRegistered(req.Resolver) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
req.Data.Name = req.Resolver
|
||||
|
||||
v, err := parsing.ParseResolver(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
registry.Resolver().Unregister(req.Resolver)
|
||||
|
||||
if err := registry.Resolver().Register(req.Resolver, v); err != nil {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Resolvers {
|
||||
if cfg.Resolvers[i].Name == req.Resolver {
|
||||
cfg.Resolvers[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteResolverRequest
|
||||
type deleteResolverRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Resolver string `uri:"resolver" json:"resolver"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteResolverResponse
|
||||
type deleteResolverResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteResolver(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/resolvers/{resolver} ConfigManagement deleteResolverRequest
|
||||
//
|
||||
// Delete resolver by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteResolverResponse
|
||||
|
||||
var req deleteResolverRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
if !registry.Resolver().IsRegistered(req.Resolver) {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
registry.Resolver().Unregister(req.Resolver)
|
||||
|
||||
cfg := config.Global()
|
||||
resolvers := cfg.Resolvers
|
||||
cfg.Resolvers = nil
|
||||
for _, s := range resolvers {
|
||||
if s.Name == req.Resolver {
|
||||
continue
|
||||
}
|
||||
cfg.Resolvers = append(cfg.Resolvers, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,190 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/config/parsing"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
// swagger:parameters createServiceRequest
|
||||
type createServiceRequest struct {
|
||||
// in: body
|
||||
Data config.ServiceConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response createServiceResponse
|
||||
type createServiceResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func createService(ctx *gin.Context) {
|
||||
// swagger:route POST /config/services ConfigManagement createServiceRequest
|
||||
//
|
||||
// Create a new service, the name of the service must be unique in service list.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: createServiceResponse
|
||||
|
||||
var req createServiceRequest
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
if req.Data.Name == "" {
|
||||
writeError(ctx, ErrInvalid)
|
||||
return
|
||||
}
|
||||
|
||||
if registry.Service().IsRegistered(req.Data.Name) {
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
svc, err := parsing.ParseService(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
if err := registry.Service().Register(req.Data.Name, svc); err != nil {
|
||||
svc.Close()
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
go svc.Serve()
|
||||
|
||||
cfg := config.Global()
|
||||
cfg.Services = append(cfg.Services, &req.Data)
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters updateServiceRequest
|
||||
type updateServiceRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Service string `uri:"service" json:"service"`
|
||||
// in: body
|
||||
Data config.ServiceConfig `json:"data"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response updateServiceResponse
|
||||
type updateServiceResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func updateService(ctx *gin.Context) {
|
||||
// swagger:route PUT /config/services/{service} ConfigManagement updateServiceRequest
|
||||
//
|
||||
// Update service by name, the service must already exist.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: updateServiceResponse
|
||||
|
||||
var req updateServiceRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
ctx.ShouldBindJSON(&req.Data)
|
||||
|
||||
old := registry.Service().Get(req.Service)
|
||||
if old == nil {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
old.Close()
|
||||
|
||||
req.Data.Name = req.Service
|
||||
|
||||
svc, err := parsing.ParseService(&req.Data)
|
||||
if err != nil {
|
||||
writeError(ctx, ErrCreate)
|
||||
return
|
||||
}
|
||||
|
||||
registry.Service().Unregister(req.Service)
|
||||
|
||||
if err := registry.Service().Register(req.Service, svc); err != nil {
|
||||
svc.Close()
|
||||
writeError(ctx, ErrDup)
|
||||
return
|
||||
}
|
||||
|
||||
go svc.Serve()
|
||||
|
||||
cfg := config.Global()
|
||||
for i := range cfg.Services {
|
||||
if cfg.Services[i].Name == req.Service {
|
||||
cfg.Services[i] = &req.Data
|
||||
break
|
||||
}
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
|
||||
// swagger:parameters deleteServiceRequest
|
||||
type deleteServiceRequest struct {
|
||||
// in: path
|
||||
// required: true
|
||||
Service string `uri:"service" json:"service"`
|
||||
}
|
||||
|
||||
// successful operation.
|
||||
// swagger:response deleteServiceResponse
|
||||
type deleteServiceResponse struct {
|
||||
Data Response
|
||||
}
|
||||
|
||||
func deleteService(ctx *gin.Context) {
|
||||
// swagger:route DELETE /config/services/{service} ConfigManagement deleteServiceRequest
|
||||
//
|
||||
// Delete service by name.
|
||||
//
|
||||
// Security:
|
||||
// basicAuth: []
|
||||
//
|
||||
// Responses:
|
||||
// 200: deleteServiceResponse
|
||||
|
||||
var req deleteServiceRequest
|
||||
ctx.ShouldBindUri(&req)
|
||||
|
||||
svc := registry.Service().Get(req.Service)
|
||||
if svc == nil {
|
||||
writeError(ctx, ErrNotFound)
|
||||
return
|
||||
}
|
||||
|
||||
registry.Service().Unregister(req.Service)
|
||||
svc.Close()
|
||||
|
||||
cfg := config.Global()
|
||||
services := cfg.Services
|
||||
cfg.Services = nil
|
||||
for _, s := range services {
|
||||
if s.Name == req.Service {
|
||||
continue
|
||||
}
|
||||
cfg.Services = append(cfg.Services, s)
|
||||
}
|
||||
config.SetGlobal(cfg)
|
||||
|
||||
ctx.JSON(http.StatusOK, Response{
|
||||
Msg: "OK",
|
||||
})
|
||||
}
|
||||
@@ -1,18 +0,0 @@
|
||||
// Documentation of Web API.
|
||||
//
|
||||
// Schemes: https, http
|
||||
// BasePath: /
|
||||
// Version: 1.0.0
|
||||
//
|
||||
// Consumes:
|
||||
// - application/json
|
||||
//
|
||||
// Produces:
|
||||
// - application/json
|
||||
//
|
||||
// SecurityDefinitions:
|
||||
// basicAuth:
|
||||
// type: basic
|
||||
//
|
||||
// swagger:meta
|
||||
package api
|
||||
@@ -1,45 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
)
|
||||
|
||||
var (
|
||||
ErrInvalid = &Error{statusCode: http.StatusBadRequest, Code: 40001, Msg: "object invalid"}
|
||||
ErrDup = &Error{statusCode: http.StatusBadRequest, Code: 40002, Msg: "object duplicated"}
|
||||
ErrCreate = &Error{statusCode: http.StatusConflict, Code: 40003, Msg: "object creation failed"}
|
||||
ErrNotFound = &Error{statusCode: http.StatusBadRequest, Code: 40004, Msg: "object not found"}
|
||||
ErrSave = &Error{statusCode: http.StatusInternalServerError, Code: 40005, Msg: "save config failed"}
|
||||
)
|
||||
|
||||
// Error is an api error.
|
||||
type Error struct {
|
||||
statusCode int
|
||||
Code int `json:"code"`
|
||||
Msg string `json:"msg"`
|
||||
}
|
||||
|
||||
func (e *Error) Error() string {
|
||||
b, _ := json.Marshal(e)
|
||||
return string(b)
|
||||
}
|
||||
|
||||
func writeError(c *gin.Context, err error) {
|
||||
// c.Set(HTTPResponseTag, err)
|
||||
c.JSON(getStatusCode(err), err)
|
||||
}
|
||||
|
||||
func getStatusCode(err error) int {
|
||||
if err == nil {
|
||||
return http.StatusOK
|
||||
}
|
||||
if e, ok := err.(*Error); ok {
|
||||
if e.statusCode >= http.StatusOK && e.statusCode < 600 {
|
||||
return e.statusCode
|
||||
}
|
||||
}
|
||||
return http.StatusInternalServerError
|
||||
}
|
||||
@@ -1,42 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
"time"
|
||||
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/auth"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
func mwLogger() gin.HandlerFunc {
|
||||
return func(ctx *gin.Context) {
|
||||
// start time
|
||||
startTime := time.Now()
|
||||
// Processing request
|
||||
ctx.Next()
|
||||
duration := time.Since(startTime)
|
||||
|
||||
logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "api",
|
||||
"method": ctx.Request.Method,
|
||||
"uri": ctx.Request.RequestURI,
|
||||
"code": ctx.Writer.Status(),
|
||||
"client": ctx.ClientIP(),
|
||||
"duration": duration,
|
||||
}).Infof("| %3d | %13v | %15s | %-7s %s",
|
||||
ctx.Writer.Status(), duration, ctx.ClientIP(), ctx.Request.Method, ctx.Request.RequestURI)
|
||||
}
|
||||
}
|
||||
|
||||
func mwBasicAuth(auther auth.Authenticator) gin.HandlerFunc {
|
||||
return func(c *gin.Context) {
|
||||
if auther == nil {
|
||||
return
|
||||
}
|
||||
u, p, _ := c.Request.BasicAuth()
|
||||
if !auther.Authenticate(u, p) {
|
||||
c.AbortWithStatus(http.StatusUnauthorized)
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -1,131 +0,0 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net"
|
||||
"net/http"
|
||||
|
||||
"github.com/gin-contrib/cors"
|
||||
"github.com/gin-gonic/gin"
|
||||
"github.com/go-gost/gost/pkg/auth"
|
||||
)
|
||||
|
||||
type options struct {
|
||||
accessLog bool
|
||||
pathPrefix string
|
||||
auther auth.Authenticator
|
||||
}
|
||||
|
||||
type Option func(*options)
|
||||
|
||||
func PathPrefixOption(pathPrefix string) Option {
|
||||
return func(o *options) {
|
||||
o.pathPrefix = pathPrefix
|
||||
}
|
||||
}
|
||||
|
||||
func AccessLogOption(enable bool) Option {
|
||||
return func(o *options) {
|
||||
o.accessLog = enable
|
||||
}
|
||||
}
|
||||
|
||||
func AutherOption(auther auth.Authenticator) Option {
|
||||
return func(o *options) {
|
||||
o.auther = auther
|
||||
}
|
||||
}
|
||||
|
||||
type Server struct {
|
||||
s *http.Server
|
||||
ln net.Listener
|
||||
}
|
||||
|
||||
func NewServer(addr string, opts ...Option) (*Server, error) {
|
||||
ln, err := net.Listen("tcp", addr)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
var options options
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
gin.SetMode(gin.ReleaseMode)
|
||||
|
||||
r := gin.New()
|
||||
r.Use(
|
||||
cors.New((cors.Config{
|
||||
AllowAllOrigins: true,
|
||||
AllowMethods: []string{"GET", "POST", "PUT", "DELETE", "OPTIONS"},
|
||||
AllowHeaders: []string{"*"},
|
||||
})),
|
||||
gin.Recovery(),
|
||||
)
|
||||
if options.accessLog {
|
||||
r.Use(mwLogger())
|
||||
}
|
||||
|
||||
router := r.Group("")
|
||||
if options.pathPrefix != "" {
|
||||
router = router.Group(options.pathPrefix)
|
||||
}
|
||||
|
||||
router.StaticFS("/docs", http.FS(swaggerDoc))
|
||||
|
||||
config := router.Group("/config")
|
||||
config.Use(mwBasicAuth(options.auther))
|
||||
registerConfig(config)
|
||||
|
||||
return &Server{
|
||||
s: &http.Server{
|
||||
Handler: r,
|
||||
},
|
||||
ln: ln,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (s *Server) Serve() error {
|
||||
return s.s.Serve(s.ln)
|
||||
}
|
||||
|
||||
func (s *Server) Addr() net.Addr {
|
||||
return s.ln.Addr()
|
||||
}
|
||||
|
||||
func (s *Server) Close() error {
|
||||
return s.s.Close()
|
||||
}
|
||||
|
||||
func registerConfig(config *gin.RouterGroup) {
|
||||
config.GET("", getConfig)
|
||||
config.POST("", saveConfig)
|
||||
|
||||
config.POST("/services", createService)
|
||||
config.PUT("/services/:service", updateService)
|
||||
config.DELETE("/services/:service", deleteService)
|
||||
|
||||
config.POST("/chains", createChain)
|
||||
config.PUT("/chains/:chain", updateChain)
|
||||
config.DELETE("/chains/:chain", deleteChain)
|
||||
|
||||
config.POST("/authers", createAuther)
|
||||
config.PUT("/authers/:auther", updateAuther)
|
||||
config.DELETE("/authers/:auther", deleteAuther)
|
||||
|
||||
config.POST("/admissions", createAdmission)
|
||||
config.PUT("/admissions/:admission", updateAdmission)
|
||||
config.DELETE("/admissions/:admission", deleteAdmission)
|
||||
|
||||
config.POST("/bypasses", createBypass)
|
||||
config.PUT("/bypasses/:bypass", updateBypass)
|
||||
config.DELETE("/bypasses/:bypass", deleteBypass)
|
||||
|
||||
config.POST("/resolvers", createResolver)
|
||||
config.PUT("/resolvers/:resolver", updateResolver)
|
||||
config.DELETE("/resolvers/:resolver", deleteResolver)
|
||||
|
||||
config.POST("/hosts", createHosts)
|
||||
config.PUT("/hosts/:hosts", updateHosts)
|
||||
config.DELETE("/hosts/:hosts", deleteHosts)
|
||||
}
|
||||
File diff suppressed because it is too large
Load Diff
@@ -1,28 +0,0 @@
|
||||
package auth
|
||||
|
||||
// Authenticator is an interface for user authentication.
|
||||
type Authenticator interface {
|
||||
Authenticate(user, password string) bool
|
||||
}
|
||||
|
||||
// LocalAuthenticator is an Authenticator that authenticates client by local key-value pairs.
|
||||
type MapAuthenticator struct {
|
||||
kvs map[string]string
|
||||
}
|
||||
|
||||
// NewMapAuthenticator creates an Authenticator that authenticates client by local infos.
|
||||
func NewMapAuthenticator(kvs map[string]string) Authenticator {
|
||||
return &MapAuthenticator{
|
||||
kvs: kvs,
|
||||
}
|
||||
}
|
||||
|
||||
// Authenticate checks the validity of the provided user-password pair.
|
||||
func (au *MapAuthenticator) Authenticate(user, password string) bool {
|
||||
if au == nil || len(au.kvs) == 0 {
|
||||
return true
|
||||
}
|
||||
|
||||
v, ok := au.kvs[user]
|
||||
return ok && (v == "" || password == v)
|
||||
}
|
||||
@@ -1,90 +0,0 @@
|
||||
package bypass
|
||||
|
||||
import (
|
||||
"net"
|
||||
"strconv"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/matcher"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
// Bypass is a filter of address (IP or domain).
|
||||
type Bypass interface {
|
||||
// Contains reports whether the bypass includes addr.
|
||||
Contains(addr string) bool
|
||||
}
|
||||
|
||||
type options struct {
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
type Option func(opts *options)
|
||||
|
||||
func LoggerOption(logger logger.Logger) Option {
|
||||
return func(opts *options) {
|
||||
opts.logger = logger
|
||||
}
|
||||
}
|
||||
|
||||
type bypass struct {
|
||||
matchers []matcher.Matcher
|
||||
reversed bool
|
||||
options options
|
||||
}
|
||||
|
||||
// NewBypass creates and initializes a new Bypass using matchers as its match rules.
|
||||
// The rules will be reversed if the reversed is true.
|
||||
func NewBypass(reversed bool, matchers []matcher.Matcher, opts ...Option) Bypass {
|
||||
options := options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
return &bypass{
|
||||
matchers: matchers,
|
||||
reversed: reversed,
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
// NewBypassPatterns creates and initializes a new Bypass using matcher patterns as its match rules.
|
||||
// The rules will be reversed if the reverse is true.
|
||||
func NewBypassPatterns(reversed bool, patterns []string, opts ...Option) Bypass {
|
||||
var matchers []matcher.Matcher
|
||||
for _, pattern := range patterns {
|
||||
if m := matcher.NewMatcher(pattern); m != nil {
|
||||
matchers = append(matchers, m)
|
||||
}
|
||||
}
|
||||
return NewBypass(reversed, matchers, opts...)
|
||||
}
|
||||
|
||||
func (bp *bypass) Contains(addr string) bool {
|
||||
if addr == "" || bp == nil || len(bp.matchers) == 0 {
|
||||
return false
|
||||
}
|
||||
|
||||
// try to strip the port
|
||||
if host, port, _ := net.SplitHostPort(addr); host != "" && port != "" {
|
||||
if p, _ := strconv.Atoi(port); p > 0 { // port is valid
|
||||
addr = host
|
||||
}
|
||||
}
|
||||
|
||||
var matched bool
|
||||
for _, matcher := range bp.matchers {
|
||||
if matcher == nil {
|
||||
continue
|
||||
}
|
||||
if matcher.Match(addr) {
|
||||
matched = true
|
||||
break
|
||||
}
|
||||
}
|
||||
|
||||
b := !bp.reversed && matched ||
|
||||
bp.reversed && !matched
|
||||
if b {
|
||||
bp.options.logger.Debugf("bypass: %s", addr)
|
||||
}
|
||||
return b
|
||||
}
|
||||
@@ -1,41 +0,0 @@
|
||||
package chain
|
||||
|
||||
type Chainer interface {
|
||||
Route(network, address string) *Route
|
||||
}
|
||||
|
||||
type Chain struct {
|
||||
groups []*NodeGroup
|
||||
}
|
||||
|
||||
func (c *Chain) AddNodeGroup(group *NodeGroup) {
|
||||
c.groups = append(c.groups, group)
|
||||
}
|
||||
|
||||
func (c *Chain) Route(network, address string) (r *Route) {
|
||||
if c == nil || len(c.groups) == 0 {
|
||||
return
|
||||
}
|
||||
|
||||
r = &Route{}
|
||||
for _, group := range c.groups {
|
||||
node := group.Next()
|
||||
if node == nil {
|
||||
return
|
||||
}
|
||||
if node.Bypass != nil && node.Bypass.Contains(address) {
|
||||
break
|
||||
}
|
||||
|
||||
if node.Transport.Multiplex() {
|
||||
tr := node.Transport.Copy().
|
||||
WithRoute(r)
|
||||
node = node.Copy()
|
||||
node.Transport = tr
|
||||
r = &Route{}
|
||||
}
|
||||
|
||||
r.addNode(node)
|
||||
}
|
||||
return r
|
||||
}
|
||||
@@ -1,97 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"sync/atomic"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/bypass"
|
||||
"github.com/go-gost/gost/pkg/hosts"
|
||||
"github.com/go-gost/gost/pkg/resolver"
|
||||
)
|
||||
|
||||
type Node struct {
|
||||
Name string
|
||||
Addr string
|
||||
Transport *Transport
|
||||
Bypass bypass.Bypass
|
||||
Resolver resolver.Resolver
|
||||
Hosts hosts.HostMapper
|
||||
Marker *FailMarker
|
||||
}
|
||||
|
||||
func (node *Node) Copy() *Node {
|
||||
n := &Node{}
|
||||
*n = *node
|
||||
return n
|
||||
}
|
||||
|
||||
type NodeGroup struct {
|
||||
nodes []*Node
|
||||
selector Selector
|
||||
}
|
||||
|
||||
func NewNodeGroup(nodes ...*Node) *NodeGroup {
|
||||
return &NodeGroup{
|
||||
nodes: nodes,
|
||||
}
|
||||
}
|
||||
|
||||
func (g *NodeGroup) AddNode(node *Node) {
|
||||
g.nodes = append(g.nodes, node)
|
||||
}
|
||||
|
||||
func (g *NodeGroup) WithSelector(selector Selector) *NodeGroup {
|
||||
g.selector = selector
|
||||
return g
|
||||
}
|
||||
|
||||
func (g *NodeGroup) Next() *Node {
|
||||
if g == nil || len(g.nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
|
||||
s := g.selector
|
||||
if s == nil {
|
||||
s = DefaultSelector
|
||||
}
|
||||
|
||||
return s.Select(g.nodes...)
|
||||
}
|
||||
|
||||
type FailMarker struct {
|
||||
failTime int64
|
||||
failCount int64
|
||||
}
|
||||
|
||||
func (m *FailMarker) FailTime() int64 {
|
||||
if m == nil {
|
||||
return 0
|
||||
}
|
||||
|
||||
return atomic.LoadInt64(&m.failTime)
|
||||
}
|
||||
|
||||
func (m *FailMarker) FailCount() int64 {
|
||||
if m == nil {
|
||||
return 0
|
||||
}
|
||||
|
||||
return atomic.LoadInt64(&m.failCount)
|
||||
}
|
||||
|
||||
func (m *FailMarker) Mark() {
|
||||
if m == nil {
|
||||
return
|
||||
}
|
||||
|
||||
atomic.AddInt64(&m.failCount, 1)
|
||||
atomic.StoreInt64(&m.failTime, time.Now().Unix())
|
||||
}
|
||||
|
||||
func (m *FailMarker) Reset() {
|
||||
if m == nil {
|
||||
return
|
||||
}
|
||||
|
||||
atomic.StoreInt64(&m.failCount, 0)
|
||||
}
|
||||
@@ -1,47 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/hosts"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/resolver"
|
||||
)
|
||||
|
||||
func resolve(ctx context.Context, network, addr string, r resolver.Resolver, hosts hosts.HostMapper, log logger.Logger) (string, error) {
|
||||
if addr == "" {
|
||||
return addr, nil
|
||||
}
|
||||
|
||||
host, port, err := net.SplitHostPort(addr)
|
||||
if err != nil {
|
||||
return "", err
|
||||
}
|
||||
if host == "" {
|
||||
return addr, nil
|
||||
}
|
||||
|
||||
if hosts != nil {
|
||||
if ips, _ := hosts.Lookup(network, host); len(ips) > 0 {
|
||||
log.Debugf("hit host mapper: %s -> %s", host, ips)
|
||||
return net.JoinHostPort(ips[0].String(), port), nil
|
||||
}
|
||||
}
|
||||
|
||||
if r != nil {
|
||||
ips, err := r.Resolve(ctx, network, host)
|
||||
if err != nil {
|
||||
if err == resolver.ErrInvalid {
|
||||
return addr, nil
|
||||
}
|
||||
log.Error(err)
|
||||
}
|
||||
if len(ips) == 0 {
|
||||
return "", fmt.Errorf("resolver: domain %s does not exists", host)
|
||||
}
|
||||
return net.JoinHostPort(ips[0].String(), port), nil
|
||||
}
|
||||
return addr, nil
|
||||
}
|
||||
@@ -1,196 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"context"
|
||||
"errors"
|
||||
"fmt"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/udp"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
var (
|
||||
ErrEmptyRoute = errors.New("empty route")
|
||||
)
|
||||
|
||||
type Route struct {
|
||||
nodes []*Node
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func (r *Route) addNode(node *Node) {
|
||||
r.nodes = append(r.nodes, node)
|
||||
}
|
||||
|
||||
func (r *Route) Dial(ctx context.Context, network, address string) (net.Conn, error) {
|
||||
if r.Len() == 0 {
|
||||
return r.dialDirect(ctx, network, address)
|
||||
}
|
||||
|
||||
conn, err := r.connect(ctx)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cc, err := r.GetNode(r.Len()-1).Transport.Connect(ctx, conn, network, address)
|
||||
if err != nil {
|
||||
conn.Close()
|
||||
return nil, err
|
||||
}
|
||||
return cc, nil
|
||||
}
|
||||
|
||||
func (r *Route) dialDirect(ctx context.Context, network, address string) (net.Conn, error) {
|
||||
switch network {
|
||||
case "udp", "udp4", "udp6":
|
||||
if address == "" {
|
||||
return net.ListenUDP(network, nil)
|
||||
}
|
||||
default:
|
||||
}
|
||||
|
||||
d := net.Dialer{}
|
||||
return d.DialContext(ctx, network, address)
|
||||
}
|
||||
|
||||
func (r *Route) Bind(ctx context.Context, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
if r.Len() == 0 {
|
||||
return r.bindLocal(ctx, network, address, opts...)
|
||||
}
|
||||
|
||||
conn, err := r.connect(ctx)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
ln, err := r.GetNode(r.Len()-1).Transport.Bind(ctx, conn, network, address, opts...)
|
||||
if err != nil {
|
||||
conn.Close()
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return ln, nil
|
||||
}
|
||||
|
||||
func (r *Route) connect(ctx context.Context) (conn net.Conn, err error) {
|
||||
if r.Len() == 0 {
|
||||
return nil, ErrEmptyRoute
|
||||
}
|
||||
|
||||
network := "ip"
|
||||
node := r.nodes[0]
|
||||
|
||||
addr, err := resolve(ctx, network, node.Addr, node.Resolver, node.Hosts, r.logger)
|
||||
if err != nil {
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
cc, err := node.Transport.Dial(ctx, addr)
|
||||
if err != nil {
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
|
||||
cn, err := node.Transport.Handshake(ctx, cc)
|
||||
if err != nil {
|
||||
cc.Close()
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
node.Marker.Reset()
|
||||
|
||||
preNode := node
|
||||
for _, node := range r.nodes[1:] {
|
||||
addr, err = resolve(ctx, network, node.Addr, node.Resolver, node.Hosts, r.logger)
|
||||
if err != nil {
|
||||
cn.Close()
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
cc, err = preNode.Transport.Connect(ctx, cn, "tcp", addr)
|
||||
if err != nil {
|
||||
cn.Close()
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
cc, err = node.Transport.Handshake(ctx, cc)
|
||||
if err != nil {
|
||||
cn.Close()
|
||||
node.Marker.Mark()
|
||||
return
|
||||
}
|
||||
node.Marker.Reset()
|
||||
|
||||
cn = cc
|
||||
preNode = node
|
||||
}
|
||||
|
||||
conn = cn
|
||||
return
|
||||
}
|
||||
|
||||
func (r *Route) Len() int {
|
||||
if r == nil {
|
||||
return 0
|
||||
}
|
||||
return len(r.nodes)
|
||||
}
|
||||
|
||||
func (r *Route) GetNode(index int) *Node {
|
||||
if r.Len() == 0 || index < 0 || index >= len(r.nodes) {
|
||||
return nil
|
||||
}
|
||||
return r.nodes[index]
|
||||
}
|
||||
|
||||
func (r *Route) Path() (path []*Node) {
|
||||
if r == nil || len(r.nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
|
||||
for _, node := range r.nodes {
|
||||
if node.Transport != nil && node.Transport.route != nil {
|
||||
path = append(path, node.Transport.route.Path()...)
|
||||
}
|
||||
path = append(path, node)
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (r *Route) bindLocal(ctx context.Context, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
options := connector.BindOptions{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
addr, err := net.ResolveTCPAddr(network, address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return net.ListenTCP(network, addr)
|
||||
case "udp", "udp4", "udp6":
|
||||
addr, err := net.ResolveUDPAddr(network, address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
conn, err := net.ListenUDP(network, addr)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
logger := logger.Default().WithFields(map[string]interface{}{
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
ln := udp.NewListener(conn, addr,
|
||||
options.Backlog, options.UDPDataQueueSize, options.UDPDataBufferSize,
|
||||
options.UDPConnTTL, logger)
|
||||
return ln, err
|
||||
default:
|
||||
err := fmt.Errorf("network %s unsupported", network)
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
@@ -1,122 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/hosts"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/resolver"
|
||||
)
|
||||
|
||||
type Router struct {
|
||||
Retries int
|
||||
Chain Chainer
|
||||
Hosts hosts.HostMapper
|
||||
Resolver resolver.Resolver
|
||||
Logger logger.Logger
|
||||
}
|
||||
|
||||
func (r *Router) Dial(ctx context.Context, network, address string) (conn net.Conn, err error) {
|
||||
conn, err = r.dial(ctx, network, address)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
if network == "udp" || network == "udp4" || network == "udp6" {
|
||||
if _, ok := conn.(net.PacketConn); !ok {
|
||||
return &packetConn{conn}, nil
|
||||
}
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (r *Router) dial(ctx context.Context, network, address string) (conn net.Conn, err error) {
|
||||
count := r.Retries + 1
|
||||
if count <= 0 {
|
||||
count = 1
|
||||
}
|
||||
r.Logger.Debugf("dial %s/%s", address, network)
|
||||
|
||||
for i := 0; i < count; i++ {
|
||||
var route *Route
|
||||
if r.Chain != nil {
|
||||
route = r.Chain.Route(network, address)
|
||||
}
|
||||
|
||||
if r.Logger.IsLevelEnabled(logger.DebugLevel) {
|
||||
buf := bytes.Buffer{}
|
||||
for _, node := range route.Path() {
|
||||
fmt.Fprintf(&buf, "%s@%s > ", node.Name, node.Addr)
|
||||
}
|
||||
fmt.Fprintf(&buf, "%s", address)
|
||||
r.Logger.Debugf("route(retry=%d) %s", i, buf.String())
|
||||
}
|
||||
|
||||
address, err = resolve(ctx, "ip", address, r.Resolver, r.Hosts, r.Logger)
|
||||
if err != nil {
|
||||
r.Logger.Error(err)
|
||||
break
|
||||
}
|
||||
|
||||
if route != nil {
|
||||
route.logger = r.Logger
|
||||
}
|
||||
|
||||
conn, err = route.Dial(ctx, network, address)
|
||||
if err == nil {
|
||||
break
|
||||
}
|
||||
r.Logger.Errorf("route(retry=%d) %s", i, err)
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (r *Router) Bind(ctx context.Context, network, address string, opts ...connector.BindOption) (ln net.Listener, err error) {
|
||||
count := r.Retries + 1
|
||||
if count <= 0 {
|
||||
count = 1
|
||||
}
|
||||
r.Logger.Debugf("bind on %s/%s", address, network)
|
||||
|
||||
for i := 0; i < count; i++ {
|
||||
var route *Route
|
||||
if r.Chain != nil {
|
||||
route = r.Chain.Route(network, address)
|
||||
}
|
||||
|
||||
if r.Logger.IsLevelEnabled(logger.DebugLevel) {
|
||||
buf := bytes.Buffer{}
|
||||
for _, node := range route.Path() {
|
||||
fmt.Fprintf(&buf, "%s@%s > ", node.Name, node.Addr)
|
||||
}
|
||||
fmt.Fprintf(&buf, "%s", address)
|
||||
r.Logger.Debugf("route(retry=%d) %s", i, buf.String())
|
||||
}
|
||||
|
||||
ln, err = route.Bind(ctx, network, address, opts...)
|
||||
if err == nil {
|
||||
break
|
||||
}
|
||||
r.Logger.Errorf("route(retry=%d) %s", i, err)
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
type packetConn struct {
|
||||
net.Conn
|
||||
}
|
||||
|
||||
func (c *packetConn) ReadFrom(b []byte) (n int, addr net.Addr, err error) {
|
||||
n, err = c.Read(b)
|
||||
addr = c.Conn.RemoteAddr()
|
||||
return
|
||||
}
|
||||
|
||||
func (c *packetConn) WriteTo(b []byte, addr net.Addr) (n int, err error) {
|
||||
return c.Write(b)
|
||||
}
|
||||
@@ -1,170 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"math/rand"
|
||||
"net"
|
||||
"strconv"
|
||||
"sync"
|
||||
"sync/atomic"
|
||||
"time"
|
||||
)
|
||||
|
||||
// default options for FailFilter
|
||||
const (
|
||||
DefaultFailTimeout = 30 * time.Second
|
||||
)
|
||||
|
||||
var (
|
||||
DefaultSelector = NewSelector(RoundRobinStrategy())
|
||||
)
|
||||
|
||||
type Selector interface {
|
||||
Select(nodes ...*Node) *Node
|
||||
}
|
||||
|
||||
type selector struct {
|
||||
strategy Strategy
|
||||
filters []Filter
|
||||
}
|
||||
|
||||
func NewSelector(strategy Strategy, filters ...Filter) Selector {
|
||||
return &selector{
|
||||
filters: filters,
|
||||
strategy: strategy,
|
||||
}
|
||||
}
|
||||
|
||||
func (s *selector) Select(nodes ...*Node) *Node {
|
||||
for _, filter := range s.filters {
|
||||
nodes = filter.Filter(nodes...)
|
||||
}
|
||||
if len(nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
return s.strategy.Apply(nodes...)
|
||||
}
|
||||
|
||||
type Strategy interface {
|
||||
Apply(nodes ...*Node) *Node
|
||||
}
|
||||
|
||||
type roundRobinStrategy struct {
|
||||
counter uint64
|
||||
}
|
||||
|
||||
// RoundRobinStrategy is a strategy for node selector.
|
||||
// The node will be selected by round-robin algorithm.
|
||||
func RoundRobinStrategy() Strategy {
|
||||
return &roundRobinStrategy{}
|
||||
}
|
||||
|
||||
func (s *roundRobinStrategy) Apply(nodes ...*Node) *Node {
|
||||
if len(nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
|
||||
n := atomic.AddUint64(&s.counter, 1) - 1
|
||||
return nodes[int(n%uint64(len(nodes)))]
|
||||
}
|
||||
|
||||
type randomStrategy struct {
|
||||
rand *rand.Rand
|
||||
mux sync.Mutex
|
||||
}
|
||||
|
||||
// RandomStrategy is a strategy for node selector.
|
||||
// The node will be selected randomly.
|
||||
func RandomStrategy() Strategy {
|
||||
return &randomStrategy{
|
||||
rand: rand.New(rand.NewSource(time.Now().UnixNano())),
|
||||
}
|
||||
}
|
||||
|
||||
func (s *randomStrategy) Apply(nodes ...*Node) *Node {
|
||||
if len(nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
|
||||
s.mux.Lock()
|
||||
defer s.mux.Unlock()
|
||||
|
||||
r := s.rand.Int()
|
||||
|
||||
return nodes[r%len(nodes)]
|
||||
}
|
||||
|
||||
type fifoStrategy struct{}
|
||||
|
||||
// FIFOStrategy is a strategy for node selector.
|
||||
// The node will be selected from first to last,
|
||||
// and will stick to the selected node until it is failed.
|
||||
func FIFOStrategy() Strategy {
|
||||
return &fifoStrategy{}
|
||||
}
|
||||
|
||||
// Apply applies the fifo strategy for the nodes.
|
||||
func (s *fifoStrategy) Apply(nodes ...*Node) *Node {
|
||||
if len(nodes) == 0 {
|
||||
return nil
|
||||
}
|
||||
return nodes[0]
|
||||
}
|
||||
|
||||
type Filter interface {
|
||||
Filter(nodes ...*Node) []*Node
|
||||
}
|
||||
|
||||
type failFilter struct {
|
||||
maxFails int
|
||||
failTimeout time.Duration
|
||||
}
|
||||
|
||||
// FailFilter filters the dead node.
|
||||
// A node is marked as dead if its failed count is greater than MaxFails.
|
||||
func FailFilter(maxFails int, timeout time.Duration) Filter {
|
||||
return &failFilter{
|
||||
maxFails: maxFails,
|
||||
failTimeout: timeout,
|
||||
}
|
||||
}
|
||||
|
||||
// Filter filters dead nodes.
|
||||
func (f *failFilter) Filter(nodes ...*Node) []*Node {
|
||||
maxFails := f.maxFails
|
||||
failTimeout := f.failTimeout
|
||||
if failTimeout == 0 {
|
||||
failTimeout = DefaultFailTimeout
|
||||
}
|
||||
|
||||
if len(nodes) <= 1 || maxFails <= 0 {
|
||||
return nodes
|
||||
}
|
||||
var nl []*Node
|
||||
for _, node := range nodes {
|
||||
if node.Marker.FailCount() < int64(maxFails) ||
|
||||
time.Since(time.Unix(node.Marker.FailTime(), 0)) >= failTimeout {
|
||||
nl = append(nl, node)
|
||||
}
|
||||
}
|
||||
return nl
|
||||
}
|
||||
|
||||
type invalidFilter struct{}
|
||||
|
||||
// InvalidFilter filters the invalid node.
|
||||
// A node is invalid if its port is invalid (negative or zero value).
|
||||
func InvalidFilter() Filter {
|
||||
return &invalidFilter{}
|
||||
}
|
||||
|
||||
// Filter filters invalid nodes.
|
||||
func (f *invalidFilter) Filter(nodes ...*Node) []*Node {
|
||||
var nl []*Node
|
||||
for _, node := range nodes {
|
||||
_, sport, _ := net.SplitHostPort(node.Addr)
|
||||
if port, _ := strconv.Atoi(sport); port > 0 {
|
||||
nl = append(nl, node)
|
||||
}
|
||||
}
|
||||
return nl
|
||||
}
|
||||
@@ -1,95 +0,0 @@
|
||||
package chain
|
||||
|
||||
import (
|
||||
"context"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/dialer"
|
||||
)
|
||||
|
||||
type Transport struct {
|
||||
addr string
|
||||
route *Route
|
||||
dialer dialer.Dialer
|
||||
connector connector.Connector
|
||||
}
|
||||
|
||||
func (tr *Transport) Copy() *Transport {
|
||||
tr2 := &Transport{}
|
||||
*tr2 = *tr
|
||||
return tr
|
||||
}
|
||||
|
||||
func (tr *Transport) WithDialer(dialer dialer.Dialer) *Transport {
|
||||
tr.dialer = dialer
|
||||
return tr
|
||||
}
|
||||
|
||||
func (tr *Transport) WithConnector(connector connector.Connector) *Transport {
|
||||
tr.connector = connector
|
||||
return tr
|
||||
}
|
||||
|
||||
func (tr *Transport) Dial(ctx context.Context, addr string) (net.Conn, error) {
|
||||
return tr.dialer.Dial(ctx, addr, tr.dialOptions()...)
|
||||
}
|
||||
|
||||
func (tr *Transport) dialOptions() []dialer.DialOption {
|
||||
opts := []dialer.DialOption{
|
||||
dialer.HostDialOption(tr.addr),
|
||||
}
|
||||
if tr.route.Len() > 0 {
|
||||
opts = append(opts,
|
||||
dialer.DialFuncDialOption(
|
||||
func(ctx context.Context, addr string) (net.Conn, error) {
|
||||
return tr.route.Dial(ctx, "tcp", addr)
|
||||
},
|
||||
),
|
||||
)
|
||||
}
|
||||
return opts
|
||||
}
|
||||
|
||||
func (tr *Transport) Handshake(ctx context.Context, conn net.Conn) (net.Conn, error) {
|
||||
var err error
|
||||
if hs, ok := tr.dialer.(dialer.Handshaker); ok {
|
||||
conn, err = hs.Handshake(ctx, conn,
|
||||
dialer.AddrHandshakeOption(tr.addr))
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
if hs, ok := tr.connector.(connector.Handshaker); ok {
|
||||
return hs.Handshake(ctx, conn)
|
||||
}
|
||||
return conn, nil
|
||||
}
|
||||
|
||||
func (tr *Transport) Connect(ctx context.Context, conn net.Conn, network, address string) (net.Conn, error) {
|
||||
return tr.connector.Connect(ctx, conn, network, address)
|
||||
}
|
||||
|
||||
func (tr *Transport) Bind(ctx context.Context, conn net.Conn, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
if binder, ok := tr.connector.(connector.Binder); ok {
|
||||
return binder.Bind(ctx, conn, network, address, opts...)
|
||||
}
|
||||
return nil, connector.ErrBindUnsupported
|
||||
}
|
||||
|
||||
func (tr *Transport) Multiplex() bool {
|
||||
if mux, ok := tr.dialer.(dialer.Multiplexer); ok {
|
||||
return mux.Multiplex()
|
||||
}
|
||||
return false
|
||||
}
|
||||
|
||||
func (tr *Transport) WithRoute(r *Route) *Transport {
|
||||
tr.route = r
|
||||
return tr
|
||||
}
|
||||
|
||||
func (tr *Transport) WithAddr(addr string) *Transport {
|
||||
tr.addr = addr
|
||||
return tr
|
||||
}
|
||||
@@ -1,113 +0,0 @@
|
||||
package bufpool
|
||||
|
||||
import "sync"
|
||||
|
||||
var (
|
||||
pools = []struct {
|
||||
size int
|
||||
pool sync.Pool
|
||||
}{
|
||||
{
|
||||
size: 128,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 128)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 512,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 512)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 1024,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 1024)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 4096,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 4096)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 8192,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 8192)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 16 * 1024,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 16*1024)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 32 * 1024,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 32*1024)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 64 * 1024,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 64*1024)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
{
|
||||
size: 65 * 1024,
|
||||
pool: sync.Pool{
|
||||
New: func() interface{} {
|
||||
b := make([]byte, 65*1024)
|
||||
return &b
|
||||
},
|
||||
},
|
||||
},
|
||||
}
|
||||
)
|
||||
|
||||
// Get returns a buffer of specified size.
|
||||
func Get(size int) *[]byte {
|
||||
for i := range pools {
|
||||
if size <= pools[i].size {
|
||||
b := pools[i].pool.Get().(*[]byte)
|
||||
*b = (*b)[:size]
|
||||
return b
|
||||
}
|
||||
}
|
||||
b := make([]byte, size)
|
||||
return &b
|
||||
}
|
||||
|
||||
func Put(b *[]byte) {
|
||||
for i := range pools {
|
||||
if cap(*b) == pools[i].size {
|
||||
pools[i].pool.Put(b)
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -1,99 +0,0 @@
|
||||
package matcher
|
||||
|
||||
import (
|
||||
"net"
|
||||
"strings"
|
||||
|
||||
"github.com/gobwas/glob"
|
||||
)
|
||||
|
||||
// Matcher is a generic pattern matcher,
|
||||
// it gives the match result of the given pattern for specific v.
|
||||
type Matcher interface {
|
||||
Match(v string) bool
|
||||
}
|
||||
|
||||
// NewMatcher creates a Matcher for the given pattern.
|
||||
// The acutal Matcher depends on the pattern:
|
||||
// IP Matcher if pattern is a valid IP address.
|
||||
// CIDR Matcher if pattern is a valid CIDR address.
|
||||
// Domain Matcher if both of the above are not.
|
||||
func NewMatcher(pattern string) Matcher {
|
||||
if pattern == "" {
|
||||
return nil
|
||||
}
|
||||
if ip := net.ParseIP(pattern); ip != nil {
|
||||
return IPMatcher(ip)
|
||||
}
|
||||
if _, inet, err := net.ParseCIDR(pattern); err == nil {
|
||||
return CIDRMatcher(inet)
|
||||
}
|
||||
return DomainMatcher(pattern)
|
||||
}
|
||||
|
||||
type ipMatcher struct {
|
||||
ip net.IP
|
||||
}
|
||||
|
||||
// IPMatcher creates a Matcher for a specific IP address.
|
||||
func IPMatcher(ip net.IP) Matcher {
|
||||
return &ipMatcher{
|
||||
ip: ip,
|
||||
}
|
||||
}
|
||||
|
||||
func (m *ipMatcher) Match(ip string) bool {
|
||||
if m == nil {
|
||||
return false
|
||||
}
|
||||
return m.ip.Equal(net.ParseIP(ip))
|
||||
}
|
||||
|
||||
type cidrMatcher struct {
|
||||
ipNet *net.IPNet
|
||||
}
|
||||
|
||||
// CIDRMatcher creates a Matcher for a specific CIDR notation IP address.
|
||||
func CIDRMatcher(inet *net.IPNet) Matcher {
|
||||
return &cidrMatcher{
|
||||
ipNet: inet,
|
||||
}
|
||||
}
|
||||
|
||||
func (m *cidrMatcher) Match(ip string) bool {
|
||||
if m == nil || m.ipNet == nil {
|
||||
return false
|
||||
}
|
||||
return m.ipNet.Contains(net.ParseIP(ip))
|
||||
}
|
||||
|
||||
type domainMatcher struct {
|
||||
pattern string
|
||||
glob glob.Glob
|
||||
}
|
||||
|
||||
// DomainMatcher creates a Matcher for a specific domain pattern,
|
||||
// the pattern can be a plain domain such as 'example.com',
|
||||
// a wildcard such as '*.exmaple.com' or a special wildcard '.example.com'.
|
||||
func DomainMatcher(pattern string) Matcher {
|
||||
p := pattern
|
||||
if strings.HasPrefix(pattern, ".") {
|
||||
p = pattern[1:] // trim the prefix '.'
|
||||
pattern = "*" + p
|
||||
}
|
||||
return &domainMatcher{
|
||||
pattern: p,
|
||||
glob: glob.MustCompile(pattern),
|
||||
}
|
||||
}
|
||||
|
||||
func (m *domainMatcher) Match(domain string) bool {
|
||||
if m == nil || m.glob == nil {
|
||||
return false
|
||||
}
|
||||
|
||||
if domain == m.pattern {
|
||||
return true
|
||||
}
|
||||
return m.glob.Match(domain)
|
||||
}
|
||||
@@ -1,148 +0,0 @@
|
||||
// Code generated by protoc-gen-go. DO NOT EDIT.
|
||||
// versions:
|
||||
// protoc-gen-go v1.26.0
|
||||
// protoc v3.12.4
|
||||
// source: gost.proto
|
||||
|
||||
package proto
|
||||
|
||||
import (
|
||||
protoreflect "google.golang.org/protobuf/reflect/protoreflect"
|
||||
protoimpl "google.golang.org/protobuf/runtime/protoimpl"
|
||||
reflect "reflect"
|
||||
sync "sync"
|
||||
)
|
||||
|
||||
const (
|
||||
// Verify that this generated code is sufficiently up-to-date.
|
||||
_ = protoimpl.EnforceVersion(20 - protoimpl.MinVersion)
|
||||
// Verify that runtime/protoimpl is sufficiently up-to-date.
|
||||
_ = protoimpl.EnforceVersion(protoimpl.MaxVersion - 20)
|
||||
)
|
||||
|
||||
type Chunk struct {
|
||||
state protoimpl.MessageState
|
||||
sizeCache protoimpl.SizeCache
|
||||
unknownFields protoimpl.UnknownFields
|
||||
|
||||
Data []byte `protobuf:"bytes,1,opt,name=data,proto3" json:"data,omitempty"`
|
||||
}
|
||||
|
||||
func (x *Chunk) Reset() {
|
||||
*x = Chunk{}
|
||||
if protoimpl.UnsafeEnabled {
|
||||
mi := &file_gost_proto_msgTypes[0]
|
||||
ms := protoimpl.X.MessageStateOf(protoimpl.Pointer(x))
|
||||
ms.StoreMessageInfo(mi)
|
||||
}
|
||||
}
|
||||
|
||||
func (x *Chunk) String() string {
|
||||
return protoimpl.X.MessageStringOf(x)
|
||||
}
|
||||
|
||||
func (*Chunk) ProtoMessage() {}
|
||||
|
||||
func (x *Chunk) ProtoReflect() protoreflect.Message {
|
||||
mi := &file_gost_proto_msgTypes[0]
|
||||
if protoimpl.UnsafeEnabled && x != nil {
|
||||
ms := protoimpl.X.MessageStateOf(protoimpl.Pointer(x))
|
||||
if ms.LoadMessageInfo() == nil {
|
||||
ms.StoreMessageInfo(mi)
|
||||
}
|
||||
return ms
|
||||
}
|
||||
return mi.MessageOf(x)
|
||||
}
|
||||
|
||||
// Deprecated: Use Chunk.ProtoReflect.Descriptor instead.
|
||||
func (*Chunk) Descriptor() ([]byte, []int) {
|
||||
return file_gost_proto_rawDescGZIP(), []int{0}
|
||||
}
|
||||
|
||||
func (x *Chunk) GetData() []byte {
|
||||
if x != nil {
|
||||
return x.Data
|
||||
}
|
||||
return nil
|
||||
}
|
||||
|
||||
var File_gost_proto protoreflect.FileDescriptor
|
||||
|
||||
var file_gost_proto_rawDesc = []byte{
|
||||
0x0a, 0x0a, 0x67, 0x6f, 0x73, 0x74, 0x2e, 0x70, 0x72, 0x6f, 0x74, 0x6f, 0x22, 0x1b, 0x0a, 0x05,
|
||||
0x43, 0x68, 0x75, 0x6e, 0x6b, 0x12, 0x12, 0x0a, 0x04, 0x64, 0x61, 0x74, 0x61, 0x18, 0x01, 0x20,
|
||||
0x01, 0x28, 0x0c, 0x52, 0x04, 0x64, 0x61, 0x74, 0x61, 0x32, 0x29, 0x0a, 0x09, 0x47, 0x6f, 0x73,
|
||||
0x74, 0x54, 0x75, 0x6e, 0x65, 0x6c, 0x12, 0x1c, 0x0a, 0x06, 0x54, 0x75, 0x6e, 0x6e, 0x65, 0x6c,
|
||||
0x12, 0x06, 0x2e, 0x43, 0x68, 0x75, 0x6e, 0x6b, 0x1a, 0x06, 0x2e, 0x43, 0x68, 0x75, 0x6e, 0x6b,
|
||||
0x28, 0x01, 0x30, 0x01, 0x42, 0x34, 0x5a, 0x32, 0x67, 0x69, 0x74, 0x68, 0x75, 0x62, 0x2e, 0x63,
|
||||
0x6f, 0x6d, 0x2f, 0x67, 0x6f, 0x2d, 0x67, 0x6f, 0x73, 0x74, 0x2f, 0x67, 0x6f, 0x73, 0x74, 0x2f,
|
||||
0x70, 0x6b, 0x67, 0x2f, 0x63, 0x6f, 0x6d, 0x6d, 0x6f, 0x6e, 0x2f, 0x75, 0x74, 0x69, 0x6c, 0x2f,
|
||||
0x67, 0x72, 0x70, 0x63, 0x2f, 0x70, 0x72, 0x6f, 0x74, 0x6f, 0x62, 0x06, 0x70, 0x72, 0x6f, 0x74,
|
||||
0x6f, 0x33,
|
||||
}
|
||||
|
||||
var (
|
||||
file_gost_proto_rawDescOnce sync.Once
|
||||
file_gost_proto_rawDescData = file_gost_proto_rawDesc
|
||||
)
|
||||
|
||||
func file_gost_proto_rawDescGZIP() []byte {
|
||||
file_gost_proto_rawDescOnce.Do(func() {
|
||||
file_gost_proto_rawDescData = protoimpl.X.CompressGZIP(file_gost_proto_rawDescData)
|
||||
})
|
||||
return file_gost_proto_rawDescData
|
||||
}
|
||||
|
||||
var file_gost_proto_msgTypes = make([]protoimpl.MessageInfo, 1)
|
||||
var file_gost_proto_goTypes = []interface{}{
|
||||
(*Chunk)(nil), // 0: Chunk
|
||||
}
|
||||
var file_gost_proto_depIdxs = []int32{
|
||||
0, // 0: GostTunel.Tunnel:input_type -> Chunk
|
||||
0, // 1: GostTunel.Tunnel:output_type -> Chunk
|
||||
1, // [1:2] is the sub-list for method output_type
|
||||
0, // [0:1] is the sub-list for method input_type
|
||||
0, // [0:0] is the sub-list for extension type_name
|
||||
0, // [0:0] is the sub-list for extension extendee
|
||||
0, // [0:0] is the sub-list for field type_name
|
||||
}
|
||||
|
||||
func init() { file_gost_proto_init() }
|
||||
func file_gost_proto_init() {
|
||||
if File_gost_proto != nil {
|
||||
return
|
||||
}
|
||||
if !protoimpl.UnsafeEnabled {
|
||||
file_gost_proto_msgTypes[0].Exporter = func(v interface{}, i int) interface{} {
|
||||
switch v := v.(*Chunk); i {
|
||||
case 0:
|
||||
return &v.state
|
||||
case 1:
|
||||
return &v.sizeCache
|
||||
case 2:
|
||||
return &v.unknownFields
|
||||
default:
|
||||
return nil
|
||||
}
|
||||
}
|
||||
}
|
||||
type x struct{}
|
||||
out := protoimpl.TypeBuilder{
|
||||
File: protoimpl.DescBuilder{
|
||||
GoPackagePath: reflect.TypeOf(x{}).PkgPath(),
|
||||
RawDescriptor: file_gost_proto_rawDesc,
|
||||
NumEnums: 0,
|
||||
NumMessages: 1,
|
||||
NumExtensions: 0,
|
||||
NumServices: 1,
|
||||
},
|
||||
GoTypes: file_gost_proto_goTypes,
|
||||
DependencyIndexes: file_gost_proto_depIdxs,
|
||||
MessageInfos: file_gost_proto_msgTypes,
|
||||
}.Build()
|
||||
File_gost_proto = out.File
|
||||
file_gost_proto_rawDesc = nil
|
||||
file_gost_proto_goTypes = nil
|
||||
file_gost_proto_depIdxs = nil
|
||||
}
|
||||
@@ -1,10 +0,0 @@
|
||||
syntax = "proto3";
|
||||
option go_package = "github.com/go-gost/gost/pkg/common/util/grpc/proto";
|
||||
|
||||
message Chunk {
|
||||
bytes data = 1;
|
||||
}
|
||||
|
||||
service GostTunel {
|
||||
rpc Tunnel (stream Chunk) returns (stream Chunk);
|
||||
}
|
||||
@@ -1,133 +0,0 @@
|
||||
// Code generated by protoc-gen-go-grpc. DO NOT EDIT.
|
||||
|
||||
package proto
|
||||
|
||||
import (
|
||||
context "context"
|
||||
grpc "google.golang.org/grpc"
|
||||
codes "google.golang.org/grpc/codes"
|
||||
status "google.golang.org/grpc/status"
|
||||
)
|
||||
|
||||
// This is a compile-time assertion to ensure that this generated file
|
||||
// is compatible with the grpc package it is being compiled against.
|
||||
// Requires gRPC-Go v1.32.0 or later.
|
||||
const _ = grpc.SupportPackageIsVersion7
|
||||
|
||||
// GostTunelClient is the client API for GostTunel service.
|
||||
//
|
||||
// For semantics around ctx use and closing/ending streaming RPCs, please refer to https://pkg.go.dev/google.golang.org/grpc/?tab=doc#ClientConn.NewStream.
|
||||
type GostTunelClient interface {
|
||||
Tunnel(ctx context.Context, opts ...grpc.CallOption) (GostTunel_TunnelClient, error)
|
||||
}
|
||||
|
||||
type gostTunelClient struct {
|
||||
cc grpc.ClientConnInterface
|
||||
}
|
||||
|
||||
func NewGostTunelClient(cc grpc.ClientConnInterface) GostTunelClient {
|
||||
return &gostTunelClient{cc}
|
||||
}
|
||||
|
||||
func (c *gostTunelClient) Tunnel(ctx context.Context, opts ...grpc.CallOption) (GostTunel_TunnelClient, error) {
|
||||
stream, err := c.cc.NewStream(ctx, &GostTunel_ServiceDesc.Streams[0], "/GostTunel/Tunnel", opts...)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
x := &gostTunelTunnelClient{stream}
|
||||
return x, nil
|
||||
}
|
||||
|
||||
type GostTunel_TunnelClient interface {
|
||||
Send(*Chunk) error
|
||||
Recv() (*Chunk, error)
|
||||
grpc.ClientStream
|
||||
}
|
||||
|
||||
type gostTunelTunnelClient struct {
|
||||
grpc.ClientStream
|
||||
}
|
||||
|
||||
func (x *gostTunelTunnelClient) Send(m *Chunk) error {
|
||||
return x.ClientStream.SendMsg(m)
|
||||
}
|
||||
|
||||
func (x *gostTunelTunnelClient) Recv() (*Chunk, error) {
|
||||
m := new(Chunk)
|
||||
if err := x.ClientStream.RecvMsg(m); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return m, nil
|
||||
}
|
||||
|
||||
// GostTunelServer is the server API for GostTunel service.
|
||||
// All implementations must embed UnimplementedGostTunelServer
|
||||
// for forward compatibility
|
||||
type GostTunelServer interface {
|
||||
Tunnel(GostTunel_TunnelServer) error
|
||||
mustEmbedUnimplementedGostTunelServer()
|
||||
}
|
||||
|
||||
// UnimplementedGostTunelServer must be embedded to have forward compatible implementations.
|
||||
type UnimplementedGostTunelServer struct {
|
||||
}
|
||||
|
||||
func (UnimplementedGostTunelServer) Tunnel(GostTunel_TunnelServer) error {
|
||||
return status.Errorf(codes.Unimplemented, "method Tunnel not implemented")
|
||||
}
|
||||
func (UnimplementedGostTunelServer) mustEmbedUnimplementedGostTunelServer() {}
|
||||
|
||||
// UnsafeGostTunelServer may be embedded to opt out of forward compatibility for this service.
|
||||
// Use of this interface is not recommended, as added methods to GostTunelServer will
|
||||
// result in compilation errors.
|
||||
type UnsafeGostTunelServer interface {
|
||||
mustEmbedUnimplementedGostTunelServer()
|
||||
}
|
||||
|
||||
func RegisterGostTunelServer(s grpc.ServiceRegistrar, srv GostTunelServer) {
|
||||
s.RegisterService(&GostTunel_ServiceDesc, srv)
|
||||
}
|
||||
|
||||
func _GostTunel_Tunnel_Handler(srv interface{}, stream grpc.ServerStream) error {
|
||||
return srv.(GostTunelServer).Tunnel(&gostTunelTunnelServer{stream})
|
||||
}
|
||||
|
||||
type GostTunel_TunnelServer interface {
|
||||
Send(*Chunk) error
|
||||
Recv() (*Chunk, error)
|
||||
grpc.ServerStream
|
||||
}
|
||||
|
||||
type gostTunelTunnelServer struct {
|
||||
grpc.ServerStream
|
||||
}
|
||||
|
||||
func (x *gostTunelTunnelServer) Send(m *Chunk) error {
|
||||
return x.ServerStream.SendMsg(m)
|
||||
}
|
||||
|
||||
func (x *gostTunelTunnelServer) Recv() (*Chunk, error) {
|
||||
m := new(Chunk)
|
||||
if err := x.ServerStream.RecvMsg(m); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return m, nil
|
||||
}
|
||||
|
||||
// GostTunel_ServiceDesc is the grpc.ServiceDesc for GostTunel service.
|
||||
// It's only intended for direct use with grpc.RegisterService,
|
||||
// and not to be introspected or modified (even as a copy)
|
||||
var GostTunel_ServiceDesc = grpc.ServiceDesc{
|
||||
ServiceName: "GostTunel",
|
||||
HandlerType: (*GostTunelServer)(nil),
|
||||
Methods: []grpc.MethodDesc{},
|
||||
Streams: []grpc.StreamDesc{
|
||||
{
|
||||
StreamName: "Tunnel",
|
||||
Handler: _GostTunel_Tunnel_Handler,
|
||||
ServerStreams: true,
|
||||
ClientStreams: true,
|
||||
},
|
||||
},
|
||||
Metadata: "gost.proto",
|
||||
}
|
||||
@@ -1,3 +0,0 @@
|
||||
protoc --go_out=. --go_opt=paths=source_relative \
|
||||
--go-grpc_out=. --go-grpc_opt=paths=source_relative \
|
||||
gost.proto
|
||||
@@ -1,115 +0,0 @@
|
||||
package kcp
|
||||
|
||||
import (
|
||||
"crypto/sha1"
|
||||
|
||||
"github.com/xtaci/kcp-go/v5"
|
||||
"golang.org/x/crypto/pbkdf2"
|
||||
)
|
||||
|
||||
var (
|
||||
// DefaultSalt is the default salt for KCP cipher.
|
||||
DefaultSalt = "kcp-go"
|
||||
)
|
||||
|
||||
var (
|
||||
// DefaultKCPConfig is the default KCP config.
|
||||
DefaultConfig = &Config{
|
||||
Key: "it's a secrect",
|
||||
Crypt: "aes",
|
||||
Mode: "fast",
|
||||
MTU: 1350,
|
||||
SndWnd: 1024,
|
||||
RcvWnd: 1024,
|
||||
DataShard: 10,
|
||||
ParityShard: 3,
|
||||
DSCP: 0,
|
||||
NoComp: false,
|
||||
AckNodelay: false,
|
||||
NoDelay: 0,
|
||||
Interval: 50,
|
||||
Resend: 0,
|
||||
NoCongestion: 0,
|
||||
SockBuf: 4194304,
|
||||
KeepAlive: 10,
|
||||
SnmpLog: "",
|
||||
SnmpPeriod: 60,
|
||||
Signal: false,
|
||||
TCP: false,
|
||||
}
|
||||
)
|
||||
|
||||
// KCPConfig describes the config for KCP.
|
||||
type Config struct {
|
||||
Key string `json:"key"`
|
||||
Crypt string `json:"crypt"`
|
||||
Mode string `json:"mode"`
|
||||
MTU int `json:"mtu"`
|
||||
SndWnd int `json:"sndwnd"`
|
||||
RcvWnd int `json:"rcvwnd"`
|
||||
DataShard int `json:"datashard"`
|
||||
ParityShard int `json:"parityshard"`
|
||||
DSCP int `json:"dscp"`
|
||||
NoComp bool `json:"nocomp"`
|
||||
AckNodelay bool `json:"acknodelay"`
|
||||
NoDelay int `json:"nodelay"`
|
||||
Interval int `json:"interval"`
|
||||
Resend int `json:"resend"`
|
||||
NoCongestion int `json:"nc"`
|
||||
SockBuf int `json:"sockbuf"`
|
||||
KeepAlive int `json:"keepalive"`
|
||||
SnmpLog string `json:"snmplog"`
|
||||
SnmpPeriod int `json:"snmpperiod"`
|
||||
Signal bool `json:"signal"` // Signal enables the signal SIGUSR1 feature.
|
||||
TCP bool `json:"tcp"`
|
||||
}
|
||||
|
||||
// Init initializes the KCP config.
|
||||
func (c *Config) Init() {
|
||||
switch c.Mode {
|
||||
case "normal":
|
||||
c.NoDelay, c.Interval, c.Resend, c.NoCongestion = 0, 40, 2, 1
|
||||
case "fast":
|
||||
c.NoDelay, c.Interval, c.Resend, c.NoCongestion = 0, 30, 2, 1
|
||||
case "fast2":
|
||||
c.NoDelay, c.Interval, c.Resend, c.NoCongestion = 1, 20, 2, 1
|
||||
case "fast3":
|
||||
c.NoDelay, c.Interval, c.Resend, c.NoCongestion = 1, 10, 2, 1
|
||||
}
|
||||
}
|
||||
|
||||
func BlockCrypt(key, crypt, salt string) (block kcp.BlockCrypt) {
|
||||
pass := pbkdf2.Key([]byte(key), []byte(salt), 4096, 32, sha1.New)
|
||||
|
||||
switch crypt {
|
||||
case "sm4":
|
||||
block, _ = kcp.NewSM4BlockCrypt(pass[:16])
|
||||
case "tea":
|
||||
block, _ = kcp.NewTEABlockCrypt(pass[:16])
|
||||
case "xor":
|
||||
block, _ = kcp.NewSimpleXORBlockCrypt(pass)
|
||||
case "none":
|
||||
block, _ = kcp.NewNoneBlockCrypt(pass)
|
||||
case "aes-128":
|
||||
block, _ = kcp.NewAESBlockCrypt(pass[:16])
|
||||
case "aes-192":
|
||||
block, _ = kcp.NewAESBlockCrypt(pass[:24])
|
||||
case "blowfish":
|
||||
block, _ = kcp.NewBlowfishBlockCrypt(pass)
|
||||
case "twofish":
|
||||
block, _ = kcp.NewTwofishBlockCrypt(pass)
|
||||
case "cast5":
|
||||
block, _ = kcp.NewCast5BlockCrypt(pass[:16])
|
||||
case "3des":
|
||||
block, _ = kcp.NewTripleDESBlockCrypt(pass[:24])
|
||||
case "xtea":
|
||||
block, _ = kcp.NewXTEABlockCrypt(pass[:16])
|
||||
case "salsa20":
|
||||
block, _ = kcp.NewSalsa20BlockCrypt(pass)
|
||||
case "aes":
|
||||
fallthrough
|
||||
default: // aes
|
||||
block, _ = kcp.NewAESBlockCrypt(pass)
|
||||
}
|
||||
return
|
||||
}
|
||||
@@ -1,34 +0,0 @@
|
||||
package kcp
|
||||
|
||||
import (
|
||||
"net"
|
||||
|
||||
"github.com/golang/snappy"
|
||||
)
|
||||
|
||||
type kcpCompStreamConn struct {
|
||||
net.Conn
|
||||
w *snappy.Writer
|
||||
r *snappy.Reader
|
||||
}
|
||||
|
||||
func CompStreamConn(conn net.Conn) net.Conn {
|
||||
return &kcpCompStreamConn{
|
||||
Conn: conn,
|
||||
w: snappy.NewBufferedWriter(conn),
|
||||
r: snappy.NewReader(conn),
|
||||
}
|
||||
}
|
||||
|
||||
func (c *kcpCompStreamConn) Read(b []byte) (n int, err error) {
|
||||
return c.r.Read(b)
|
||||
}
|
||||
|
||||
func (c *kcpCompStreamConn) Write(b []byte) (n int, err error) {
|
||||
n, err = c.w.Write(b)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
err = c.w.Flush()
|
||||
return n, err
|
||||
}
|
||||
@@ -1,85 +0,0 @@
|
||||
package mux
|
||||
|
||||
import (
|
||||
"net"
|
||||
|
||||
smux "github.com/xtaci/smux"
|
||||
)
|
||||
|
||||
type Session struct {
|
||||
conn net.Conn
|
||||
session *smux.Session
|
||||
}
|
||||
|
||||
func ClientSession(conn net.Conn) (*Session, error) {
|
||||
s, err := smux.Client(conn, smux.DefaultConfig())
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return &Session{
|
||||
conn: conn,
|
||||
session: s,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func ServerSession(conn net.Conn) (*Session, error) {
|
||||
s, err := smux.Server(conn, smux.DefaultConfig())
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return &Session{
|
||||
conn: conn,
|
||||
session: s,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (session *Session) GetConn() (net.Conn, error) {
|
||||
stream, err := session.session.OpenStream()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return &StreamConn{Conn: session.conn, stream: stream}, nil
|
||||
}
|
||||
|
||||
func (session *Session) Accept() (net.Conn, error) {
|
||||
stream, err := session.session.AcceptStream()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
return &StreamConn{Conn: session.conn, stream: stream}, nil
|
||||
}
|
||||
|
||||
func (session *Session) Close() error {
|
||||
if session.session == nil {
|
||||
return nil
|
||||
}
|
||||
return session.session.Close()
|
||||
}
|
||||
|
||||
func (session *Session) IsClosed() bool {
|
||||
if session.session == nil {
|
||||
return true
|
||||
}
|
||||
return session.session.IsClosed()
|
||||
}
|
||||
|
||||
func (session *Session) NumStreams() int {
|
||||
return session.session.NumStreams()
|
||||
}
|
||||
|
||||
type StreamConn struct {
|
||||
net.Conn
|
||||
stream *smux.Stream
|
||||
}
|
||||
|
||||
func (c *StreamConn) Read(b []byte) (n int, err error) {
|
||||
return c.stream.Read(b)
|
||||
}
|
||||
|
||||
func (c *StreamConn) Write(b []byte) (n int, err error) {
|
||||
return c.stream.Write(b)
|
||||
}
|
||||
|
||||
func (c *StreamConn) Close() error {
|
||||
return c.stream.Close()
|
||||
}
|
||||
@@ -1,172 +0,0 @@
|
||||
package socks
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/bufpool"
|
||||
)
|
||||
|
||||
type udpTunConn struct {
|
||||
net.Conn
|
||||
taddr net.Addr
|
||||
}
|
||||
|
||||
func UDPTunClientConn(c net.Conn, targetAddr net.Addr) net.Conn {
|
||||
return &udpTunConn{
|
||||
Conn: c,
|
||||
taddr: targetAddr,
|
||||
}
|
||||
}
|
||||
|
||||
func UDPTunClientPacketConn(c net.Conn) net.PacketConn {
|
||||
return &udpTunConn{
|
||||
Conn: c,
|
||||
}
|
||||
}
|
||||
|
||||
func UDPTunServerConn(c net.Conn) net.PacketConn {
|
||||
return &udpTunConn{
|
||||
Conn: c,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *udpTunConn) ReadFrom(b []byte) (n int, addr net.Addr, err error) {
|
||||
socksAddr := gosocks5.Addr{}
|
||||
header := gosocks5.UDPHeader{
|
||||
Addr: &socksAddr,
|
||||
}
|
||||
dgram := gosocks5.UDPDatagram{
|
||||
Header: &header,
|
||||
Data: b,
|
||||
}
|
||||
_, err = dgram.ReadFrom(c.Conn)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
n = len(dgram.Data)
|
||||
if n > len(b) {
|
||||
n = copy(b, dgram.Data)
|
||||
}
|
||||
addr, err = net.ResolveUDPAddr("udp", socksAddr.String())
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpTunConn) Read(b []byte) (n int, err error) {
|
||||
n, _, err = c.ReadFrom(b)
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpTunConn) WriteTo(b []byte, addr net.Addr) (n int, err error) {
|
||||
socksAddr := gosocks5.Addr{}
|
||||
if err = socksAddr.ParseFrom(addr.String()); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
header := gosocks5.UDPHeader{
|
||||
Addr: &socksAddr,
|
||||
}
|
||||
dgram := gosocks5.UDPDatagram{
|
||||
Header: &header,
|
||||
Data: b,
|
||||
}
|
||||
dgram.Header.Rsv = uint16(len(dgram.Data))
|
||||
dgram.Header.Frag = 0xff // UDP tun relay flag, used by shadowsocks
|
||||
_, err = dgram.WriteTo(c.Conn)
|
||||
n = len(b)
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpTunConn) Write(b []byte) (n int, err error) {
|
||||
return c.WriteTo(b, c.taddr)
|
||||
}
|
||||
|
||||
var (
|
||||
DefaultBufferSize = 4096
|
||||
)
|
||||
|
||||
type udpConn struct {
|
||||
net.PacketConn
|
||||
raddr net.Addr
|
||||
taddr net.Addr
|
||||
bufferSize int
|
||||
}
|
||||
|
||||
func UDPConn(c net.PacketConn, bufferSize int) net.PacketConn {
|
||||
return &udpConn{
|
||||
PacketConn: c,
|
||||
bufferSize: bufferSize,
|
||||
}
|
||||
}
|
||||
|
||||
// ReadFrom reads an UDP datagram.
|
||||
// NOTE: for server side,
|
||||
// the returned addr is the target address the client want to relay to.
|
||||
func (c *udpConn) ReadFrom(b []byte) (n int, addr net.Addr, err error) {
|
||||
rbuf := bufpool.Get(c.bufferSize)
|
||||
defer bufpool.Put(rbuf)
|
||||
|
||||
n, c.raddr, err = c.PacketConn.ReadFrom(*rbuf)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
socksAddr := gosocks5.Addr{}
|
||||
header := gosocks5.UDPHeader{
|
||||
Addr: &socksAddr,
|
||||
}
|
||||
hlen, err := header.ReadFrom(bytes.NewReader((*rbuf)[:n]))
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
n = copy(b, (*rbuf)[hlen:n])
|
||||
|
||||
addr, err = net.ResolveUDPAddr("udp", socksAddr.String())
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpConn) Read(b []byte) (n int, err error) {
|
||||
n, _, err = c.ReadFrom(b)
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpConn) WriteTo(b []byte, addr net.Addr) (n int, err error) {
|
||||
wbuf := bufpool.Get(c.bufferSize)
|
||||
defer bufpool.Put(wbuf)
|
||||
|
||||
socksAddr := gosocks5.Addr{}
|
||||
if err = socksAddr.ParseFrom(addr.String()); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
header := gosocks5.UDPHeader{
|
||||
Addr: &socksAddr,
|
||||
}
|
||||
dgram := gosocks5.UDPDatagram{
|
||||
Header: &header,
|
||||
Data: b,
|
||||
}
|
||||
|
||||
buf := bytes.NewBuffer((*wbuf)[:0])
|
||||
_, err = dgram.WriteTo(buf)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
_, err = c.PacketConn.WriteTo(buf.Bytes(), c.raddr)
|
||||
n = len(b)
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpConn) Write(b []byte) (n int, err error) {
|
||||
return c.WriteTo(b, c.taddr)
|
||||
}
|
||||
|
||||
func (c *udpConn) RemoteAddr() net.Addr {
|
||||
return c.raddr
|
||||
}
|
||||
@@ -1,18 +0,0 @@
|
||||
package socks
|
||||
|
||||
const (
|
||||
// MethodTLS is an extended SOCKS5 method with tls encryption support.
|
||||
MethodTLS uint8 = 0x80
|
||||
// MethodTLSAuth is an extended SOCKS5 method with tls encryption and authentication support.
|
||||
MethodTLSAuth uint8 = 0x82
|
||||
// MethodMux is an extended SOCKS5 method for stream multiplexing.
|
||||
MethodMux = 0x88
|
||||
)
|
||||
|
||||
const (
|
||||
// CmdMuxBind is an extended SOCKS5 request CMD for
|
||||
// multiplexing transport with the binding server.
|
||||
CmdMuxBind uint8 = 0xF2
|
||||
// CmdUDPTun is an extended SOCKS5 request CMD for UDP over TCP.
|
||||
CmdUDPTun uint8 = 0xF3
|
||||
)
|
||||
@@ -1,96 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/bufpool"
|
||||
)
|
||||
|
||||
var (
|
||||
DefaultBufferSize = 4096
|
||||
)
|
||||
|
||||
var (
|
||||
_ net.PacketConn = (*UDPConn)(nil)
|
||||
_ net.Conn = (*UDPConn)(nil)
|
||||
)
|
||||
|
||||
type UDPConn struct {
|
||||
net.PacketConn
|
||||
raddr net.Addr
|
||||
taddr net.Addr
|
||||
bufferSize int
|
||||
}
|
||||
|
||||
func UDPClientConn(c net.PacketConn, remoteAddr, targetAddr net.Addr, bufferSize int) *UDPConn {
|
||||
return &UDPConn{
|
||||
PacketConn: c,
|
||||
raddr: remoteAddr,
|
||||
taddr: targetAddr,
|
||||
bufferSize: bufferSize,
|
||||
}
|
||||
}
|
||||
|
||||
func UDPServerConn(c net.PacketConn, remoteAddr net.Addr, bufferSize int) *UDPConn {
|
||||
return &UDPConn{
|
||||
PacketConn: c,
|
||||
raddr: remoteAddr,
|
||||
bufferSize: bufferSize,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *UDPConn) ReadFrom(b []byte) (n int, addr net.Addr, err error) {
|
||||
rbuf := bufpool.Get(c.bufferSize)
|
||||
defer bufpool.Put(rbuf)
|
||||
|
||||
n, _, err = c.PacketConn.ReadFrom(*rbuf)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
saddr := gosocks5.Addr{}
|
||||
addrLen, err := saddr.ReadFrom(bytes.NewReader((*rbuf)[:n]))
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
n = copy(b, (*rbuf)[addrLen:n])
|
||||
addr, err = net.ResolveUDPAddr("udp", saddr.String())
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *UDPConn) Read(b []byte) (n int, err error) {
|
||||
n, _, err = c.ReadFrom(b)
|
||||
return
|
||||
}
|
||||
|
||||
func (c *UDPConn) WriteTo(b []byte, addr net.Addr) (n int, err error) {
|
||||
wbuf := bufpool.Get(c.bufferSize)
|
||||
defer bufpool.Put(wbuf)
|
||||
|
||||
socksAddr := gosocks5.Addr{}
|
||||
if err = socksAddr.ParseFrom(addr.String()); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
addrLen, err := socksAddr.Encode(*wbuf)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
n = copy((*wbuf)[addrLen:], b)
|
||||
_, err = c.PacketConn.WriteTo((*wbuf)[:addrLen+n], c.raddr)
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *UDPConn) Write(b []byte) (n int, err error) {
|
||||
return c.WriteTo(b, c.taddr)
|
||||
}
|
||||
|
||||
func (c *UDPConn) RemoteAddr() net.Addr {
|
||||
return c.raddr
|
||||
}
|
||||
@@ -1,60 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"net"
|
||||
|
||||
"github.com/shadowsocks/go-shadowsocks2/core"
|
||||
ss "github.com/shadowsocks/shadowsocks-go/shadowsocks"
|
||||
)
|
||||
|
||||
type shadowCipher struct {
|
||||
cipher *ss.Cipher
|
||||
}
|
||||
|
||||
func (c *shadowCipher) StreamConn(conn net.Conn) net.Conn {
|
||||
return ss.NewConn(conn, c.cipher.Copy())
|
||||
}
|
||||
|
||||
func (c *shadowCipher) PacketConn(conn net.PacketConn) net.PacketConn {
|
||||
return ss.NewSecurePacketConn(conn, c.cipher.Copy())
|
||||
}
|
||||
|
||||
func ShadowCipher(method, password string, key string) (core.Cipher, error) {
|
||||
if method == "" && password == "" {
|
||||
return nil, nil
|
||||
}
|
||||
|
||||
c, _ := ss.NewCipher(method, password)
|
||||
if c != nil {
|
||||
return &shadowCipher{cipher: c}, nil
|
||||
}
|
||||
|
||||
return core.PickCipher(method, []byte(key), password)
|
||||
}
|
||||
|
||||
// Due to in/out byte length is inconsistent of the shadowsocks.Conn.Write,
|
||||
// we wrap around it to make io.Copy happy.
|
||||
type shadowConn struct {
|
||||
net.Conn
|
||||
wbuf *bytes.Buffer
|
||||
}
|
||||
|
||||
func ShadowConn(conn net.Conn, header []byte) net.Conn {
|
||||
return &shadowConn{
|
||||
Conn: conn,
|
||||
wbuf: bytes.NewBuffer(header),
|
||||
}
|
||||
}
|
||||
|
||||
func (c *shadowConn) Write(b []byte) (n int, err error) {
|
||||
n = len(b) // force byte length consistent
|
||||
if c.wbuf.Len() > 0 {
|
||||
c.wbuf.Write(b) // append the data to the cached header
|
||||
_, err = c.Conn.Write(c.wbuf.Bytes())
|
||||
c.wbuf.Reset()
|
||||
return
|
||||
}
|
||||
_, err = c.Conn.Write(b)
|
||||
return
|
||||
}
|
||||
@@ -1,32 +0,0 @@
|
||||
package util
|
||||
|
||||
import (
|
||||
"net"
|
||||
"time"
|
||||
)
|
||||
|
||||
const (
|
||||
defaultKeepAlivePeriod = 180 * time.Second
|
||||
)
|
||||
|
||||
// TCPKeepAliveListener is a TCP listener with keep alive enabled.
|
||||
type TCPKeepAliveListener struct {
|
||||
KeepAlivePeriod time.Duration
|
||||
*net.TCPListener
|
||||
}
|
||||
|
||||
func (l *TCPKeepAliveListener) Accept() (c net.Conn, err error) {
|
||||
tc, err := l.AcceptTCP()
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
tc.SetKeepAlive(true)
|
||||
period := l.KeepAlivePeriod
|
||||
if period <= 0 {
|
||||
period = defaultKeepAlivePeriod
|
||||
}
|
||||
tc.SetKeepAlivePeriod(period)
|
||||
|
||||
return tc, nil
|
||||
}
|
||||
@@ -1,178 +0,0 @@
|
||||
package tls
|
||||
|
||||
import (
|
||||
"crypto/tls"
|
||||
"crypto/x509"
|
||||
"errors"
|
||||
"io/ioutil"
|
||||
"net"
|
||||
"time"
|
||||
)
|
||||
|
||||
var (
|
||||
// DefaultConfig is a default TLS config for global use.
|
||||
DefaultConfig *tls.Config
|
||||
)
|
||||
|
||||
// LoadServerConfig loads the certificate from cert & key files and optional client CA file.
|
||||
func LoadServerConfig(certFile, keyFile, caFile string) (*tls.Config, error) {
|
||||
if certFile == "" && keyFile == "" {
|
||||
return DefaultConfig.Clone(), nil
|
||||
}
|
||||
|
||||
cert, err := tls.LoadX509KeyPair(certFile, keyFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cfg := &tls.Config{Certificates: []tls.Certificate{cert}}
|
||||
|
||||
pool, err := loadCA(caFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
if pool != nil {
|
||||
cfg.ClientCAs = pool
|
||||
cfg.ClientAuth = tls.RequireAndVerifyClientCert
|
||||
}
|
||||
|
||||
return cfg, nil
|
||||
}
|
||||
|
||||
// LoadClientConfig loads the certificate from cert & key files and optional CA file.
|
||||
func LoadClientConfig(certFile, keyFile, caFile string, verify bool, serverName string) (*tls.Config, error) {
|
||||
var cfg *tls.Config
|
||||
|
||||
if certFile == "" && keyFile == "" {
|
||||
cfg = &tls.Config{}
|
||||
} else {
|
||||
cert, err := tls.LoadX509KeyPair(certFile, keyFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cfg = &tls.Config{
|
||||
Certificates: []tls.Certificate{cert},
|
||||
}
|
||||
}
|
||||
|
||||
rootCAs, err := loadCA(caFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cfg.RootCAs = rootCAs
|
||||
cfg.ServerName = serverName
|
||||
cfg.InsecureSkipVerify = !verify
|
||||
|
||||
// If the root ca is given, but skip verify, we verify the certificate manually.
|
||||
if cfg.RootCAs != nil && !verify {
|
||||
cfg.VerifyConnection = func(state tls.ConnectionState) error {
|
||||
opts := x509.VerifyOptions{
|
||||
Roots: cfg.RootCAs,
|
||||
CurrentTime: time.Now(),
|
||||
DNSName: "",
|
||||
Intermediates: x509.NewCertPool(),
|
||||
}
|
||||
|
||||
certs := state.PeerCertificates
|
||||
for i, cert := range certs {
|
||||
if i == 0 {
|
||||
continue
|
||||
}
|
||||
opts.Intermediates.AddCert(cert)
|
||||
}
|
||||
|
||||
_, err := certs[0].Verify(opts)
|
||||
return err
|
||||
}
|
||||
}
|
||||
|
||||
return cfg, nil
|
||||
}
|
||||
|
||||
func loadCA(caFile string) (cp *x509.CertPool, err error) {
|
||||
if caFile == "" {
|
||||
return
|
||||
}
|
||||
cp = x509.NewCertPool()
|
||||
data, err := ioutil.ReadFile(caFile)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
if !cp.AppendCertsFromPEM(data) {
|
||||
return nil, errors.New("AppendCertsFromPEM failed")
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
// Wrap a net.Conn into a client tls connection, performing any
|
||||
// additional verification as needed.
|
||||
//
|
||||
// As of go 1.3, crypto/tls only supports either doing no certificate
|
||||
// verification, or doing full verification including of the peer's
|
||||
// DNS name. For consul, we want to validate that the certificate is
|
||||
// signed by a known CA, but because consul doesn't use DNS names for
|
||||
// node names, we don't verify the certificate DNS names. Since go 1.3
|
||||
// no longer supports this mode of operation, we have to do it
|
||||
// manually.
|
||||
//
|
||||
// This code is taken from consul:
|
||||
// https://github.com/hashicorp/consul/blob/master/tlsutil/config.go
|
||||
func WrapTLSClient(conn net.Conn, tlsConfig *tls.Config, timeout time.Duration) (net.Conn, error) {
|
||||
var err error
|
||||
var tlsConn *tls.Conn
|
||||
|
||||
if timeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(timeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
tlsConn = tls.Client(conn, tlsConfig)
|
||||
|
||||
// Otherwise perform handshake, but don't verify the domain
|
||||
//
|
||||
// The following is lightly-modified from the doFullHandshake
|
||||
// method in https://golang.org/src/crypto/tls/handshake_client.go
|
||||
if err = tlsConn.Handshake(); err != nil {
|
||||
tlsConn.Close()
|
||||
return nil, err
|
||||
}
|
||||
|
||||
// We can do this in `tls.Config.VerifyConnection`, which effective for
|
||||
// other TLS protocols such as WebSocket. See `route.go:parseChainNode`
|
||||
/*
|
||||
// If crypto/tls is doing verification, there's no need to do our own.
|
||||
if tlsConfig.InsecureSkipVerify == false {
|
||||
return tlsConn, nil
|
||||
}
|
||||
|
||||
// Similarly if we use host's CA, we can do full handshake
|
||||
if tlsConfig.RootCAs == nil {
|
||||
return tlsConn, nil
|
||||
}
|
||||
|
||||
opts := x509.VerifyOptions{
|
||||
Roots: tlsConfig.RootCAs,
|
||||
CurrentTime: time.Now(),
|
||||
DNSName: "",
|
||||
Intermediates: x509.NewCertPool(),
|
||||
}
|
||||
|
||||
certs := tlsConn.ConnectionState().PeerCertificates
|
||||
for i, cert := range certs {
|
||||
if i == 0 {
|
||||
continue
|
||||
}
|
||||
opts.Intermediates.AddCert(cert)
|
||||
}
|
||||
|
||||
_, err = certs[0].Verify(opts)
|
||||
if err != nil {
|
||||
tlsConn.Close()
|
||||
return nil, err
|
||||
}
|
||||
*/
|
||||
|
||||
return tlsConn, err
|
||||
}
|
||||
@@ -1,102 +0,0 @@
|
||||
package udp
|
||||
|
||||
import (
|
||||
"errors"
|
||||
"net"
|
||||
"sync"
|
||||
"sync/atomic"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/bufpool"
|
||||
)
|
||||
|
||||
// Conn is a server side connection for UDP client peer, it implements net.Conn and net.PacketConn.
|
||||
type Conn struct {
|
||||
net.PacketConn
|
||||
localAddr net.Addr
|
||||
remoteAddr net.Addr
|
||||
rc chan []byte // data receive queue
|
||||
idle int32 // indicate the connection is idle
|
||||
closed chan struct{}
|
||||
closeMutex sync.Mutex
|
||||
}
|
||||
|
||||
func NewConn(c net.PacketConn, localAddr, remoteAddr net.Addr, queueSize int) *Conn {
|
||||
return &Conn{
|
||||
PacketConn: c,
|
||||
localAddr: localAddr,
|
||||
remoteAddr: remoteAddr,
|
||||
rc: make(chan []byte, queueSize),
|
||||
closed: make(chan struct{}),
|
||||
}
|
||||
}
|
||||
|
||||
func (c *Conn) ReadFrom(b []byte) (n int, addr net.Addr, err error) {
|
||||
select {
|
||||
case bb := <-c.rc:
|
||||
n = copy(b, bb)
|
||||
c.SetIdle(false)
|
||||
bufpool.Put(&bb)
|
||||
|
||||
case <-c.closed:
|
||||
err = net.ErrClosed
|
||||
return
|
||||
}
|
||||
|
||||
addr = c.remoteAddr
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *Conn) Read(b []byte) (n int, err error) {
|
||||
n, _, err = c.ReadFrom(b)
|
||||
return
|
||||
}
|
||||
|
||||
func (c *Conn) Write(b []byte) (n int, err error) {
|
||||
return c.WriteTo(b, c.remoteAddr)
|
||||
}
|
||||
|
||||
func (c *Conn) Close() error {
|
||||
c.closeMutex.Lock()
|
||||
defer c.closeMutex.Unlock()
|
||||
|
||||
select {
|
||||
case <-c.closed:
|
||||
default:
|
||||
close(c.closed)
|
||||
}
|
||||
return nil
|
||||
}
|
||||
|
||||
func (c *Conn) LocalAddr() net.Addr {
|
||||
return c.localAddr
|
||||
}
|
||||
|
||||
func (c *Conn) RemoteAddr() net.Addr {
|
||||
return c.remoteAddr
|
||||
}
|
||||
|
||||
func (c *Conn) IsIdle() bool {
|
||||
return atomic.LoadInt32(&c.idle) > 0
|
||||
}
|
||||
|
||||
func (c *Conn) SetIdle(idle bool) {
|
||||
v := int32(0)
|
||||
if idle {
|
||||
v = 1
|
||||
}
|
||||
atomic.StoreInt32(&c.idle, v)
|
||||
}
|
||||
|
||||
func (c *Conn) WriteQueue(b []byte) error {
|
||||
select {
|
||||
case c.rc <- b:
|
||||
return nil
|
||||
|
||||
case <-c.closed:
|
||||
return net.ErrClosed
|
||||
|
||||
default:
|
||||
return errors.New("recv queue is full")
|
||||
}
|
||||
}
|
||||
@@ -1,120 +0,0 @@
|
||||
package udp
|
||||
|
||||
import (
|
||||
"net"
|
||||
"sync"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/bufpool"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type listener struct {
|
||||
addr net.Addr
|
||||
conn net.PacketConn
|
||||
cqueue chan net.Conn
|
||||
readQueueSize int
|
||||
readBufferSize int
|
||||
connPool *ConnPool
|
||||
mux sync.Mutex
|
||||
closed chan struct{}
|
||||
errChan chan error
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func NewListener(conn net.PacketConn, addr net.Addr, backlog, dataQueueSize, dataBufferSize int, ttl time.Duration, logger logger.Logger) net.Listener {
|
||||
ln := &listener{
|
||||
conn: conn,
|
||||
addr: addr,
|
||||
cqueue: make(chan net.Conn, backlog),
|
||||
connPool: NewConnPool(ttl).WithLogger(logger),
|
||||
readQueueSize: dataQueueSize,
|
||||
readBufferSize: dataBufferSize,
|
||||
closed: make(chan struct{}),
|
||||
errChan: make(chan error, 1),
|
||||
logger: logger,
|
||||
}
|
||||
go ln.listenLoop()
|
||||
|
||||
return ln
|
||||
}
|
||||
|
||||
func (ln *listener) Accept() (conn net.Conn, err error) {
|
||||
select {
|
||||
case conn = <-ln.cqueue:
|
||||
return
|
||||
case <-ln.closed:
|
||||
return nil, net.ErrClosed
|
||||
case err = <-ln.errChan:
|
||||
if err == nil {
|
||||
err = net.ErrClosed
|
||||
}
|
||||
return
|
||||
}
|
||||
}
|
||||
|
||||
func (ln *listener) listenLoop() {
|
||||
for {
|
||||
select {
|
||||
case <-ln.closed:
|
||||
return
|
||||
default:
|
||||
}
|
||||
|
||||
b := bufpool.Get(ln.readBufferSize)
|
||||
|
||||
n, raddr, err := ln.conn.ReadFrom(*b)
|
||||
if err != nil {
|
||||
ln.errChan <- err
|
||||
close(ln.errChan)
|
||||
return
|
||||
}
|
||||
|
||||
c := ln.getConn(raddr)
|
||||
if c == nil {
|
||||
bufpool.Put(b)
|
||||
continue
|
||||
}
|
||||
|
||||
if err := c.WriteQueue((*b)[:n]); err != nil {
|
||||
ln.logger.Warn("data discarded: ", err)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
func (ln *listener) Addr() net.Addr {
|
||||
return ln.addr
|
||||
}
|
||||
|
||||
func (ln *listener) Close() error {
|
||||
select {
|
||||
case <-ln.closed:
|
||||
default:
|
||||
close(ln.closed)
|
||||
ln.conn.Close()
|
||||
ln.connPool.Close()
|
||||
}
|
||||
|
||||
return nil
|
||||
}
|
||||
|
||||
func (ln *listener) getConn(raddr net.Addr) *Conn {
|
||||
ln.mux.Lock()
|
||||
defer ln.mux.Unlock()
|
||||
|
||||
c, ok := ln.connPool.Get(raddr.String())
|
||||
if ok {
|
||||
return c
|
||||
}
|
||||
|
||||
c = NewConn(ln.conn, ln.addr, raddr, ln.readQueueSize)
|
||||
select {
|
||||
case ln.cqueue <- c:
|
||||
ln.connPool.Set(raddr.String(), c)
|
||||
return c
|
||||
default:
|
||||
c.Close()
|
||||
ln.logger.Warnf("connection queue is full, client %s discarded", raddr)
|
||||
return nil
|
||||
}
|
||||
}
|
||||
@@ -1,100 +0,0 @@
|
||||
package udp
|
||||
|
||||
import (
|
||||
"sync"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type ConnPool struct {
|
||||
m sync.Map
|
||||
ttl time.Duration
|
||||
closed chan struct{}
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func NewConnPool(ttl time.Duration) *ConnPool {
|
||||
p := &ConnPool{
|
||||
ttl: ttl,
|
||||
closed: make(chan struct{}),
|
||||
}
|
||||
go p.idleCheck()
|
||||
return p
|
||||
}
|
||||
|
||||
func (p *ConnPool) WithLogger(logger logger.Logger) *ConnPool {
|
||||
p.logger = logger
|
||||
return p
|
||||
}
|
||||
|
||||
func (p *ConnPool) Get(key interface{}) (c *Conn, ok bool) {
|
||||
v, ok := p.m.Load(key)
|
||||
if ok {
|
||||
c, ok = v.(*Conn)
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (p *ConnPool) Set(key interface{}, c *Conn) {
|
||||
p.m.Store(key, c)
|
||||
}
|
||||
|
||||
func (p *ConnPool) Delete(key interface{}) {
|
||||
p.m.Delete(key)
|
||||
}
|
||||
|
||||
func (p *ConnPool) Close() {
|
||||
select {
|
||||
case <-p.closed:
|
||||
return
|
||||
default:
|
||||
}
|
||||
|
||||
close(p.closed)
|
||||
|
||||
p.m.Range(func(k, v interface{}) bool {
|
||||
if c, ok := v.(*Conn); ok && c != nil {
|
||||
c.Close()
|
||||
}
|
||||
return true
|
||||
})
|
||||
}
|
||||
|
||||
func (p *ConnPool) idleCheck() {
|
||||
ticker := time.NewTicker(p.ttl)
|
||||
defer ticker.Stop()
|
||||
|
||||
for {
|
||||
select {
|
||||
case <-ticker.C:
|
||||
size := 0
|
||||
idles := 0
|
||||
p.m.Range(func(key, value interface{}) bool {
|
||||
c, ok := value.(*Conn)
|
||||
if !ok || c == nil {
|
||||
p.Delete(key)
|
||||
return true
|
||||
}
|
||||
size++
|
||||
|
||||
if c.IsIdle() {
|
||||
idles++
|
||||
p.Delete(key)
|
||||
c.Close()
|
||||
return true
|
||||
}
|
||||
|
||||
c.SetIdle(true)
|
||||
|
||||
return true
|
||||
})
|
||||
|
||||
if idles > 0 {
|
||||
p.logger.Debugf("connection pool: size=%d, idle=%d", size, idles)
|
||||
}
|
||||
case <-p.closed:
|
||||
return
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -1,272 +0,0 @@
|
||||
package config
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"io"
|
||||
"sync"
|
||||
"time"
|
||||
|
||||
"github.com/spf13/viper"
|
||||
"gopkg.in/yaml.v2"
|
||||
)
|
||||
|
||||
var (
|
||||
v = viper.GetViper()
|
||||
)
|
||||
|
||||
func init() {
|
||||
v.SetConfigName("gost")
|
||||
v.AddConfigPath("/etc/gost/")
|
||||
v.AddConfigPath("$HOME/.gost/")
|
||||
v.AddConfigPath(".")
|
||||
}
|
||||
|
||||
var (
|
||||
global = &Config{}
|
||||
globalMux sync.RWMutex
|
||||
)
|
||||
|
||||
func Global() *Config {
|
||||
globalMux.RLock()
|
||||
defer globalMux.RUnlock()
|
||||
|
||||
cfg := &Config{}
|
||||
*cfg = *global
|
||||
return cfg
|
||||
}
|
||||
|
||||
func SetGlobal(c *Config) {
|
||||
globalMux.Lock()
|
||||
defer globalMux.Unlock()
|
||||
|
||||
global = c
|
||||
}
|
||||
|
||||
type LogConfig struct {
|
||||
Output string `yaml:",omitempty" json:"output,omitempty"`
|
||||
Level string `yaml:",omitempty" json:"level,omitempty"`
|
||||
Format string `yaml:",omitempty" json:"format,omitempty"`
|
||||
}
|
||||
|
||||
type ProfilingConfig struct {
|
||||
Addr string `json:"addr"`
|
||||
Enable bool `json:"enable"`
|
||||
}
|
||||
|
||||
type APIConfig struct {
|
||||
Addr string `json:"addr"`
|
||||
PathPrefix string `yaml:"pathPrefix,omitempty" json:"pathPrefix,omitempty"`
|
||||
AccessLog bool `yaml:"accesslog,omitempty" json:"accesslog,omitempty"`
|
||||
Auth *AuthConfig `yaml:",omitempty" json:"auth,omitempty"`
|
||||
Auther string `yaml:",omitempty" json:"auther,omitempty"`
|
||||
}
|
||||
|
||||
type MetricsConfig struct {
|
||||
Enable bool `json:"enable"`
|
||||
Addr string `json:"addr"`
|
||||
Path string `json:"path"`
|
||||
}
|
||||
|
||||
type TLSConfig struct {
|
||||
CertFile string `yaml:"certFile,omitempty" json:"certFile,omitempty"`
|
||||
KeyFile string `yaml:"keyFile,omitempty" json:"keyFile,omitempty"`
|
||||
CAFile string `yaml:"caFile,omitempty" json:"caFile,omitempty"`
|
||||
Secure bool `yaml:",omitempty" json:"secure,omitempty"`
|
||||
ServerName string `yaml:"serverName,omitempty" json:"serverName,omitempty"`
|
||||
}
|
||||
|
||||
type AutherConfig struct {
|
||||
Name string `json:"name"`
|
||||
// inline, file, redis, etc.
|
||||
Type string `yaml:",omitempty" json:"type,omitempty"`
|
||||
Auths []*AuthConfig `yaml:",omitempty" json:"auths"`
|
||||
// File string `yaml:",omitempty" json:"file"`
|
||||
}
|
||||
|
||||
type AuthConfig struct {
|
||||
Username string `json:"username"`
|
||||
Password string `yaml:",omitempty" json:"password,omitempty"`
|
||||
}
|
||||
|
||||
type SelectorConfig struct {
|
||||
Strategy string `json:"strategy"`
|
||||
MaxFails int `yaml:"maxFails" json:"maxFails"`
|
||||
FailTimeout time.Duration `yaml:"failTimeout" json:"failTimeout"`
|
||||
}
|
||||
|
||||
type AdmissionConfig struct {
|
||||
Name string `json:"name"`
|
||||
// inline, file, etc.
|
||||
Type string `yaml:",omitempty" json:"type,omitempty"`
|
||||
Reverse bool `yaml:",omitempty" json:"reverse,omitempty"`
|
||||
Matchers []string `json:"matchers"`
|
||||
}
|
||||
|
||||
type BypassConfig struct {
|
||||
Name string `json:"name"`
|
||||
// inline, file, etc.
|
||||
Type string `yaml:",omitempty" json:"type,omitempty"`
|
||||
Reverse bool `yaml:",omitempty" json:"reverse,omitempty"`
|
||||
Matchers []string `json:"matchers"`
|
||||
}
|
||||
|
||||
type NameserverConfig struct {
|
||||
Addr string `json:"addr"`
|
||||
Chain string `yaml:",omitempty" json:"chain,omitempty"`
|
||||
Prefer string `yaml:",omitempty" json:"prefer,omitempty"`
|
||||
ClientIP string `yaml:"clientIP,omitempty" json:"clientIP,omitempty"`
|
||||
Hostname string `yaml:",omitempty" json:"hostname,omitempty"`
|
||||
TTL time.Duration `yaml:",omitempty" json:"ttl,omitempty"`
|
||||
Timeout time.Duration `yaml:",omitempty" json:"timeout,omitempty"`
|
||||
}
|
||||
|
||||
type ResolverConfig struct {
|
||||
Name string `json:"name"`
|
||||
// inline, file, etc.
|
||||
Type string `yaml:",omitempty" json:"type,omitempty"`
|
||||
Nameservers []*NameserverConfig `json:"nameservers"`
|
||||
}
|
||||
|
||||
type HostMappingConfig struct {
|
||||
IP string `json:"ip"`
|
||||
Hostname string `json:"hostname"`
|
||||
Aliases []string `yaml:",omitempty" json:"aliases,omitempty"`
|
||||
}
|
||||
|
||||
type HostsConfig struct {
|
||||
Name string `json:"name"`
|
||||
// inline, file, etc.
|
||||
Type string `yaml:",omitempty" json:"type,omitempty"`
|
||||
Mappings []*HostMappingConfig `json:"mappings"`
|
||||
}
|
||||
|
||||
type ListenerConfig struct {
|
||||
Type string `json:"type"`
|
||||
Chain string `yaml:",omitempty" json:"chain,omitempty"`
|
||||
Auther string `yaml:",omitempty" json:"auther,omitempty"`
|
||||
Auth *AuthConfig `yaml:",omitempty" json:"auth,omitempty"`
|
||||
TLS *TLSConfig `yaml:",omitempty" json:"tls,omitempty"`
|
||||
Metadata map[string]interface{} `yaml:",omitempty" json:"metadata,omitempty"`
|
||||
}
|
||||
|
||||
type HandlerConfig struct {
|
||||
Type string `json:"type"`
|
||||
Retries int `yaml:",omitempty" json:"retries,omitempty"`
|
||||
Chain string `yaml:",omitempty" json:"chain,omitempty"`
|
||||
Auther string `yaml:",omitempty" json:"auther,omitempty"`
|
||||
Auth *AuthConfig `yaml:",omitempty" json:"auth,omitempty"`
|
||||
TLS *TLSConfig `yaml:",omitempty" json:"tls,omitempty"`
|
||||
Metadata map[string]interface{} `yaml:",omitempty" json:"metadata,omitempty"`
|
||||
}
|
||||
|
||||
type ForwarderConfig struct {
|
||||
Targets []string `json:"targets"`
|
||||
Selector *SelectorConfig `yaml:",omitempty" json:"selector,omitempty"`
|
||||
}
|
||||
|
||||
type DialerConfig struct {
|
||||
Type string `json:"type"`
|
||||
Auth *AuthConfig `yaml:",omitempty" json:"auth,omitempty"`
|
||||
TLS *TLSConfig `yaml:",omitempty" json:"tls,omitempty"`
|
||||
Metadata map[string]interface{} `yaml:",omitempty" json:"metadata,omitempty"`
|
||||
}
|
||||
|
||||
type ConnectorConfig struct {
|
||||
Type string `json:"type"`
|
||||
Auth *AuthConfig `yaml:",omitempty" json:"auth,omitempty"`
|
||||
TLS *TLSConfig `yaml:",omitempty" json:"tls,omitempty"`
|
||||
Metadata map[string]interface{} `yaml:",omitempty" json:"metadata,omitempty"`
|
||||
}
|
||||
|
||||
type ServiceConfig struct {
|
||||
Name string `json:"name"`
|
||||
Addr string `yaml:",omitempty" json:"addr,omitempty"`
|
||||
Admission string `yaml:",omitempty" json:"admission,omitempty"`
|
||||
Bypass string `yaml:",omitempty" json:"bypass,omitempty"`
|
||||
Resolver string `yaml:",omitempty" json:"resolver,omitempty"`
|
||||
Hosts string `yaml:",omitempty" json:"hosts,omitempty"`
|
||||
Handler *HandlerConfig `yaml:",omitempty" json:"handler,omitempty"`
|
||||
Listener *ListenerConfig `yaml:",omitempty" json:"listener,omitempty"`
|
||||
Forwarder *ForwarderConfig `yaml:",omitempty" json:"forwarder,omitempty"`
|
||||
}
|
||||
|
||||
type ChainConfig struct {
|
||||
Name string `json:"name"`
|
||||
Selector *SelectorConfig `yaml:",omitempty" json:"selector,omitempty"`
|
||||
Hops []*HopConfig `json:"hops"`
|
||||
}
|
||||
|
||||
type HopConfig struct {
|
||||
Name string `json:"name"`
|
||||
Selector *SelectorConfig `yaml:",omitempty" json:"selector,omitempty"`
|
||||
Bypass string `yaml:",omitempty" json:"bypass,omitempty"`
|
||||
Resolver string `yaml:",omitempty" json:"resolver,omitempty"`
|
||||
Hosts string `yaml:",omitempty" json:"hosts,omitempty"`
|
||||
Nodes []*NodeConfig `json:"nodes"`
|
||||
}
|
||||
|
||||
type NodeConfig struct {
|
||||
Name string `json:"name"`
|
||||
Addr string `yaml:",omitempty" json:"addr,omitempty"`
|
||||
Bypass string `yaml:",omitempty" json:"bypass,omitempty"`
|
||||
Resolver string `yaml:",omitempty" json:"resolver,omitempty"`
|
||||
Hosts string `yaml:",omitempty" json:"hosts,omitempty"`
|
||||
Connector *ConnectorConfig `yaml:",omitempty" json:"connector,omitempty"`
|
||||
Dialer *DialerConfig `yaml:",omitempty" json:"dialer,omitempty"`
|
||||
}
|
||||
|
||||
type Config struct {
|
||||
Services []*ServiceConfig `json:"services"`
|
||||
Chains []*ChainConfig `yaml:",omitempty" json:"chains,omitempty"`
|
||||
Authers []*AutherConfig `yaml:",omitempty" json:"authers,omitempty"`
|
||||
Admissions []*AdmissionConfig `yaml:",omitempty" json:"admissions,omitempty"`
|
||||
Bypasses []*BypassConfig `yaml:",omitempty" json:"bypasses,omitempty"`
|
||||
Resolvers []*ResolverConfig `yaml:",omitempty" json:"resolvers,omitempty"`
|
||||
Hosts []*HostsConfig `yaml:",omitempty" json:"hosts,omitempty"`
|
||||
TLS *TLSConfig `yaml:",omitempty" json:"tls,omitempty"`
|
||||
Log *LogConfig `yaml:",omitempty" json:"log,omitempty"`
|
||||
Profiling *ProfilingConfig `yaml:",omitempty" json:"profiling,omitempty"`
|
||||
API *APIConfig `yaml:",omitempty" json:"api,omitempty"`
|
||||
Metrics *MetricsConfig `yaml:",omitempty" json:"metrics,omitempty"`
|
||||
}
|
||||
|
||||
func (c *Config) Load() error {
|
||||
if err := v.ReadInConfig(); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
return v.Unmarshal(c)
|
||||
}
|
||||
|
||||
func (c *Config) Read(r io.Reader) error {
|
||||
if err := v.ReadConfig(r); err != nil {
|
||||
return err
|
||||
}
|
||||
|
||||
return v.Unmarshal(c)
|
||||
}
|
||||
|
||||
func (c *Config) ReadFile(file string) error {
|
||||
v.SetConfigFile(file)
|
||||
if err := v.ReadInConfig(); err != nil {
|
||||
return err
|
||||
}
|
||||
return v.Unmarshal(c)
|
||||
}
|
||||
|
||||
func (c *Config) Write(w io.Writer, format string) error {
|
||||
switch format {
|
||||
case "json":
|
||||
enc := json.NewEncoder(w)
|
||||
enc.SetIndent("", " ")
|
||||
enc.Encode(c)
|
||||
return nil
|
||||
case "yaml":
|
||||
fallthrough
|
||||
default:
|
||||
enc := yaml.NewEncoder(w)
|
||||
defer enc.Close()
|
||||
|
||||
return enc.Encode(c)
|
||||
}
|
||||
}
|
||||
@@ -1,132 +0,0 @@
|
||||
package parsing
|
||||
|
||||
import (
|
||||
"github.com/go-gost/gost/pkg/chain"
|
||||
tls_util "github.com/go-gost/gost/pkg/common/util/tls"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/dialer"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func ParseChain(cfg *config.ChainConfig) (chain.Chainer, error) {
|
||||
if cfg == nil {
|
||||
return nil, nil
|
||||
}
|
||||
|
||||
chainLogger := logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "chain",
|
||||
"chain": cfg.Name,
|
||||
})
|
||||
|
||||
c := &chain.Chain{}
|
||||
selector := parseSelector(cfg.Selector)
|
||||
for _, hop := range cfg.Hops {
|
||||
group := &chain.NodeGroup{}
|
||||
for _, v := range hop.Nodes {
|
||||
nodeLogger := chainLogger.WithFields(map[string]interface{}{
|
||||
"kind": "node",
|
||||
"connector": v.Connector.Type,
|
||||
"dialer": v.Dialer.Type,
|
||||
"hop": hop.Name,
|
||||
"node": v.Name,
|
||||
})
|
||||
connectorLogger := nodeLogger.WithFields(map[string]interface{}{
|
||||
"kind": "connector",
|
||||
})
|
||||
|
||||
tlsCfg := v.Connector.TLS
|
||||
if tlsCfg == nil {
|
||||
tlsCfg = &config.TLSConfig{}
|
||||
}
|
||||
tlsConfig, err := tls_util.LoadClientConfig(
|
||||
tlsCfg.CertFile, tlsCfg.KeyFile, tlsCfg.CAFile,
|
||||
tlsCfg.Secure, tlsCfg.ServerName)
|
||||
if err != nil {
|
||||
chainLogger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
cr := registry.GetConnector(v.Connector.Type)(
|
||||
connector.AuthOption(parseAuth(v.Connector.Auth)),
|
||||
connector.TLSConfigOption(tlsConfig),
|
||||
connector.LoggerOption(connectorLogger),
|
||||
)
|
||||
|
||||
if v.Connector.Metadata == nil {
|
||||
v.Connector.Metadata = make(map[string]interface{})
|
||||
}
|
||||
if err := cr.Init(metadata.MapMetadata(v.Connector.Metadata)); err != nil {
|
||||
connectorLogger.Error("init: ", err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
dialerLogger := nodeLogger.WithFields(map[string]interface{}{
|
||||
"kind": "dialer",
|
||||
})
|
||||
|
||||
tlsCfg = v.Dialer.TLS
|
||||
if tlsCfg == nil {
|
||||
tlsCfg = &config.TLSConfig{}
|
||||
}
|
||||
tlsConfig, err = tls_util.LoadClientConfig(
|
||||
tlsCfg.CertFile, tlsCfg.KeyFile, tlsCfg.CAFile,
|
||||
tlsCfg.Secure, tlsCfg.ServerName)
|
||||
if err != nil {
|
||||
chainLogger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
d := registry.GetDialer(v.Dialer.Type)(
|
||||
dialer.AuthOption(parseAuth(v.Dialer.Auth)),
|
||||
dialer.TLSConfigOption(tlsConfig),
|
||||
dialer.LoggerOption(dialerLogger),
|
||||
)
|
||||
|
||||
if v.Dialer.Metadata == nil {
|
||||
v.Dialer.Metadata = make(map[string]interface{})
|
||||
}
|
||||
if err := d.Init(metadata.MapMetadata(v.Dialer.Metadata)); err != nil {
|
||||
dialerLogger.Error("init: ", err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
tr := (&chain.Transport{}).
|
||||
WithConnector(cr).
|
||||
WithDialer(d).
|
||||
WithAddr(v.Addr)
|
||||
|
||||
if v.Bypass == "" {
|
||||
v.Bypass = hop.Bypass
|
||||
}
|
||||
if v.Resolver == "" {
|
||||
v.Resolver = hop.Resolver
|
||||
}
|
||||
if v.Hosts == "" {
|
||||
v.Hosts = hop.Hosts
|
||||
}
|
||||
|
||||
node := &chain.Node{
|
||||
Name: v.Name,
|
||||
Addr: v.Addr,
|
||||
Transport: tr,
|
||||
Bypass: registry.Bypass().Get(v.Bypass),
|
||||
Resolver: registry.Resolver().Get(v.Resolver),
|
||||
Hosts: registry.Hosts().Get(v.Hosts),
|
||||
Marker: &chain.FailMarker{},
|
||||
}
|
||||
group.AddNode(node)
|
||||
}
|
||||
|
||||
sel := selector
|
||||
if s := parseSelector(hop.Selector); s != nil {
|
||||
sel = s
|
||||
}
|
||||
group.WithSelector(sel)
|
||||
c.AddNodeGroup(group)
|
||||
}
|
||||
|
||||
return c, nil
|
||||
}
|
||||
@@ -1,161 +0,0 @@
|
||||
package parsing
|
||||
|
||||
import (
|
||||
"net"
|
||||
"net/url"
|
||||
|
||||
"github.com/go-gost/gost/pkg/admission"
|
||||
"github.com/go-gost/gost/pkg/auth"
|
||||
"github.com/go-gost/gost/pkg/bypass"
|
||||
"github.com/go-gost/gost/pkg/chain"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
hostspkg "github.com/go-gost/gost/pkg/hosts"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/go-gost/gost/pkg/resolver"
|
||||
resolver_impl "github.com/go-gost/gost/pkg/resolver/impl"
|
||||
)
|
||||
|
||||
func ParseAuther(cfg *config.AutherConfig) auth.Authenticator {
|
||||
if cfg == nil {
|
||||
return nil
|
||||
}
|
||||
|
||||
m := make(map[string]string)
|
||||
|
||||
for _, user := range cfg.Auths {
|
||||
if user.Username == "" {
|
||||
continue
|
||||
}
|
||||
m[user.Username] = user.Password
|
||||
}
|
||||
|
||||
if len(m) == 0 {
|
||||
return nil
|
||||
}
|
||||
return auth.NewMapAuthenticator(m)
|
||||
}
|
||||
|
||||
func ParseAutherFromAuth(au *config.AuthConfig) auth.Authenticator {
|
||||
if au == nil || au.Username == "" {
|
||||
return nil
|
||||
}
|
||||
return auth.NewMapAuthenticator(map[string]string{
|
||||
au.Username: au.Password,
|
||||
})
|
||||
}
|
||||
|
||||
func parseAuth(cfg *config.AuthConfig) *url.Userinfo {
|
||||
if cfg == nil || cfg.Username == "" {
|
||||
return nil
|
||||
}
|
||||
|
||||
if cfg.Password == "" {
|
||||
return url.User(cfg.Username)
|
||||
}
|
||||
return url.UserPassword(cfg.Username, cfg.Password)
|
||||
}
|
||||
|
||||
func parseSelector(cfg *config.SelectorConfig) chain.Selector {
|
||||
if cfg == nil {
|
||||
return nil
|
||||
}
|
||||
|
||||
var strategy chain.Strategy
|
||||
switch cfg.Strategy {
|
||||
case "round", "rr":
|
||||
strategy = chain.RoundRobinStrategy()
|
||||
case "random", "rand":
|
||||
strategy = chain.RandomStrategy()
|
||||
case "fifo", "ha":
|
||||
strategy = chain.FIFOStrategy()
|
||||
default:
|
||||
strategy = chain.RoundRobinStrategy()
|
||||
}
|
||||
|
||||
return chain.NewSelector(
|
||||
strategy,
|
||||
chain.InvalidFilter(),
|
||||
chain.FailFilter(cfg.MaxFails, cfg.FailTimeout),
|
||||
)
|
||||
}
|
||||
|
||||
func ParseAdmission(cfg *config.AdmissionConfig) admission.Admission {
|
||||
if cfg == nil {
|
||||
return nil
|
||||
}
|
||||
return admission.NewAdmissionPatterns(
|
||||
cfg.Reverse,
|
||||
cfg.Matchers,
|
||||
admission.LoggerOption(logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "admission",
|
||||
"admission": cfg.Name,
|
||||
})),
|
||||
)
|
||||
}
|
||||
|
||||
func ParseBypass(cfg *config.BypassConfig) bypass.Bypass {
|
||||
if cfg == nil {
|
||||
return nil
|
||||
}
|
||||
return bypass.NewBypassPatterns(
|
||||
cfg.Reverse,
|
||||
cfg.Matchers,
|
||||
bypass.LoggerOption(logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "bypass",
|
||||
"bypass": cfg.Name,
|
||||
})),
|
||||
)
|
||||
}
|
||||
|
||||
func ParseResolver(cfg *config.ResolverConfig) (resolver.Resolver, error) {
|
||||
if cfg == nil {
|
||||
return nil, nil
|
||||
}
|
||||
var nameservers []resolver_impl.NameServer
|
||||
for _, server := range cfg.Nameservers {
|
||||
nameservers = append(nameservers, resolver_impl.NameServer{
|
||||
Addr: server.Addr,
|
||||
Chain: registry.Chain().Get(server.Chain),
|
||||
TTL: server.TTL,
|
||||
Timeout: server.Timeout,
|
||||
ClientIP: net.ParseIP(server.ClientIP),
|
||||
Prefer: server.Prefer,
|
||||
Hostname: server.Hostname,
|
||||
})
|
||||
}
|
||||
|
||||
return resolver_impl.NewResolver(
|
||||
nameservers,
|
||||
resolver_impl.LoggerResolverOption(
|
||||
logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "resolver",
|
||||
"resolver": cfg.Name,
|
||||
}),
|
||||
),
|
||||
)
|
||||
}
|
||||
|
||||
func ParseHosts(cfg *config.HostsConfig) hostspkg.HostMapper {
|
||||
if cfg == nil || len(cfg.Mappings) == 0 {
|
||||
return nil
|
||||
}
|
||||
hosts := hostspkg.NewHosts()
|
||||
hosts.Logger = logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "hosts",
|
||||
"hosts": cfg.Name,
|
||||
})
|
||||
|
||||
for _, host := range cfg.Mappings {
|
||||
if host.IP == "" || host.Hostname == "" {
|
||||
continue
|
||||
}
|
||||
|
||||
ip := net.ParseIP(host.IP)
|
||||
if ip == nil {
|
||||
continue
|
||||
}
|
||||
hosts.Map(ip, host.Hostname, host.Aliases...)
|
||||
}
|
||||
return hosts
|
||||
}
|
||||
@@ -1,140 +0,0 @@
|
||||
package parsing
|
||||
|
||||
import (
|
||||
"strings"
|
||||
|
||||
"github.com/go-gost/gost/pkg/chain"
|
||||
tls_util "github.com/go-gost/gost/pkg/common/util/tls"
|
||||
"github.com/go-gost/gost/pkg/config"
|
||||
"github.com/go-gost/gost/pkg/handler"
|
||||
"github.com/go-gost/gost/pkg/listener"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/go-gost/gost/pkg/service"
|
||||
)
|
||||
|
||||
func ParseService(cfg *config.ServiceConfig) (service.Service, error) {
|
||||
if cfg.Listener == nil {
|
||||
cfg.Listener = &config.ListenerConfig{
|
||||
Type: "tcp",
|
||||
}
|
||||
}
|
||||
if cfg.Handler == nil {
|
||||
cfg.Handler = &config.HandlerConfig{
|
||||
Type: "auto",
|
||||
}
|
||||
}
|
||||
serviceLogger := logger.Default().WithFields(map[string]interface{}{
|
||||
"kind": "service",
|
||||
"service": cfg.Name,
|
||||
"listener": cfg.Listener.Type,
|
||||
"handler": cfg.Handler.Type,
|
||||
})
|
||||
|
||||
listenerLogger := serviceLogger.WithFields(map[string]interface{}{
|
||||
"kind": "listener",
|
||||
})
|
||||
|
||||
tlsCfg := cfg.Listener.TLS
|
||||
if tlsCfg == nil {
|
||||
tlsCfg = &config.TLSConfig{}
|
||||
}
|
||||
tlsConfig, err := tls_util.LoadServerConfig(
|
||||
tlsCfg.CertFile, tlsCfg.KeyFile, tlsCfg.CAFile)
|
||||
if err != nil {
|
||||
listenerLogger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
auther := ParseAutherFromAuth(cfg.Listener.Auth)
|
||||
if cfg.Listener.Auther != "" {
|
||||
auther = registry.Auther().Get(cfg.Listener.Auther)
|
||||
}
|
||||
|
||||
ln := registry.GetListener(cfg.Listener.Type)(
|
||||
listener.AddrOption(cfg.Addr),
|
||||
listener.ChainOption(registry.Chain().Get(cfg.Listener.Chain)),
|
||||
listener.AutherOption(auther),
|
||||
listener.AuthOption(parseAuth(cfg.Listener.Auth)),
|
||||
listener.TLSConfigOption(tlsConfig),
|
||||
listener.LoggerOption(listenerLogger),
|
||||
)
|
||||
|
||||
if cfg.Listener.Metadata == nil {
|
||||
cfg.Listener.Metadata = make(map[string]interface{})
|
||||
}
|
||||
if err := ln.Init(metadata.MapMetadata(cfg.Listener.Metadata)); err != nil {
|
||||
listenerLogger.Error("init: ", err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
handlerLogger := serviceLogger.WithFields(map[string]interface{}{
|
||||
"kind": "handler",
|
||||
})
|
||||
|
||||
tlsCfg = cfg.Handler.TLS
|
||||
if tlsCfg == nil {
|
||||
tlsCfg = &config.TLSConfig{}
|
||||
}
|
||||
tlsConfig, err = tls_util.LoadServerConfig(
|
||||
tlsCfg.CertFile, tlsCfg.KeyFile, tlsCfg.CAFile)
|
||||
if err != nil {
|
||||
handlerLogger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
auther = ParseAutherFromAuth(cfg.Handler.Auth)
|
||||
if cfg.Handler.Auther != "" {
|
||||
auther = registry.Auther().Get(cfg.Handler.Auther)
|
||||
}
|
||||
h := registry.GetHandler(cfg.Handler.Type)(
|
||||
handler.AutherOption(auther),
|
||||
handler.AuthOption(parseAuth(cfg.Handler.Auth)),
|
||||
handler.RetriesOption(cfg.Handler.Retries),
|
||||
handler.ChainOption(registry.Chain().Get(cfg.Handler.Chain)),
|
||||
handler.BypassOption(registry.Bypass().Get(cfg.Bypass)),
|
||||
handler.ResolverOption(registry.Resolver().Get(cfg.Resolver)),
|
||||
handler.HostsOption(registry.Hosts().Get(cfg.Hosts)),
|
||||
handler.TLSConfigOption(tlsConfig),
|
||||
handler.LoggerOption(handlerLogger),
|
||||
)
|
||||
|
||||
if forwarder, ok := h.(handler.Forwarder); ok {
|
||||
forwarder.Forward(parseForwarder(cfg.Forwarder))
|
||||
}
|
||||
|
||||
if cfg.Handler.Metadata == nil {
|
||||
cfg.Handler.Metadata = make(map[string]interface{})
|
||||
}
|
||||
if err := h.Init(metadata.MapMetadata(cfg.Handler.Metadata)); err != nil {
|
||||
handlerLogger.Error("init: ", err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
s := service.NewService(ln, h,
|
||||
service.AdmissionOption(registry.Admission().Get(cfg.Admission)),
|
||||
service.LoggerOption(serviceLogger),
|
||||
)
|
||||
|
||||
serviceLogger.Infof("listening on %s/%s", s.Addr().String(), s.Addr().Network())
|
||||
return s, nil
|
||||
}
|
||||
|
||||
func parseForwarder(cfg *config.ForwarderConfig) *chain.NodeGroup {
|
||||
if cfg == nil || len(cfg.Targets) == 0 {
|
||||
return nil
|
||||
}
|
||||
|
||||
group := &chain.NodeGroup{}
|
||||
for _, target := range cfg.Targets {
|
||||
if v := strings.TrimSpace(target); v != "" {
|
||||
group.AddNode(&chain.Node{
|
||||
Name: target,
|
||||
Addr: target,
|
||||
Marker: &chain.FailMarker{},
|
||||
})
|
||||
}
|
||||
}
|
||||
return group.WithSelector(parseSelector(cfg.Selector))
|
||||
}
|
||||
@@ -1,45 +0,0 @@
|
||||
package connector
|
||||
|
||||
import (
|
||||
"context"
|
||||
"errors"
|
||||
"net"
|
||||
)
|
||||
|
||||
var (
|
||||
ErrBindUnsupported = errors.New("bind unsupported")
|
||||
)
|
||||
|
||||
type Accepter interface {
|
||||
Accept() (net.Conn, error)
|
||||
Addr() net.Addr
|
||||
Close() error
|
||||
}
|
||||
|
||||
type Binder interface {
|
||||
Bind(ctx context.Context, conn net.Conn, network, address string, opts ...BindOption) (net.Listener, error)
|
||||
}
|
||||
|
||||
type AcceptError struct {
|
||||
err error
|
||||
}
|
||||
|
||||
func NewAcceptError(err error) error {
|
||||
return &AcceptError{err: err}
|
||||
}
|
||||
|
||||
func (e *AcceptError) Error() string {
|
||||
return e.err.Error()
|
||||
}
|
||||
|
||||
func (e *AcceptError) Timeout() bool {
|
||||
return false
|
||||
}
|
||||
|
||||
func (e *AcceptError) Temporary() bool {
|
||||
return true
|
||||
}
|
||||
|
||||
func (e *AcceptError) Unwrap() error {
|
||||
return e.err
|
||||
}
|
||||
@@ -1,18 +0,0 @@
|
||||
package connector
|
||||
|
||||
import (
|
||||
"context"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
// Connector is responsible for connecting to the destination address.
|
||||
type Connector interface {
|
||||
Init(metadata.Metadata) error
|
||||
Connect(ctx context.Context, conn net.Conn, network, address string, opts ...ConnectOption) (net.Conn, error)
|
||||
}
|
||||
|
||||
type Handshaker interface {
|
||||
Handshake(ctx context.Context, conn net.Conn) (net.Conn, error)
|
||||
}
|
||||
@@ -1,45 +0,0 @@
|
||||
package forward
|
||||
|
||||
import (
|
||||
"context"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("forward", NewConnector)
|
||||
}
|
||||
|
||||
type forwardConnector struct {
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &forwardConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *forwardConnector) Init(md md.Metadata) (err error) {
|
||||
return nil
|
||||
}
|
||||
|
||||
func (c *forwardConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
@@ -1,129 +0,0 @@
|
||||
package http
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"context"
|
||||
"encoding/base64"
|
||||
"fmt"
|
||||
"net"
|
||||
"net/http"
|
||||
"net/http/httputil"
|
||||
"net/url"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("http", NewConnector)
|
||||
}
|
||||
|
||||
type httpConnector struct {
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &httpConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *httpConnector) Init(md md.Metadata) (err error) {
|
||||
return c.parseMetadata(md)
|
||||
}
|
||||
|
||||
func (c *httpConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"local": conn.LocalAddr().String(),
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
req := &http.Request{
|
||||
Method: http.MethodConnect,
|
||||
URL: &url.URL{Host: address},
|
||||
Host: address,
|
||||
ProtoMajor: 1,
|
||||
ProtoMinor: 1,
|
||||
Header: c.md.header,
|
||||
}
|
||||
|
||||
if req.Header == nil {
|
||||
req.Header = http.Header{}
|
||||
}
|
||||
req.Header.Set("Proxy-Connection", "keep-alive")
|
||||
|
||||
if user := c.options.Auth; user != nil {
|
||||
u := user.Username()
|
||||
p, _ := user.Password()
|
||||
req.Header.Set("Proxy-Authorization",
|
||||
"Basic "+base64.StdEncoding.EncodeToString([]byte(u+":"+p)))
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
if _, ok := conn.(net.PacketConn); ok {
|
||||
err := fmt.Errorf("tcp over udp is unsupported")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
case "udp", "udp4", "udp6":
|
||||
req.Header.Set("X-Gost-Protocol", "udp")
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if log.IsLevelEnabled(logger.DebugLevel) {
|
||||
dump, _ := httputil.DumpRequest(req, false)
|
||||
log.Debug(string(dump))
|
||||
}
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
req = req.WithContext(ctx)
|
||||
if err := req.Write(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
resp, err := http.ReadResponse(bufio.NewReader(conn), req)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
// NOTE: the server may return `Transfer-Encoding: chunked` header,
|
||||
// then the Content-Length of response will be unknown (-1),
|
||||
// in this case, close body will be blocked, so we leave it untouched.
|
||||
// defer resp.Body.Close()
|
||||
|
||||
if log.IsLevelEnabled(logger.DebugLevel) {
|
||||
dump, _ := httputil.DumpResponse(resp, false)
|
||||
log.Debug(string(dump))
|
||||
}
|
||||
|
||||
if resp.StatusCode != http.StatusOK {
|
||||
return nil, fmt.Errorf("%s", resp.Status)
|
||||
}
|
||||
|
||||
if network == "udp" {
|
||||
addr, _ := net.ResolveUDPAddr(network, address)
|
||||
return socks.UDPTunClientConn(conn, addr), nil
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
@@ -1,32 +0,0 @@
|
||||
package http
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
connectTimeout time.Duration
|
||||
header http.Header
|
||||
}
|
||||
|
||||
func (c *httpConnector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
connectTimeout = "timeout"
|
||||
header = "header"
|
||||
)
|
||||
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
|
||||
if mm := mdata.GetStringMapString(md, header); len(mm) > 0 {
|
||||
hd := http.Header{}
|
||||
for k, v := range mm {
|
||||
hd.Add(k, v)
|
||||
}
|
||||
c.md.header = hd
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,54 +0,0 @@
|
||||
package http2
|
||||
|
||||
import (
|
||||
"errors"
|
||||
"io"
|
||||
"net"
|
||||
"time"
|
||||
)
|
||||
|
||||
// HTTP2 connection, wrapped up just like a net.Conn.
|
||||
type http2Conn struct {
|
||||
r io.Reader
|
||||
w io.Writer
|
||||
remoteAddr net.Addr
|
||||
localAddr net.Addr
|
||||
}
|
||||
|
||||
func (c *http2Conn) Read(b []byte) (n int, err error) {
|
||||
return c.r.Read(b)
|
||||
}
|
||||
|
||||
func (c *http2Conn) Write(b []byte) (n int, err error) {
|
||||
return c.w.Write(b)
|
||||
}
|
||||
|
||||
func (c *http2Conn) Close() (err error) {
|
||||
if r, ok := c.r.(io.Closer); ok {
|
||||
err = r.Close()
|
||||
}
|
||||
if w, ok := c.w.(io.Closer); ok {
|
||||
err = w.Close()
|
||||
}
|
||||
return
|
||||
}
|
||||
|
||||
func (c *http2Conn) LocalAddr() net.Addr {
|
||||
return c.localAddr
|
||||
}
|
||||
|
||||
func (c *http2Conn) RemoteAddr() net.Addr {
|
||||
return c.remoteAddr
|
||||
}
|
||||
|
||||
func (c *http2Conn) SetDeadline(t time.Time) error {
|
||||
return &net.OpError{Op: "set", Net: "http2", Source: nil, Addr: nil, Err: errors.New("deadline not supported")}
|
||||
}
|
||||
|
||||
func (c *http2Conn) SetReadDeadline(t time.Time) error {
|
||||
return &net.OpError{Op: "set", Net: "http2", Source: nil, Addr: nil, Err: errors.New("deadline not supported")}
|
||||
}
|
||||
|
||||
func (c *http2Conn) SetWriteDeadline(t time.Time) error {
|
||||
return &net.OpError{Op: "set", Net: "http2", Source: nil, Addr: nil, Err: errors.New("deadline not supported")}
|
||||
}
|
||||
@@ -1,121 +0,0 @@
|
||||
package http2
|
||||
|
||||
import (
|
||||
"context"
|
||||
"encoding/base64"
|
||||
"errors"
|
||||
"fmt"
|
||||
"io"
|
||||
"net"
|
||||
"net/http"
|
||||
"net/http/httputil"
|
||||
"net/url"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
http2_util "github.com/go-gost/gost/pkg/internal/util/http2"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("http2", NewConnector)
|
||||
}
|
||||
|
||||
type http2Connector struct {
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &http2Connector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *http2Connector) Init(md md.Metadata) (err error) {
|
||||
return c.parseMetadata(md)
|
||||
}
|
||||
|
||||
func (c *http2Connector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"local": conn.LocalAddr().String(),
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
cc, ok := conn.(*http2_util.ClientConn)
|
||||
if !ok {
|
||||
err := errors.New("wrong connection type")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
pr, pw := io.Pipe()
|
||||
req := &http.Request{
|
||||
Method: http.MethodConnect,
|
||||
URL: &url.URL{Scheme: "https", Host: conn.RemoteAddr().String()},
|
||||
Host: address,
|
||||
ProtoMajor: 2,
|
||||
ProtoMinor: 0,
|
||||
Header: make(http.Header),
|
||||
Body: pr,
|
||||
// ContentLength: -1,
|
||||
}
|
||||
if c.md.UserAgent != "" {
|
||||
req.Header.Set("User-Agent", c.md.UserAgent)
|
||||
}
|
||||
|
||||
if user := c.options.Auth; user != nil {
|
||||
u := user.Username()
|
||||
p, _ := user.Password()
|
||||
req.Header.Set("Proxy-Authorization",
|
||||
"Basic "+base64.StdEncoding.EncodeToString([]byte(u+":"+p)))
|
||||
}
|
||||
|
||||
if log.IsLevelEnabled(logger.DebugLevel) {
|
||||
dump, _ := httputil.DumpRequest(req, false)
|
||||
log.Debug(string(dump))
|
||||
}
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
resp, err := cc.Client().Do(req.WithContext(ctx))
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
cc.Close()
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if log.IsLevelEnabled(logger.DebugLevel) {
|
||||
dump, _ := httputil.DumpResponse(resp, false)
|
||||
log.Debug(string(dump))
|
||||
}
|
||||
if resp.StatusCode != http.StatusOK {
|
||||
resp.Body.Close()
|
||||
err = fmt.Errorf("%s", resp.Status)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
hc := &http2Conn{
|
||||
r: resp.Body,
|
||||
w: pw,
|
||||
localAddr: conn.RemoteAddr(),
|
||||
}
|
||||
|
||||
hc.remoteAddr, _ = net.ResolveTCPAddr(network, address)
|
||||
|
||||
return hc, nil
|
||||
}
|
||||
@@ -1,31 +0,0 @@
|
||||
package http2
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
const (
|
||||
defaultUserAgent = "Chrome/78.0.3904.106"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
connectTimeout time.Duration
|
||||
UserAgent string
|
||||
}
|
||||
|
||||
func (c *http2Connector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
connectTimeout = "timeout"
|
||||
userAgent = "userAgent"
|
||||
)
|
||||
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
c.md.UserAgent = mdata.GetString(md, userAgent)
|
||||
if c.md.UserAgent == "" {
|
||||
c.md.UserAgent = defaultUserAgent
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,80 +0,0 @@
|
||||
package connector
|
||||
|
||||
import (
|
||||
"crypto/tls"
|
||||
"net/url"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type Options struct {
|
||||
Auth *url.Userinfo
|
||||
TLSConfig *tls.Config
|
||||
Logger logger.Logger
|
||||
}
|
||||
|
||||
type Option func(opts *Options)
|
||||
|
||||
func AuthOption(auth *url.Userinfo) Option {
|
||||
return func(opts *Options) {
|
||||
opts.Auth = auth
|
||||
}
|
||||
}
|
||||
|
||||
func TLSConfigOption(tlsConfig *tls.Config) Option {
|
||||
return func(opts *Options) {
|
||||
opts.TLSConfig = tlsConfig
|
||||
}
|
||||
}
|
||||
|
||||
func LoggerOption(logger logger.Logger) Option {
|
||||
return func(opts *Options) {
|
||||
opts.Logger = logger
|
||||
}
|
||||
}
|
||||
|
||||
type ConnectOptions struct {
|
||||
}
|
||||
|
||||
type ConnectOption func(opts *ConnectOptions)
|
||||
|
||||
type BindOptions struct {
|
||||
Mux bool
|
||||
Backlog int
|
||||
UDPDataQueueSize int
|
||||
UDPDataBufferSize int
|
||||
UDPConnTTL time.Duration
|
||||
}
|
||||
|
||||
type BindOption func(opts *BindOptions)
|
||||
|
||||
func MuxBindOption(mux bool) BindOption {
|
||||
return func(opts *BindOptions) {
|
||||
opts.Mux = mux
|
||||
}
|
||||
}
|
||||
|
||||
func BacklogBindOption(backlog int) BindOption {
|
||||
return func(opts *BindOptions) {
|
||||
opts.Backlog = backlog
|
||||
}
|
||||
}
|
||||
|
||||
func UDPDataQueueSizeBindOption(size int) BindOption {
|
||||
return func(opts *BindOptions) {
|
||||
opts.UDPDataQueueSize = size
|
||||
}
|
||||
}
|
||||
|
||||
func UDPDataBufferSizeBindOption(size int) BindOption {
|
||||
return func(opts *BindOptions) {
|
||||
opts.UDPDataBufferSize = size
|
||||
}
|
||||
}
|
||||
|
||||
func UDPConnTTLBindOption(ttl time.Duration) BindOption {
|
||||
return func(opts *BindOptions) {
|
||||
opts.UDPConnTTL = ttl
|
||||
}
|
||||
}
|
||||
@@ -1,133 +0,0 @@
|
||||
package relay
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
"strconv"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/mux"
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/common/util/udp"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/relay"
|
||||
)
|
||||
|
||||
// Bind implements connector.Binder.
|
||||
func (c *relayConnector) Bind(ctx context.Context, conn net.Conn, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("bind on %s/%s", address, network)
|
||||
|
||||
options := connector.BindOptions{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
return c.bindTCP(ctx, conn, network, address, log)
|
||||
case "udp", "udp4", "udp6":
|
||||
return c.bindUDP(ctx, conn, network, address, &options, log)
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
|
||||
func (c *relayConnector) bindTCP(ctx context.Context, conn net.Conn, network, address string, log logger.Logger) (net.Listener, error) {
|
||||
laddr, err := c.bind(conn, relay.BIND, network, address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
log.Debugf("bind on %s/%s OK", laddr, laddr.Network())
|
||||
|
||||
session, err := mux.ServerSession(conn)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &tcpListener{
|
||||
addr: laddr,
|
||||
session: session,
|
||||
logger: log,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (c *relayConnector) bindUDP(ctx context.Context, conn net.Conn, network, address string, opts *connector.BindOptions, log logger.Logger) (net.Listener, error) {
|
||||
laddr, err := c.bind(conn, relay.FUDP|relay.BIND, network, address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
log.Debugf("bind on %s/%s OK", laddr, laddr.Network())
|
||||
|
||||
ln := udp.NewListener(
|
||||
socks.UDPTunClientPacketConn(conn),
|
||||
laddr,
|
||||
opts.Backlog,
|
||||
opts.UDPDataQueueSize, opts.UDPDataBufferSize,
|
||||
opts.UDPConnTTL,
|
||||
log)
|
||||
|
||||
return ln, nil
|
||||
}
|
||||
|
||||
func (c *relayConnector) bind(conn net.Conn, cmd uint8, network, address string) (net.Addr, error) {
|
||||
req := relay.Request{
|
||||
Version: relay.Version1,
|
||||
Flags: cmd,
|
||||
}
|
||||
|
||||
if c.options.Auth != nil {
|
||||
pwd, _ := c.options.Auth.Password()
|
||||
req.Features = append(req.Features, &relay.UserAuthFeature{
|
||||
Username: c.options.Auth.Username(),
|
||||
Password: pwd,
|
||||
})
|
||||
}
|
||||
fa := &relay.AddrFeature{}
|
||||
fa.ParseFrom(address)
|
||||
req.Features = append(req.Features, fa)
|
||||
if _, err := req.WriteTo(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
// first reply, bind status
|
||||
resp := relay.Response{}
|
||||
if _, err := resp.ReadFrom(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if resp.Status != relay.StatusOK {
|
||||
return nil, fmt.Errorf("bind on %s/%s failed", address, network)
|
||||
}
|
||||
|
||||
var addr string
|
||||
for _, f := range resp.Features {
|
||||
if f.Type() == relay.FeatureAddr {
|
||||
if fa, ok := f.(*relay.AddrFeature); ok {
|
||||
addr = net.JoinHostPort(fa.Host, strconv.Itoa(int(fa.Port)))
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
var baddr net.Addr
|
||||
var err error
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
baddr, err = net.ResolveTCPAddr(network, addr)
|
||||
case "udp", "udp4", "udp6":
|
||||
baddr, err = net.ResolveUDPAddr(network, addr)
|
||||
default:
|
||||
err = fmt.Errorf("unknown network %s", network)
|
||||
}
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return baddr, nil
|
||||
}
|
||||
@@ -1,132 +0,0 @@
|
||||
package relay
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"encoding/binary"
|
||||
"errors"
|
||||
"fmt"
|
||||
"io"
|
||||
"math"
|
||||
"net"
|
||||
"sync"
|
||||
|
||||
"github.com/go-gost/relay"
|
||||
)
|
||||
|
||||
type tcpConn struct {
|
||||
net.Conn
|
||||
wbuf bytes.Buffer
|
||||
once sync.Once
|
||||
}
|
||||
|
||||
func (c *tcpConn) Read(b []byte) (n int, err error) {
|
||||
c.once.Do(func() {
|
||||
err = readResponse(c.Conn)
|
||||
})
|
||||
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
return c.Conn.Read(b)
|
||||
}
|
||||
|
||||
func (c *tcpConn) Write(b []byte) (n int, err error) {
|
||||
n = len(b) // force byte length consistent
|
||||
if c.wbuf.Len() > 0 {
|
||||
c.wbuf.Write(b) // append the data to the cached header
|
||||
_, err = c.Conn.Write(c.wbuf.Bytes())
|
||||
c.wbuf.Reset()
|
||||
return
|
||||
}
|
||||
_, err = c.Conn.Write(b)
|
||||
return
|
||||
}
|
||||
|
||||
type udpConn struct {
|
||||
net.Conn
|
||||
wbuf bytes.Buffer
|
||||
once sync.Once
|
||||
}
|
||||
|
||||
func (c *udpConn) Read(b []byte) (n int, err error) {
|
||||
c.once.Do(func() {
|
||||
err = readResponse(c.Conn)
|
||||
})
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
var bb [2]byte
|
||||
_, err = io.ReadFull(c.Conn, bb[:])
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
dlen := int(binary.BigEndian.Uint16(bb[:]))
|
||||
if len(b) >= dlen {
|
||||
return io.ReadFull(c.Conn, b[:dlen])
|
||||
}
|
||||
buf := make([]byte, dlen)
|
||||
_, err = io.ReadFull(c.Conn, buf)
|
||||
n = copy(b, buf)
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *udpConn) Write(b []byte) (n int, err error) {
|
||||
if len(b) > math.MaxUint16 {
|
||||
err = errors.New("write: data maximum exceeded")
|
||||
return
|
||||
}
|
||||
|
||||
n = len(b)
|
||||
if c.wbuf.Len() > 0 {
|
||||
var bb [2]byte
|
||||
binary.BigEndian.PutUint16(bb[:], uint16(len(b)))
|
||||
c.wbuf.Write(bb[:])
|
||||
c.wbuf.Write(b) // append the data to the cached header
|
||||
_, err = c.wbuf.WriteTo(c.Conn)
|
||||
return
|
||||
}
|
||||
|
||||
var bb [2]byte
|
||||
binary.BigEndian.PutUint16(bb[:], uint16(len(b)))
|
||||
_, err = c.Conn.Write(bb[:])
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
return c.Conn.Write(b)
|
||||
}
|
||||
|
||||
func readResponse(r io.Reader) (err error) {
|
||||
resp := relay.Response{}
|
||||
_, err = resp.ReadFrom(r)
|
||||
if err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
if resp.Version != relay.Version1 {
|
||||
err = relay.ErrBadVersion
|
||||
return
|
||||
}
|
||||
|
||||
if resp.Status != relay.StatusOK {
|
||||
err = fmt.Errorf("status %d", resp.Status)
|
||||
return
|
||||
}
|
||||
return nil
|
||||
}
|
||||
|
||||
type bindConn struct {
|
||||
net.Conn
|
||||
localAddr net.Addr
|
||||
remoteAddr net.Addr
|
||||
}
|
||||
|
||||
func (c *bindConn) LocalAddr() net.Addr {
|
||||
return c.localAddr
|
||||
}
|
||||
|
||||
func (c *bindConn) RemoteAddr() net.Addr {
|
||||
return c.remoteAddr
|
||||
}
|
||||
@@ -1,127 +0,0 @@
|
||||
package relay
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/go-gost/relay"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("relay", NewConnector)
|
||||
}
|
||||
|
||||
type relayConnector struct {
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &relayConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *relayConnector) Init(md md.Metadata) (err error) {
|
||||
return c.parseMetadata(md)
|
||||
}
|
||||
|
||||
func (c *relayConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
req := relay.Request{
|
||||
Version: relay.Version1,
|
||||
Flags: relay.CONNECT,
|
||||
}
|
||||
if network == "udp" || network == "udp4" || network == "udp6" {
|
||||
req.Flags |= relay.FUDP
|
||||
|
||||
// UDP association
|
||||
if address == "" {
|
||||
baddr, err := c.bind(conn, relay.FUDP|relay.BIND, network, address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
log.Debugf("associate on %s OK", baddr)
|
||||
|
||||
return socks.UDPTunClientConn(conn, nil), nil
|
||||
}
|
||||
}
|
||||
|
||||
if c.options.Auth != nil {
|
||||
pwd, _ := c.options.Auth.Password()
|
||||
req.Features = append(req.Features, &relay.UserAuthFeature{
|
||||
Username: c.options.Auth.Username(),
|
||||
Password: pwd,
|
||||
})
|
||||
}
|
||||
|
||||
if address != "" {
|
||||
af := &relay.AddrFeature{}
|
||||
if err := af.ParseFrom(address); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
// forward mode if port is 0.
|
||||
if af.Port > 0 {
|
||||
req.Features = append(req.Features, af)
|
||||
}
|
||||
}
|
||||
|
||||
if c.md.noDelay {
|
||||
if _, err := req.WriteTo(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
cc := &tcpConn{
|
||||
Conn: conn,
|
||||
}
|
||||
if !c.md.noDelay {
|
||||
if _, err := req.WriteTo(&cc.wbuf); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
conn = cc
|
||||
case "udp", "udp4", "udp6":
|
||||
cc := &udpConn{
|
||||
Conn: conn,
|
||||
}
|
||||
if !c.md.noDelay {
|
||||
if _, err := req.WriteTo(&cc.wbuf); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
conn = cc
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
@@ -1,73 +0,0 @@
|
||||
package relay
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"net"
|
||||
"strconv"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/mux"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
"github.com/go-gost/relay"
|
||||
)
|
||||
|
||||
type tcpListener struct {
|
||||
addr net.Addr
|
||||
session *mux.Session
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func (p *tcpListener) Accept() (net.Conn, error) {
|
||||
cc, err := p.session.Accept()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
conn, err := p.getPeerConn(cc)
|
||||
if err != nil {
|
||||
cc.Close()
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
|
||||
func (p *tcpListener) getPeerConn(conn net.Conn) (net.Conn, error) {
|
||||
// second reply, peer connected
|
||||
resp := relay.Response{}
|
||||
if _, err := resp.ReadFrom(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if resp.Status != relay.StatusOK {
|
||||
err := fmt.Errorf("peer connect failed")
|
||||
return nil, err
|
||||
}
|
||||
|
||||
var address string
|
||||
for _, f := range resp.Features {
|
||||
if f.Type() == relay.FeatureAddr {
|
||||
if fa, ok := f.(*relay.AddrFeature); ok {
|
||||
address = net.JoinHostPort(fa.Host, strconv.Itoa(int(fa.Port)))
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
raddr, err := net.ResolveTCPAddr("tcp", address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &bindConn{
|
||||
Conn: conn,
|
||||
localAddr: p.addr,
|
||||
remoteAddr: raddr,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (p *tcpListener) Addr() net.Addr {
|
||||
return p.addr
|
||||
}
|
||||
|
||||
func (p *tcpListener) Close() error {
|
||||
return p.session.Close()
|
||||
}
|
||||
@@ -1,24 +0,0 @@
|
||||
package relay
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
connectTimeout time.Duration
|
||||
noDelay bool
|
||||
}
|
||||
|
||||
func (c *relayConnector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
connectTimeout = "connectTimeout"
|
||||
noDelay = "nodelay"
|
||||
)
|
||||
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
c.md.noDelay = mdata.GetBool(md, noDelay)
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,128 +0,0 @@
|
||||
package sni
|
||||
|
||||
import (
|
||||
"bufio"
|
||||
"bytes"
|
||||
"encoding/base64"
|
||||
"encoding/binary"
|
||||
"hash/crc32"
|
||||
"io"
|
||||
"net"
|
||||
"strings"
|
||||
|
||||
dissector "github.com/go-gost/tls-dissector"
|
||||
)
|
||||
|
||||
type sniClientConn struct {
|
||||
host string
|
||||
obfuscated bool
|
||||
net.Conn
|
||||
}
|
||||
|
||||
func (c *sniClientConn) Write(p []byte) (int, error) {
|
||||
b, err := c.obfuscate(p)
|
||||
if err != nil {
|
||||
return 0, err
|
||||
}
|
||||
if _, err = c.Conn.Write(b); err != nil {
|
||||
return 0, err
|
||||
}
|
||||
return len(p), nil
|
||||
}
|
||||
|
||||
func (c *sniClientConn) obfuscate(p []byte) ([]byte, error) {
|
||||
if c.host == "" {
|
||||
return p, nil
|
||||
}
|
||||
|
||||
if c.obfuscated {
|
||||
return p, nil
|
||||
}
|
||||
|
||||
if p[0] == dissector.Handshake {
|
||||
b, err := readClientHelloRecord(bytes.NewReader(p), c.host)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
c.obfuscated = true
|
||||
return b, nil
|
||||
}
|
||||
|
||||
buf := &bytes.Buffer{}
|
||||
br := bufio.NewReader(bytes.NewReader(p))
|
||||
for {
|
||||
s, err := br.ReadString('\n')
|
||||
if err != nil {
|
||||
if err != io.EOF {
|
||||
return nil, err
|
||||
}
|
||||
if s != "" {
|
||||
buf.Write([]byte(s))
|
||||
}
|
||||
break
|
||||
}
|
||||
|
||||
// end of HTTP header
|
||||
if s == "\r\n" {
|
||||
buf.Write([]byte(s))
|
||||
// drain the remain bytes.
|
||||
io.Copy(buf, br)
|
||||
break
|
||||
}
|
||||
|
||||
if strings.HasPrefix(s, "Host") {
|
||||
s = strings.TrimSpace(strings.TrimSuffix(strings.TrimPrefix(s, "Host:"), "\r\n"))
|
||||
host := encodeServerName(s)
|
||||
buf.WriteString("Host: " + c.host + "\r\n")
|
||||
buf.WriteString("Gost-Target: " + host + "\r\n")
|
||||
// drain the remain bytes.
|
||||
io.Copy(buf, br)
|
||||
break
|
||||
}
|
||||
buf.Write([]byte(s))
|
||||
}
|
||||
c.obfuscated = true
|
||||
return buf.Bytes(), nil
|
||||
}
|
||||
|
||||
func readClientHelloRecord(r io.Reader, host string) ([]byte, error) {
|
||||
record, err := dissector.ReadRecord(r)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
clientHello := dissector.ClientHelloMsg{}
|
||||
if err := clientHello.Decode(record.Opaque); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
for _, ext := range clientHello.Extensions {
|
||||
if ext.Type() == dissector.ExtServerName {
|
||||
snExtension := ext.(*dissector.ServerNameExtension)
|
||||
if host != "" {
|
||||
e, _ := dissector.NewExtension(0xFFFE, []byte(encodeServerName(snExtension.Name)))
|
||||
clientHello.Extensions = append(clientHello.Extensions, e)
|
||||
snExtension.Name = host
|
||||
}
|
||||
|
||||
break
|
||||
}
|
||||
}
|
||||
record.Opaque, err = clientHello.Encode()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
buf := &bytes.Buffer{}
|
||||
if _, err := record.WriteTo(buf); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return buf.Bytes(), nil
|
||||
}
|
||||
|
||||
func encodeServerName(name string) string {
|
||||
buf := &bytes.Buffer{}
|
||||
binary.Write(buf, binary.BigEndian, crc32.ChecksumIEEE([]byte(name)))
|
||||
buf.WriteString(base64.RawURLEncoding.EncodeToString([]byte(name)))
|
||||
return base64.RawURLEncoding.EncodeToString(buf.Bytes())
|
||||
}
|
||||
@@ -1,46 +0,0 @@
|
||||
package sni
|
||||
|
||||
import (
|
||||
"context"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("sni", NewConnector)
|
||||
}
|
||||
|
||||
type sniConnector struct {
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &sniConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *sniConnector) Init(md md.Metadata) (err error) {
|
||||
return c.parseMetadata(md)
|
||||
}
|
||||
|
||||
func (c *sniConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
return &sniClientConn{Conn: conn, host: c.md.host}, nil
|
||||
}
|
||||
@@ -1,24 +0,0 @@
|
||||
package sni
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
host string
|
||||
connectTimeout time.Duration
|
||||
}
|
||||
|
||||
func (c *sniConnector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
host = "host"
|
||||
connectTimeout = "timeout"
|
||||
)
|
||||
|
||||
c.md.host = mdata.GetString(md, host)
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,123 +0,0 @@
|
||||
package v4
|
||||
|
||||
import (
|
||||
"context"
|
||||
"errors"
|
||||
"fmt"
|
||||
"net"
|
||||
"strconv"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gosocks4"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("socks4", NewConnector)
|
||||
registry.RegiserConnector("socks4a", NewConnector)
|
||||
}
|
||||
|
||||
type socks4Connector struct {
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &socks4Connector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *socks4Connector) Init(md md.Metadata) (err error) {
|
||||
return c.parseMetadata(md)
|
||||
}
|
||||
|
||||
func (c *socks4Connector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
if _, ok := conn.(net.PacketConn); ok {
|
||||
err := fmt.Errorf("tcp over udp is unsupported")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
var addr *gosocks4.Addr
|
||||
|
||||
if c.md.disable4a {
|
||||
taddr, err := net.ResolveTCPAddr("tcp4", address)
|
||||
if err != nil {
|
||||
log.Error("resolve: ", err)
|
||||
return nil, err
|
||||
}
|
||||
if len(taddr.IP) == 0 {
|
||||
taddr.IP = net.IPv4zero
|
||||
}
|
||||
addr = &gosocks4.Addr{
|
||||
Type: gosocks4.AddrIPv4,
|
||||
Host: taddr.IP.String(),
|
||||
Port: uint16(taddr.Port),
|
||||
}
|
||||
} else {
|
||||
host, port, err := net.SplitHostPort(address)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
p, _ := strconv.Atoi(port)
|
||||
addr = &gosocks4.Addr{
|
||||
Type: gosocks4.AddrDomain,
|
||||
Host: host,
|
||||
Port: uint16(p),
|
||||
}
|
||||
}
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
var userid []byte
|
||||
if c.options.Auth != nil {
|
||||
userid = []byte(c.options.Auth.Username())
|
||||
}
|
||||
req := gosocks4.NewRequest(gosocks4.CmdConnect, addr, userid)
|
||||
if err := req.Write(conn); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(req)
|
||||
|
||||
reply, err := gosocks4.ReadReply(conn)
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(reply)
|
||||
|
||||
if reply.Code != gosocks4.Granted {
|
||||
err = errors.New("host unreachable")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
@@ -1,24 +0,0 @@
|
||||
package v4
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
connectTimeout time.Duration
|
||||
disable4a bool
|
||||
}
|
||||
|
||||
func (c *socks4Connector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
connectTimeout = "timeout"
|
||||
disable4a = "disable4a"
|
||||
)
|
||||
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
c.md.disable4a = mdata.GetBool(md, disable4a)
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,130 +0,0 @@
|
||||
package v5
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/util/mux"
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/common/util/udp"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
// Bind implements connector.Binder.
|
||||
func (c *socks5Connector) Bind(ctx context.Context, conn net.Conn, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("bind on %s/%s", address, network)
|
||||
|
||||
options := connector.BindOptions{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
if options.Mux {
|
||||
return c.muxBindTCP(ctx, conn, network, address, log)
|
||||
}
|
||||
return c.bindTCP(ctx, conn, network, address, log)
|
||||
case "udp", "udp4", "udp6":
|
||||
return c.bindUDP(ctx, conn, network, address, &options, log)
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
}
|
||||
|
||||
func (c *socks5Connector) bindTCP(ctx context.Context, conn net.Conn, network, address string, log logger.Logger) (net.Listener, error) {
|
||||
laddr, err := c.bind(conn, gosocks5.CmdBind, network, address, log)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &tcpListener{
|
||||
addr: laddr,
|
||||
conn: conn,
|
||||
logger: log,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (c *socks5Connector) muxBindTCP(ctx context.Context, conn net.Conn, network, address string, log logger.Logger) (net.Listener, error) {
|
||||
laddr, err := c.bind(conn, socks.CmdMuxBind, network, address, log)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
session, err := mux.ServerSession(conn)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &tcpMuxListener{
|
||||
addr: laddr,
|
||||
session: session,
|
||||
logger: log,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (c *socks5Connector) bindUDP(ctx context.Context, conn net.Conn, network, address string, opts *connector.BindOptions, log logger.Logger) (net.Listener, error) {
|
||||
laddr, err := c.bind(conn, socks.CmdUDPTun, network, address, log)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
ln := udp.NewListener(
|
||||
socks.UDPTunClientPacketConn(conn),
|
||||
laddr,
|
||||
opts.Backlog,
|
||||
opts.UDPDataQueueSize, opts.UDPDataBufferSize,
|
||||
opts.UDPConnTTL,
|
||||
log)
|
||||
|
||||
return ln, nil
|
||||
}
|
||||
|
||||
func (l *socks5Connector) bind(conn net.Conn, cmd uint8, network, address string, log logger.Logger) (net.Addr, error) {
|
||||
addr := gosocks5.Addr{}
|
||||
addr.ParseFrom(address)
|
||||
req := gosocks5.NewRequest(cmd, &addr)
|
||||
if err := req.Write(conn); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(req)
|
||||
|
||||
// first reply, bind status
|
||||
reply, err := gosocks5.ReadReply(conn)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
log.Debug(reply)
|
||||
|
||||
if reply.Rep != gosocks5.Succeeded {
|
||||
return nil, fmt.Errorf("bind on %s/%s failed", address, network)
|
||||
}
|
||||
|
||||
var baddr net.Addr
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
baddr, err = net.ResolveTCPAddr(network, reply.Addr.String())
|
||||
case "udp", "udp4", "udp6":
|
||||
baddr, err = net.ResolveUDPAddr(network, reply.Addr.String())
|
||||
default:
|
||||
err = fmt.Errorf("unknown network %s", network)
|
||||
}
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
log.Debugf("bind on %s/%s OK", baddr, baddr.Network())
|
||||
|
||||
return baddr, nil
|
||||
}
|
||||
@@ -1,17 +0,0 @@
|
||||
package v5
|
||||
|
||||
import "net"
|
||||
|
||||
type bindConn struct {
|
||||
net.Conn
|
||||
localAddr net.Addr
|
||||
remoteAddr net.Addr
|
||||
}
|
||||
|
||||
func (c *bindConn) LocalAddr() net.Addr {
|
||||
return c.localAddr
|
||||
}
|
||||
|
||||
func (c *bindConn) RemoteAddr() net.Addr {
|
||||
return c.remoteAddr
|
||||
}
|
||||
@@ -1,173 +0,0 @@
|
||||
package v5
|
||||
|
||||
import (
|
||||
"context"
|
||||
"crypto/tls"
|
||||
"errors"
|
||||
"fmt"
|
||||
"net"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("socks5", NewConnector)
|
||||
registry.RegiserConnector("socks", NewConnector)
|
||||
}
|
||||
|
||||
type socks5Connector struct {
|
||||
selector gosocks5.Selector
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &socks5Connector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *socks5Connector) Init(md md.Metadata) (err error) {
|
||||
if err = c.parseMetadata(md); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
selector := &clientSelector{
|
||||
methods: []uint8{
|
||||
gosocks5.MethodNoAuth,
|
||||
gosocks5.MethodUserPass,
|
||||
},
|
||||
User: c.options.Auth,
|
||||
TLSConfig: c.options.TLSConfig,
|
||||
logger: c.options.Logger,
|
||||
}
|
||||
if !c.md.noTLS {
|
||||
selector.methods = append(selector.methods, socks.MethodTLS)
|
||||
if selector.TLSConfig == nil {
|
||||
selector.TLSConfig = &tls.Config{
|
||||
InsecureSkipVerify: true,
|
||||
}
|
||||
}
|
||||
}
|
||||
c.selector = selector
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
// Handshake implements connector.Handshaker.
|
||||
func (c *socks5Connector) Handshake(ctx context.Context, conn net.Conn) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
})
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
cc := gosocks5.ClientConn(conn, c.selector)
|
||||
if err := cc.Handleshake(); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return cc, nil
|
||||
}
|
||||
|
||||
func (c *socks5Connector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
switch network {
|
||||
case "udp", "udp4", "udp6":
|
||||
return c.connectUDP(ctx, conn, network, address, log)
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
if _, ok := conn.(net.PacketConn); ok {
|
||||
err := fmt.Errorf("tcp over udp is unsupported")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
addr := gosocks5.Addr{}
|
||||
if err := addr.ParseFrom(address); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
req := gosocks5.NewRequest(gosocks5.CmdConnect, &addr)
|
||||
if err := req.Write(conn); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(req)
|
||||
|
||||
reply, err := gosocks5.ReadReply(conn)
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(reply)
|
||||
|
||||
if reply.Rep != gosocks5.Succeeded {
|
||||
err = errors.New("host unreachable")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
|
||||
func (c *socks5Connector) connectUDP(ctx context.Context, conn net.Conn, network, address string, log logger.Logger) (net.Conn, error) {
|
||||
addr, err := net.ResolveUDPAddr(network, address)
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
req := gosocks5.NewRequest(socks.CmdUDPTun, nil)
|
||||
if err := req.Write(conn); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(req)
|
||||
|
||||
reply, err := gosocks5.ReadReply(conn)
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
log.Debug(reply)
|
||||
|
||||
if reply.Rep != gosocks5.Succeeded {
|
||||
return nil, errors.New("get socks5 UDP tunnel failure")
|
||||
}
|
||||
|
||||
return socks.UDPTunClientConn(conn, addr), nil
|
||||
}
|
||||
@@ -1,102 +0,0 @@
|
||||
package v5
|
||||
|
||||
import (
|
||||
"fmt"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/util/mux"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type tcpListener struct {
|
||||
addr net.Addr
|
||||
conn net.Conn
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func (p *tcpListener) Accept() (net.Conn, error) {
|
||||
// second reply, peer connected
|
||||
rep, err := gosocks5.ReadReply(p.conn)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
p.logger.Debug(rep)
|
||||
|
||||
if rep.Rep != gosocks5.Succeeded {
|
||||
return nil, fmt.Errorf("peer connect failed")
|
||||
}
|
||||
|
||||
raddr, err := net.ResolveTCPAddr("tcp", rep.Addr.String())
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &bindConn{
|
||||
Conn: p.conn,
|
||||
localAddr: p.addr,
|
||||
remoteAddr: raddr,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (p *tcpListener) Addr() net.Addr {
|
||||
return p.addr
|
||||
}
|
||||
|
||||
func (p *tcpListener) Close() error {
|
||||
return p.conn.Close()
|
||||
}
|
||||
|
||||
type tcpMuxListener struct {
|
||||
addr net.Addr
|
||||
session *mux.Session
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func (p *tcpMuxListener) Accept() (net.Conn, error) {
|
||||
cc, err := p.session.Accept()
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
conn, err := p.getPeerConn(cc)
|
||||
if err != nil {
|
||||
cc.Close()
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
|
||||
func (p *tcpMuxListener) getPeerConn(conn net.Conn) (net.Conn, error) {
|
||||
// second reply, peer connected
|
||||
rep, err := gosocks5.ReadReply(conn)
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
p.logger.Debug(rep)
|
||||
|
||||
if rep.Rep != gosocks5.Succeeded {
|
||||
err = fmt.Errorf("peer connect failed")
|
||||
return nil, err
|
||||
}
|
||||
|
||||
raddr, err := net.ResolveTCPAddr("tcp", rep.Addr.String())
|
||||
if err != nil {
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return &bindConn{
|
||||
Conn: conn,
|
||||
localAddr: p.addr,
|
||||
remoteAddr: raddr,
|
||||
}, nil
|
||||
}
|
||||
|
||||
func (p *tcpMuxListener) Addr() net.Addr {
|
||||
return p.addr
|
||||
}
|
||||
|
||||
func (p *tcpMuxListener) Close() error {
|
||||
return p.session.Close()
|
||||
}
|
||||
@@ -1,24 +0,0 @@
|
||||
package v5
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
connectTimeout time.Duration
|
||||
noTLS bool
|
||||
}
|
||||
|
||||
func (c *socks5Connector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
connectTimeout = "timeout"
|
||||
noTLS = "notls"
|
||||
)
|
||||
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
c.md.noTLS = mdata.GetBool(md, noTLS)
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,73 +0,0 @@
|
||||
package v5
|
||||
|
||||
import (
|
||||
"crypto/tls"
|
||||
"net"
|
||||
"net/url"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/logger"
|
||||
)
|
||||
|
||||
type clientSelector struct {
|
||||
methods []uint8
|
||||
User *url.Userinfo
|
||||
TLSConfig *tls.Config
|
||||
logger logger.Logger
|
||||
}
|
||||
|
||||
func (s *clientSelector) Methods() []uint8 {
|
||||
s.logger.Debug("methods: ", s.methods)
|
||||
return s.methods
|
||||
}
|
||||
|
||||
func (s *clientSelector) AddMethod(methods ...uint8) {
|
||||
s.methods = append(s.methods, methods...)
|
||||
}
|
||||
|
||||
func (s *clientSelector) Select(methods ...uint8) (method uint8) {
|
||||
return
|
||||
}
|
||||
|
||||
func (s *clientSelector) OnSelected(method uint8, conn net.Conn) (net.Conn, error) {
|
||||
s.logger.Debug("method selected: ", method)
|
||||
|
||||
switch method {
|
||||
case socks.MethodTLS:
|
||||
conn = tls.Client(conn, s.TLSConfig)
|
||||
|
||||
case gosocks5.MethodUserPass, socks.MethodTLSAuth:
|
||||
if method == socks.MethodTLSAuth {
|
||||
conn = tls.Client(conn, s.TLSConfig)
|
||||
}
|
||||
|
||||
var username, password string
|
||||
if s.User != nil {
|
||||
username = s.User.Username()
|
||||
password, _ = s.User.Password()
|
||||
}
|
||||
|
||||
req := gosocks5.NewUserPassRequest(gosocks5.UserPassVer, username, password)
|
||||
if err := req.Write(conn); err != nil {
|
||||
s.logger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
s.logger.Debug(req)
|
||||
|
||||
resp, err := gosocks5.ReadUserPassResponse(conn)
|
||||
if err != nil {
|
||||
s.logger.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
s.logger.Debug(resp)
|
||||
|
||||
if resp.Status != gosocks5.Succeeded {
|
||||
return nil, gosocks5.ErrAuthFailure
|
||||
}
|
||||
case gosocks5.MethodNoAcceptable:
|
||||
return nil, gosocks5.ErrBadMethod
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
@@ -1,111 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gosocks5"
|
||||
"github.com/go-gost/gost/pkg/common/bufpool"
|
||||
"github.com/go-gost/gost/pkg/common/util/ss"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/shadowsocks/go-shadowsocks2/core"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("ss", NewConnector)
|
||||
}
|
||||
|
||||
type ssConnector struct {
|
||||
cipher core.Cipher
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &ssConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *ssConnector) Init(md md.Metadata) (err error) {
|
||||
if err = c.parseMetadata(md); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
if c.options.Auth != nil {
|
||||
method := c.options.Auth.Username()
|
||||
password, _ := c.options.Auth.Password()
|
||||
c.cipher, err = ss.ShadowCipher(method, password, c.md.key)
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *ssConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
switch network {
|
||||
case "tcp", "tcp4", "tcp6":
|
||||
if _, ok := conn.(net.PacketConn); ok {
|
||||
err := fmt.Errorf("tcp over udp is unsupported")
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
addr := gosocks5.Addr{}
|
||||
if err := addr.ParseFrom(address); err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
rawaddr := bufpool.Get(512)
|
||||
defer bufpool.Put(rawaddr)
|
||||
|
||||
n, err := addr.Encode(*rawaddr)
|
||||
if err != nil {
|
||||
log.Error("encoding addr: ", err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
if c.cipher != nil {
|
||||
conn = c.cipher.StreamConn(conn)
|
||||
}
|
||||
|
||||
var sc net.Conn
|
||||
if c.md.noDelay {
|
||||
sc = ss.ShadowConn(conn, nil)
|
||||
// write the addr at once.
|
||||
if _, err := sc.Write((*rawaddr)[:n]); err != nil {
|
||||
return nil, err
|
||||
}
|
||||
} else {
|
||||
// cache the header
|
||||
sc = ss.ShadowConn(conn, (*rawaddr)[:n])
|
||||
}
|
||||
|
||||
return sc, nil
|
||||
}
|
||||
@@ -1,27 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
key string
|
||||
connectTimeout time.Duration
|
||||
noDelay bool
|
||||
}
|
||||
|
||||
func (c *ssConnector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
key = "key"
|
||||
connectTimeout = "timeout"
|
||||
noDelay = "nodelay"
|
||||
)
|
||||
|
||||
c.md.key = mdata.GetString(md, key)
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
c.md.noDelay = mdata.GetBool(md, noDelay)
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,95 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"context"
|
||||
"fmt"
|
||||
"net"
|
||||
"time"
|
||||
|
||||
"github.com/go-gost/gost/pkg/common/util/socks"
|
||||
"github.com/go-gost/gost/pkg/common/util/ss"
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
"github.com/shadowsocks/go-shadowsocks2/core"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("ssu", NewConnector)
|
||||
}
|
||||
|
||||
type ssuConnector struct {
|
||||
cipher core.Cipher
|
||||
md metadata
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &ssuConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *ssuConnector) Init(md md.Metadata) (err error) {
|
||||
if err = c.parseMetadata(md); err != nil {
|
||||
return
|
||||
}
|
||||
|
||||
if c.options.Auth != nil {
|
||||
method := c.options.Auth.Username()
|
||||
password, _ := c.options.Auth.Password()
|
||||
c.cipher, err = ss.ShadowCipher(method, password, c.md.key)
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
|
||||
func (c *ssuConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
switch network {
|
||||
case "udp", "udp4", "udp6":
|
||||
default:
|
||||
err := fmt.Errorf("network %s is unsupported", network)
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
if c.md.connectTimeout > 0 {
|
||||
conn.SetDeadline(time.Now().Add(c.md.connectTimeout))
|
||||
defer conn.SetDeadline(time.Time{})
|
||||
}
|
||||
|
||||
taddr, _ := net.ResolveUDPAddr(network, address)
|
||||
if taddr == nil {
|
||||
taddr = &net.UDPAddr{}
|
||||
}
|
||||
|
||||
pc, ok := conn.(net.PacketConn)
|
||||
if ok {
|
||||
if c.cipher != nil {
|
||||
pc = c.cipher.PacketConn(pc)
|
||||
}
|
||||
|
||||
// standard UDP relay
|
||||
return ss.UDPClientConn(pc, conn.RemoteAddr(), taddr, c.md.bufferSize), nil
|
||||
}
|
||||
|
||||
if c.cipher != nil {
|
||||
conn = ss.ShadowConn(c.cipher.StreamConn(conn), nil)
|
||||
}
|
||||
|
||||
// UDP over TCP
|
||||
return socks.UDPTunClientConn(conn, taddr), nil
|
||||
}
|
||||
@@ -1,33 +0,0 @@
|
||||
package ss
|
||||
|
||||
import (
|
||||
"math"
|
||||
"time"
|
||||
|
||||
mdata "github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
type metadata struct {
|
||||
key string
|
||||
connectTimeout time.Duration
|
||||
bufferSize int
|
||||
}
|
||||
|
||||
func (c *ssuConnector) parseMetadata(md mdata.Metadata) (err error) {
|
||||
const (
|
||||
key = "key"
|
||||
connectTimeout = "timeout"
|
||||
bufferSize = "bufferSize" // udp buffer size
|
||||
)
|
||||
|
||||
c.md.key = mdata.GetString(md, key)
|
||||
c.md.connectTimeout = mdata.GetDuration(md, connectTimeout)
|
||||
|
||||
if bs := mdata.GetInt(md, bufferSize); bs > 0 {
|
||||
c.md.bufferSize = int(math.Min(math.Max(float64(bs), 512), 64*1024))
|
||||
} else {
|
||||
c.md.bufferSize = 1024
|
||||
}
|
||||
|
||||
return
|
||||
}
|
||||
@@ -1,80 +0,0 @@
|
||||
package sshd
|
||||
|
||||
import (
|
||||
"context"
|
||||
"errors"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/connector"
|
||||
ssh_util "github.com/go-gost/gost/pkg/internal/util/ssh"
|
||||
md "github.com/go-gost/gost/pkg/metadata"
|
||||
"github.com/go-gost/gost/pkg/registry"
|
||||
)
|
||||
|
||||
func init() {
|
||||
registry.RegiserConnector("sshd", NewConnector)
|
||||
}
|
||||
|
||||
type sshdConnector struct {
|
||||
options connector.Options
|
||||
}
|
||||
|
||||
func NewConnector(opts ...connector.Option) connector.Connector {
|
||||
options := connector.Options{}
|
||||
for _, opt := range opts {
|
||||
opt(&options)
|
||||
}
|
||||
|
||||
return &sshdConnector{
|
||||
options: options,
|
||||
}
|
||||
}
|
||||
|
||||
func (c *sshdConnector) Init(md md.Metadata) (err error) {
|
||||
return nil
|
||||
}
|
||||
|
||||
func (c *sshdConnector) Connect(ctx context.Context, conn net.Conn, network, address string, opts ...connector.ConnectOption) (net.Conn, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("connect %s/%s", address, network)
|
||||
|
||||
cc, ok := conn.(*ssh_util.ClientConn)
|
||||
if !ok {
|
||||
return nil, errors.New("ssh: invalid connection")
|
||||
}
|
||||
|
||||
conn, err := cc.Client().Dial(network, address)
|
||||
if err != nil {
|
||||
log.Error(err)
|
||||
return nil, err
|
||||
}
|
||||
|
||||
return conn, nil
|
||||
}
|
||||
|
||||
// Bind implements connector.Binder.
|
||||
func (c *sshdConnector) Bind(ctx context.Context, conn net.Conn, network, address string, opts ...connector.BindOption) (net.Listener, error) {
|
||||
log := c.options.Logger.WithFields(map[string]interface{}{
|
||||
"remote": conn.RemoteAddr().String(),
|
||||
"local": conn.LocalAddr().String(),
|
||||
"network": network,
|
||||
"address": address,
|
||||
})
|
||||
log.Infof("bind on %s/%s", address, network)
|
||||
|
||||
cc, ok := conn.(*ssh_util.ClientConn)
|
||||
if !ok {
|
||||
return nil, errors.New("ssh: invalid connection")
|
||||
}
|
||||
|
||||
if host, port, _ := net.SplitHostPort(address); host == "" {
|
||||
address = net.JoinHostPort("0.0.0.0", port)
|
||||
}
|
||||
|
||||
return cc.Client().Listen(network, address)
|
||||
}
|
||||
@@ -1,22 +0,0 @@
|
||||
package dialer
|
||||
|
||||
import (
|
||||
"context"
|
||||
"net"
|
||||
|
||||
"github.com/go-gost/gost/pkg/metadata"
|
||||
)
|
||||
|
||||
// Transporter is responsible for dialing to the proxy server.
|
||||
type Dialer interface {
|
||||
Init(metadata.Metadata) error
|
||||
Dial(ctx context.Context, addr string, opts ...DialOption) (net.Conn, error)
|
||||
}
|
||||
|
||||
type Handshaker interface {
|
||||
Handshake(ctx context.Context, conn net.Conn, opts ...HandshakeOption) (net.Conn, error)
|
||||
}
|
||||
|
||||
type Multiplexer interface {
|
||||
Multiplex() bool
|
||||
}
|
||||
@@ -1,21 +0,0 @@
|
||||
package ftcp
|
||||
|
||||
import "net"
|
||||
|
||||
type fakeTCPConn struct {
|
||||
raddr net.Addr
|
||||
net.PacketConn
|
||||
}
|
||||
|
||||
func (c *fakeTCPConn) Read(b []byte) (n int, err error) {
|
||||
n, _, err = c.ReadFrom(b)
|
||||
return
|
||||
}
|
||||
|
||||
func (c *fakeTCPConn) Write(b []byte) (n int, err error) {
|
||||
return c.WriteTo(b, c.raddr)
|
||||
}
|
||||
|
||||
func (c *fakeTCPConn) RemoteAddr() net.Addr {
|
||||
return c.raddr
|
||||
}
|
||||
Some files were not shown because too many files have changed in this diff Show More
Reference in New Issue
Block a user